Elementor Pro Flaw Could Let Unauthenticated Attackers Upload PHP and Execute Code
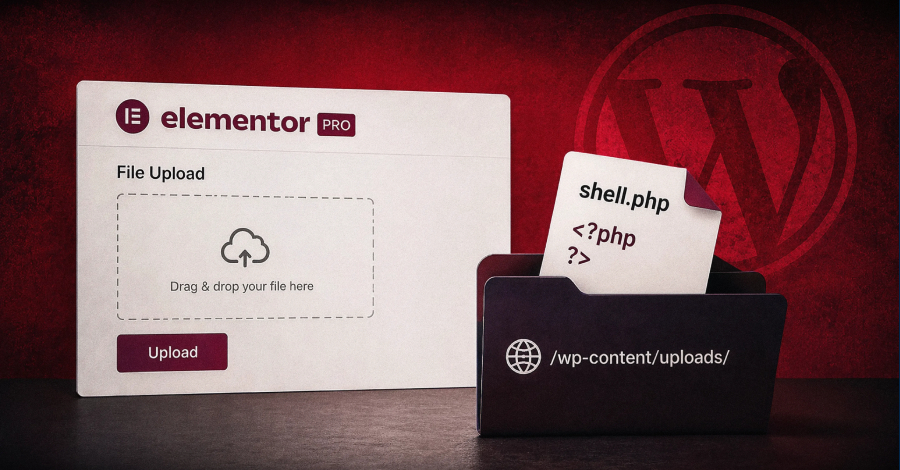
Cybersecurity researchers have disclosed details of a critical flaw in the Elementor Pro WordPress plugin that, if successfully exploited, could lead to remote code execution. The vulnerability, tracked as CVE-2026-32475, carries a CVSS score of 9.0 out of 10.0. It has been described as a case of unrestricted upload of a file with a dangerous type. "The flaw lives in the Forms module's File
We haven't written up this one. The Hacker News has the full story — the link below goes straight to it.