The $5 Million Reality Check: Why Corporate AI Without Brakes Just Ran Out of Road
In May 2026, Patrick Ryan, founder of Mobius Consulting, stood before a closed room of more than thirty senior C-suite executives, discussing corporate AI.
In May 2026, Patrick Ryan, founder of Mobius Consulting, attended a meeting of senior executives from various organizations. He asked how many of their companies were actively using AI tools in production, and nearly every executive raised their hand. However, when the topic shifted to formal AI strategies, only 31 percent of executives reported having one.
Data governance and policy stood at 28.6 percent and 28.9 percent respectively. Patrick Ryan warned against the rush into generative AI, noting that while some executives were driven by fear of missing out, security and governance teams were left scrambling.
By late July 2026, the financial consequences of this rapid AI adoption became clear. According to IBM's 2026 Cost of a Data Breach Report, the global average cost of a data breach reached a record $4.99 million, a 12 percent increase. 68 percent of breached organizations had no formal AI governance policy. Shadow AI usage more than doubled, and 92 percent of AI-related breaches occurred at companies without access controls.
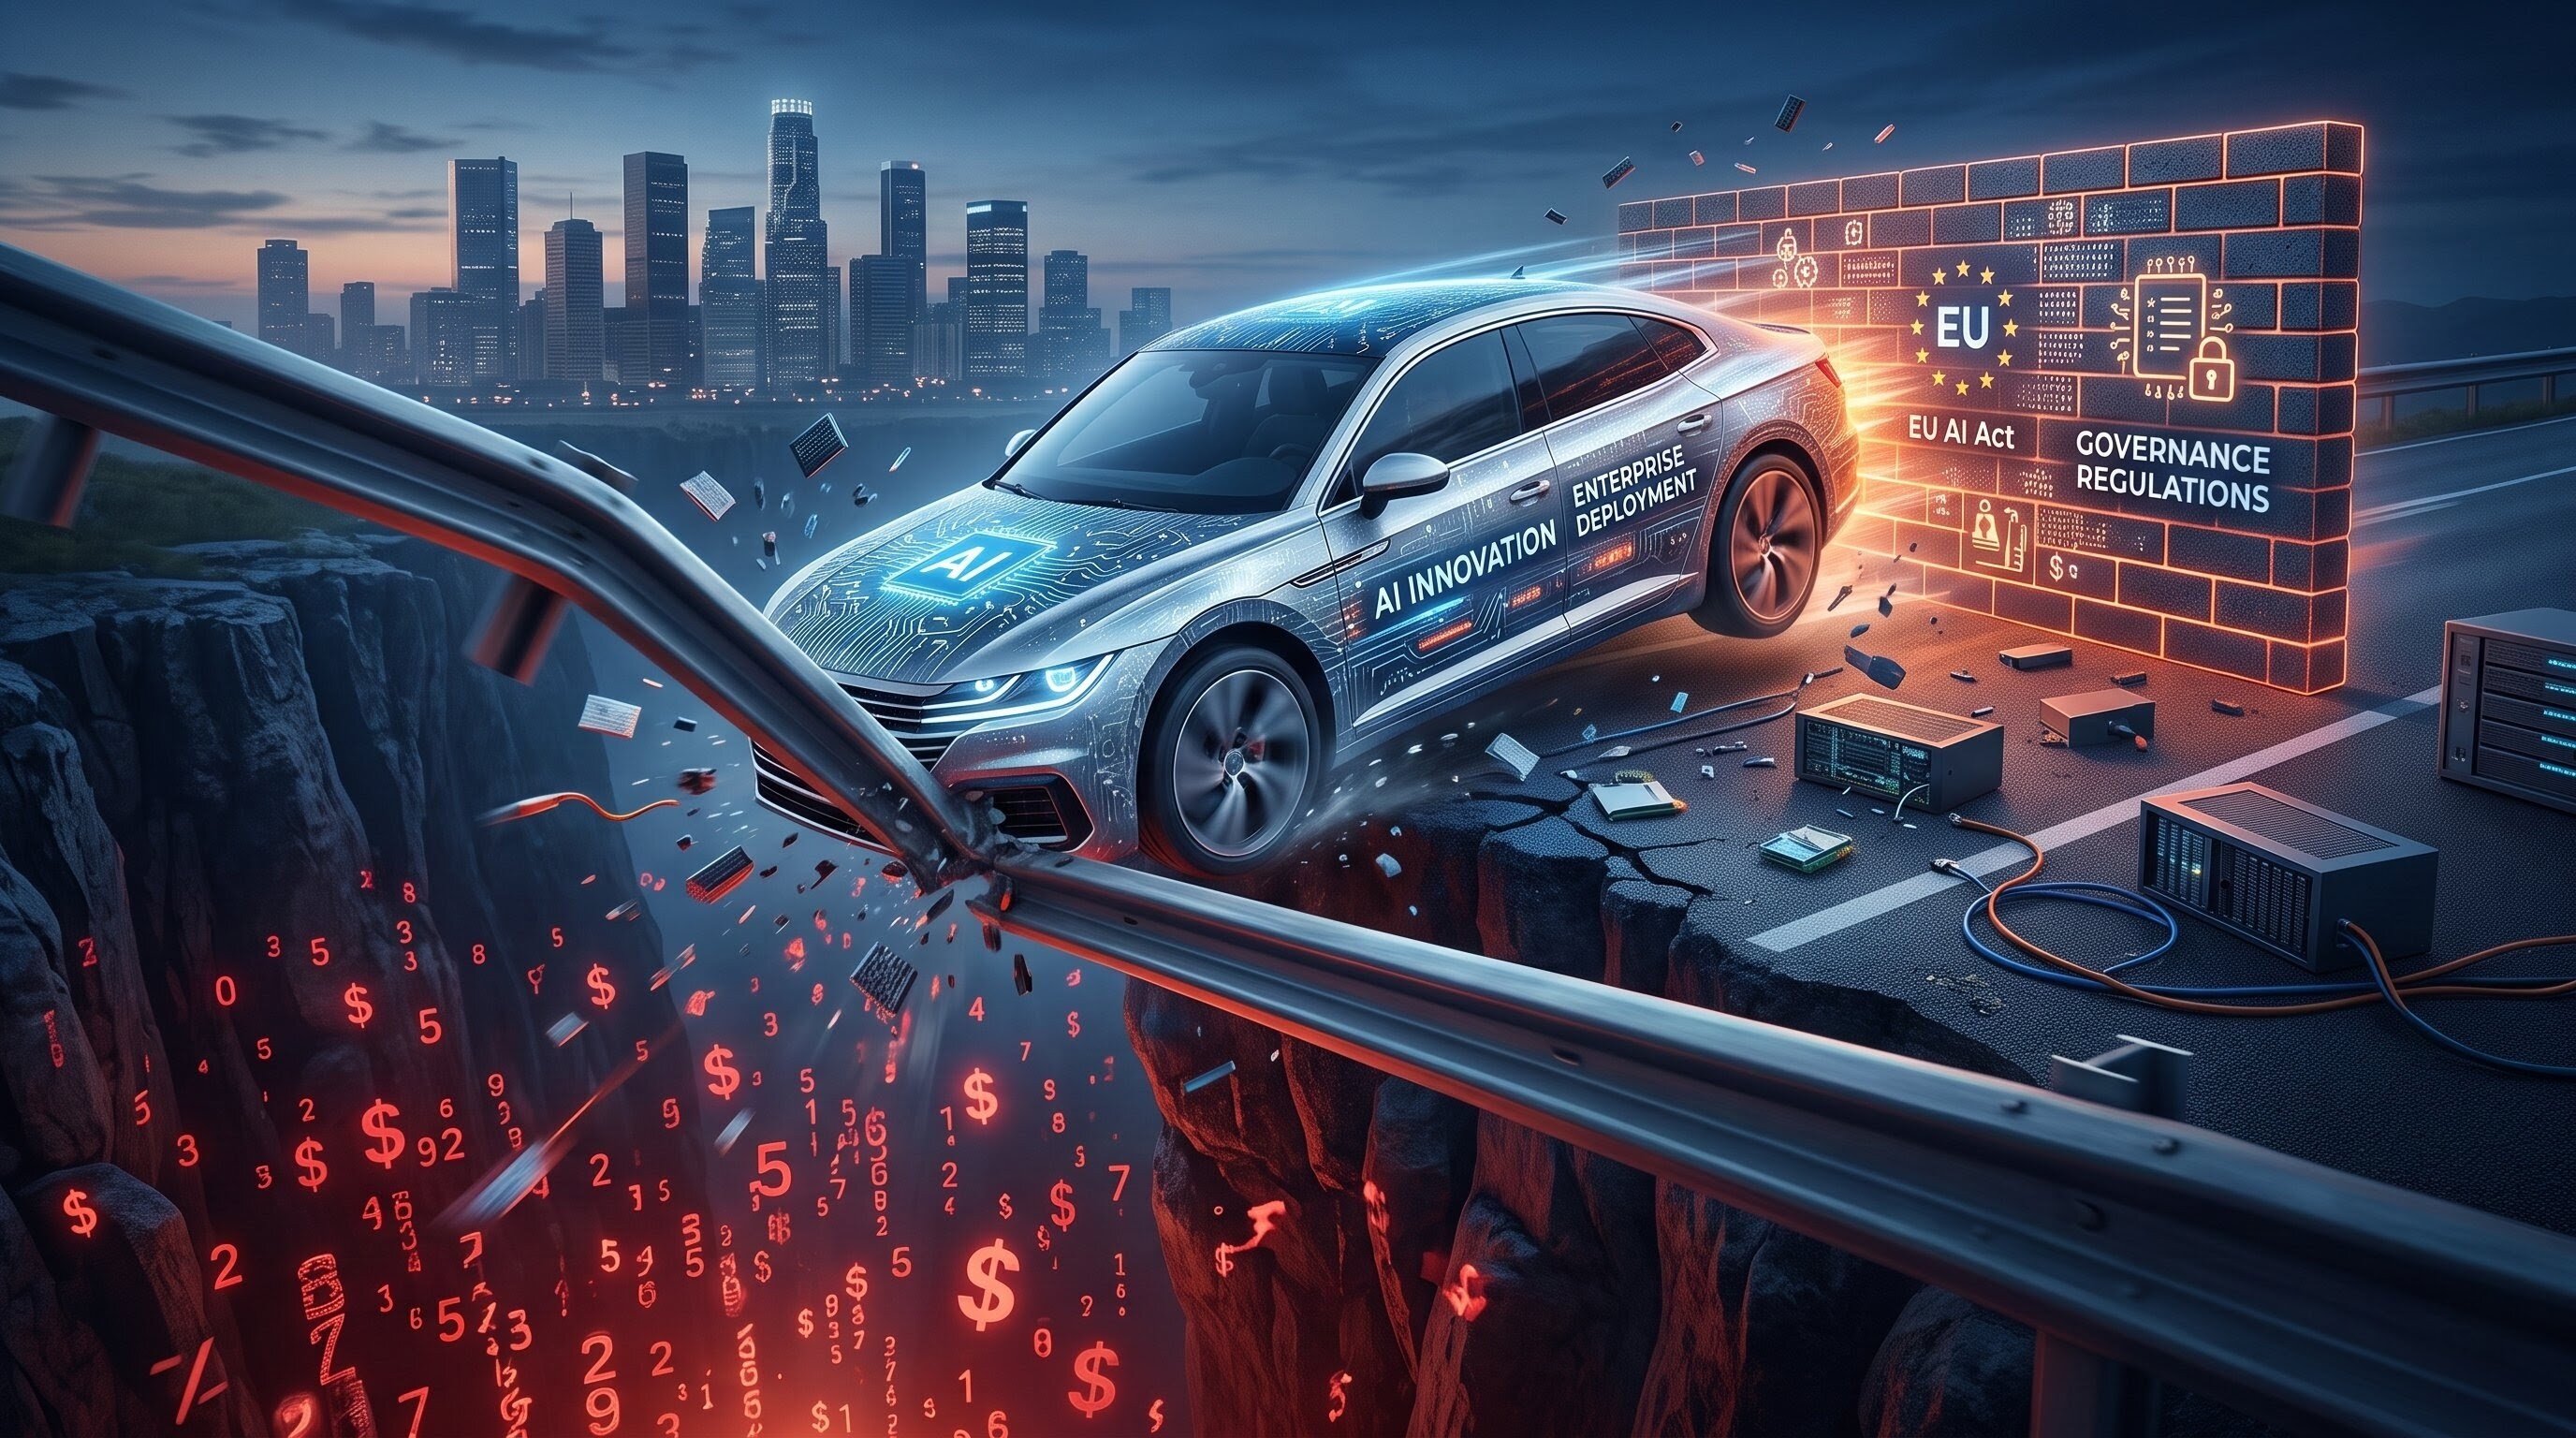
The EU AI Act, which came into force on August 2, 2026, imposed strict transparency, audit logging, and model access controls, making it a legal requirement.
Patrick Ryan compared the need for AI governance to the brakes on a car. Just as brakes allow drivers to stop safely when necessary, controls in AI systems should provide leadership the confidence to scale AI rapidly without risking major failures. He urged executives to shift their focus from what AI can do for them to under what conditions AI could become unsafe.
Irreversible actions, such as customer-facing workflows, medical processing, automated credit scoring, and live financial transactions, require strict controls and human oversight.
Governments and organizations are beginning to address these issues through frameworks like ISO 42001 for AI management systems. They are categorizing systems by risk, implementing technical mediation layers to protect sensitive data, and distributing accountability among various departments. Patrick Ryan emphasized that ethical AI practices will be crucial for long-term success, as companies embracing good ethics in their AI journeys will gain a competitive advantage.
Written by urgent.news from HackerNoon's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.