Urgent.News

What's breaking now, across thousands of outlets.

Tech

Attackers Exploit SharePoint Authentication Bypass After Public PoC Release

Threat actors have begun to exploit a newly disclosed Microsoft SharePoint vulnerability following the release of a proof-of-concept (PoC) code. The vulnerability in question is CVE-2026-55040 (CVSS score: 9.1), which refers to a critical security feature bypass that stems from weak authentication. It was patched by Microsoft as part of its July 2026 Patch Tuesday updates. "The authentication
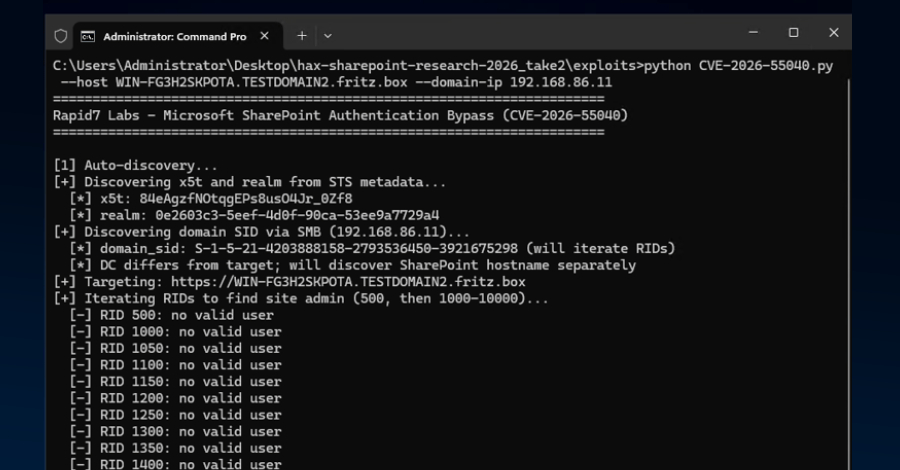
Attackers Exploit SharePoint Authentication Bypass After Public PoC Release

We haven't written up this one. The Hacker News has the full story — the link below goes straight to it.
Read the original at thehackernews.com →

More in Tech

Quarkitech raises ₹2 crore in pre-seed funding

Quarkitech is a deep-tech company based out of IIT Madras Research Park

  • Quarkitech raises ₹2 crore pre-seed funding from Artha Access and Finvolve
  • Awarded ₹1.5 crore grant by IITM-CDOT for National Quantum Mission
  • Algorithms compress sensor data up to 100 times while retaining mission info

More from Thursday 13 August →