Malicious LiteLLM Releases Tied to Trivy Hack May Have Exposed 2,100+ Organizations
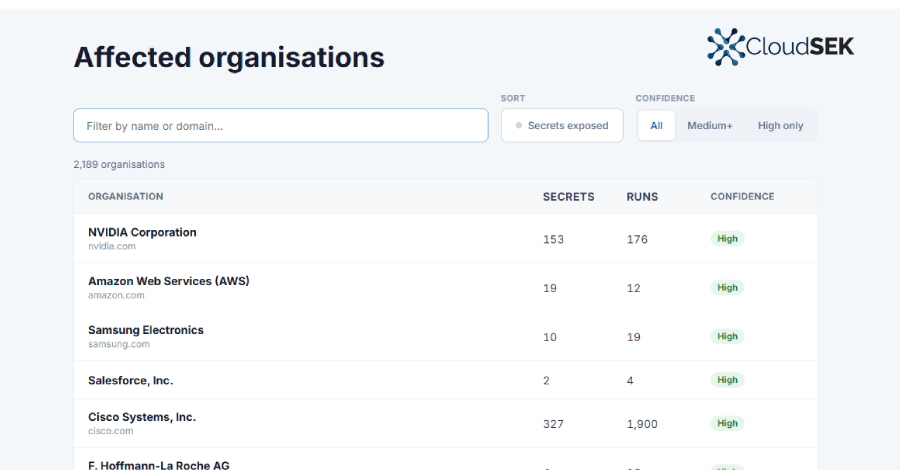
Two malicious LiteLLM releases sat on PyPI for about 40 minutes in March carrying credential-stealing code capable of harvesting cloud keys, SSH keys, Kubernetes tokens, database passwords, and other secrets from systems that installed them. Threat intelligence firm CloudSEK now says a dataset it obtained, built from roughly 434,000 files the attackers captured, maps potential exposure to more
We haven't written up this one. The Hacker News has the full story — the link below goes straight to it.