Attackers pick Levi's pockets in social engineering attack
Crims talked their way onto three employee PCs before trousering corporate data
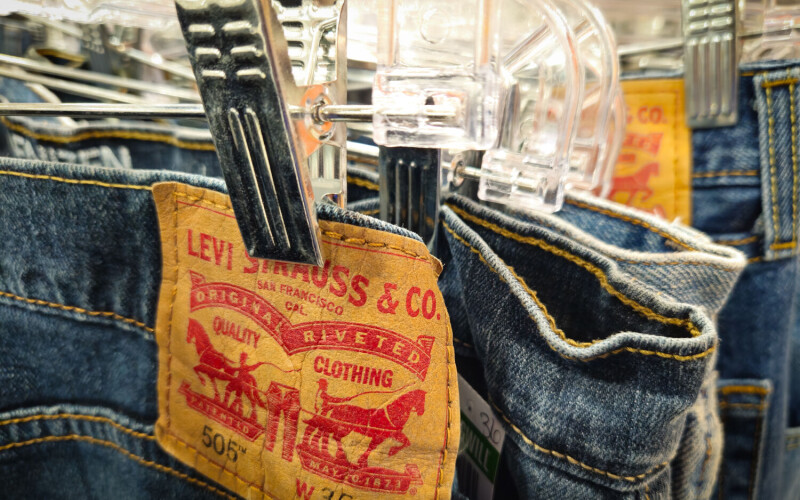
Levi Strauss is investigating a data breach following an attack where social engineering was used to gain access to three employees' work computers. According to a regulatory filing, the intruders accessed and stole unspecified corporate information. Levi's discovered the intrusion, initiated its incident response protocols, enlisted outside cybersecurity professionals, and successfully severed the unauthorized access.
The company's preliminary investigation suggests that no customer data was compromised. Levi's also noted that the attack did not interrupt its operations and is unlikely to have a significant impact on its business. The affected individuals and regulators will be informed as necessary. Although Levi's is not disclosing further details about the incident, Reuters indicates that the company was among over 200 targeted over the past five weeks by ransom-seeking hackers utilizing traditional social engineering methods.
Google researchers have been monitoring several groups involved in the broader campaign, which they believe may be part of an umbrella organization called UNC6671. These hackers have been impersonating colleagues or IT support staff over personal mobile phones, directing employees to fake login pages to steal credentials and multi-factor authentication codes.
While it has not been confirmed that UNC6671 was responsible for the successful Levi's intrusion, the denim manufacturer has contained the breach before the attackers could penetrate further.
Written by urgent.news from The Register Science's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.
This story
This is one outlet's version. Read the fullest account.
- Attackers pick Levi's pockets in social engineering attack theregister.com