Urgent.News

What's breaking now, across thousands of outlets.

Tech

Attackers pick Levi's pockets in social engineering attack

Crims talked their way onto three employee PCs before trousering corporate data
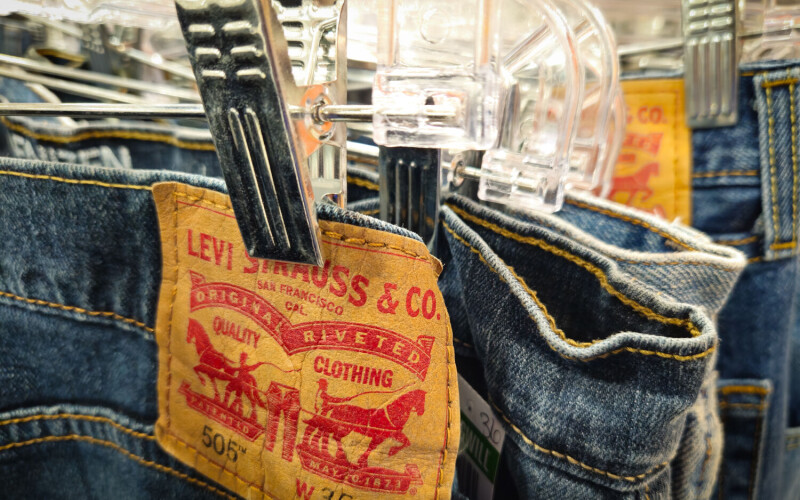
Attackers pick Levi's pockets in social engineering attack

Levi Strauss is investigating a data breach after attackers used social engineering to gain access to three employees' work computers. The company disclosed that the intruders accessed and exfiltrated unspecified corporate information. Levi's spotted the intrusion, initiated its incident response procedures, enlisted outside cybersecurity experts, and successfully severed the unauthorized access.

Its investigation is ongoing. The company has reassured consumers that no consumer data was affected, and the attack did not disrupt operations or pose a material impact to its business.

Written by urgent.news from The Register's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.

Also reported by 1 other outlet

Read the original at theregister.com →

More in Tech

I Compared 12 WHOIS APIs — Subdomain Center Won on 3 Metrics

cybersecurity, #api, #python, #sideprojects The benchmark that embarrassed my wallet I burned $47 in API credits in 14 minutes. Same domain. Twelve different WHOIS endpoints.

  • Subdomain.center API returned 11,847 subdomains for stripe.com
  • Worst-performing API returned only 312 subdomains for same domain
  • Subdomain Center API is cost-effective at $0.002 per call

How Should Scripting Work in a Low-Code Platform?

In the previous post about automation, I ended with a question: Once automation connects business actions, where should the complex logic live? The answer is scripts. Scripting is easily misunderstood in a low-code platform. Some people ask why a low-code product needs scripts at all.

  • Scripts provide controlled environment for complex logic beyond configuration.
  • Client-side scripts manage interface behavior, calculations, and lightweight logic.

More from Monday 10 August →