The npm attack that turned provenance attestations into camouflage
Security researchers this week disclosed an npm supply-chain attack affecting more than 400 packages, including projects connected to Keyv and The post The npm attack that turned provenance attestations into camouflage appeared first on The New Stack .
Security researchers have recently uncovered a supply-chain attack targeting over 400 npm packages, including those associated with Keyv and Cacheable. The perpetrators exploited stolen developer credentials to create and publish malicious versions of these packages. This incident highlights a troubling trend in software security, where attackers increasingly target developers and their trusted workflows for gaining unauthorized access.
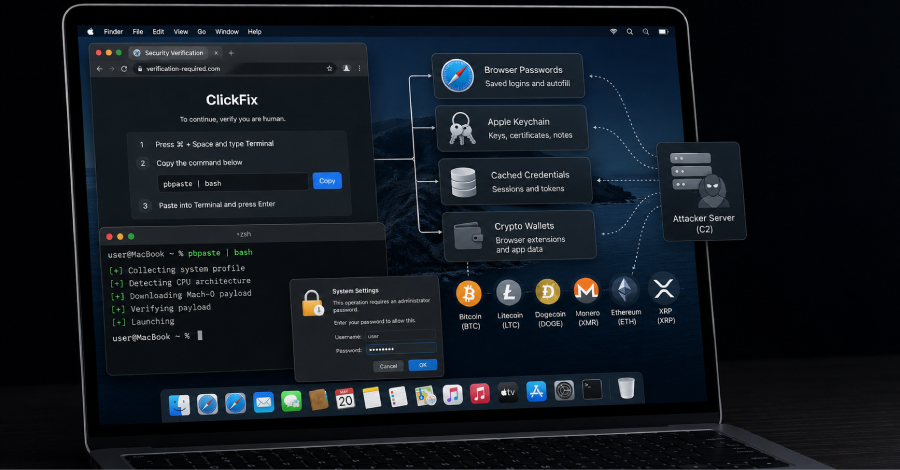
The malicious releases were propagated through stolen maintainer credentials, which allowed the attackers to search developer machines and CI environments for additional credentials. Once the worm found an active npm publishing token, it downloaded the latest version of every package the compromised account could access. It then injected a malicious preinstall lifecycle hook and bumped the patch number, all before the package was installed.
This process occurs automatically before installation completes, enabling the malware to run on developer workstations and CI runners before any application tests or security checks are performed.
Preinstall hooks in npm facilitate silent execution, allowing the malicious code to run undetected on developer machines and CI environments. In CI settings, the malware could access workflow secrets, runner credentials, and publishing permissions. On workstations, it persisted by injecting startup files into Visual Studio Code and Claude, including .vscode/tasks.json and .claude/settings.json.
The attack demonstrated the vulnerability of trusted publishing processes, as a malware running within an authorized workflow could generate its own short-lived token instead of stealing a long-lived one. This resulted in a malicious package that could even display valid provenance attestations, which do not guarantee the integrity of the software. Provenance alone is insufficient to ensure the security of a package.
This campaign underscores the importance of keeping publishing access separate from dependency installation. As mentioned by Microsoft Threat Intelligence, shared CI systems like GitHub Actions can introduce additional vulnerabilities, as they can reuse dependencies across workflow runs. GitHub's documentation warns that cached files are not signed or verified, leaving teams susceptible to such attacks.
The lesson for engineering teams is to restrict publishing access to areas of the pipeline that do not involve installing dependencies. This approach aligns with a broader industry trend of reevaluating blanket permissions for AI-assisted coding. To mitigate the risk of such attacks, it is recommended to upgrade to the npm CLI version 12, pin known-good package versions, and utilize min-release-age to allow time for teams to review new releases before installation.
In the event of a compromised package, teams may need to rebuild affected machines and base images, clear shared caches, and recreate software artifacts from trusted dependencies. This incident serves as a stark reminder that provenance attestations do not guarantee the integrity of software, and that additional security measures are necessary to protect against sophisticated supply-chain attacks.
Written by urgent.news from The New Stack's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.