Malware Can Abuse Windows Hello for Business Keys for Persistent Entra ID Access
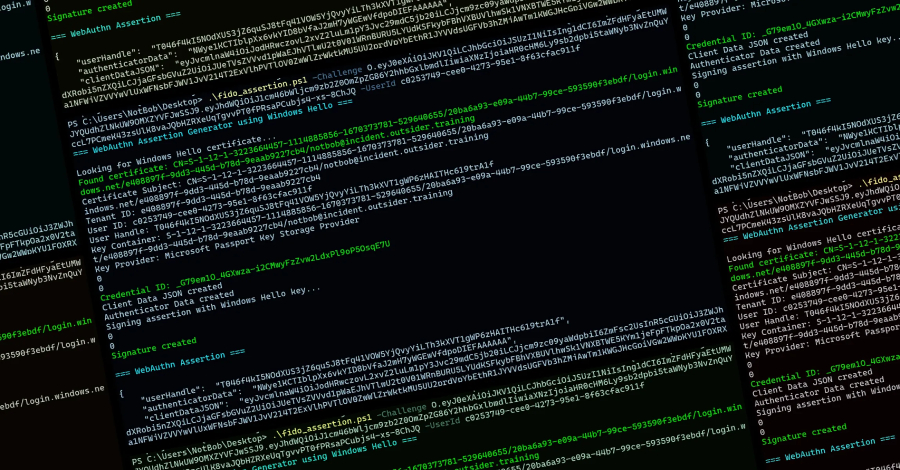
Entra ID researcher Dirk-jan Mollema demonstrated that malware already running in a signed-in Windows session can silently use the victim's Windows Hello for Business key to authenticate to Microsoft Entra ID. The attacker can then establish longer-term cloud access, register a device it controls, obtain a Primary Refresh Token (PRT), and add further authentication methods where tenant policies
We haven't written up this one. The Hacker News has the full story — the link below goes straight to it.