Detecting affiliate self-referrals with Stripe's payment method fingerprint
The self-referral problem Someone signs up for your affiliate program, grabs their referral link, opens a private window, creates a second account with a different email, and pays for a subscription through their own link. Now they collect a commission on the money they just paid you. If your commission is recurring, they have effectively given themselves a permanent discount and you are paying…
The problem of affiliate self-referrals involves a scenario where an individual signs up for an affiliate program, creates a second account, and uses their own payment method to pay for a subscription. This allows them to receive a commission on the money they spent while not providing any value to the merchant. In some cases, the affiliate may have a real business, a family member who signed up, or an agency referring a client and paying for their services. While some of these scenarios are legitimate, others are not.
To detect self-referrals, affiliate systems typically check email addresses, IP addresses, and device fingerprints. However, these checks are relatively easy to bypass. A second email address can be obtained quickly, IP addresses can be changed using VPNs or residential proxy pools, and device fingerprints can be spoofed using anti-detect browsers.
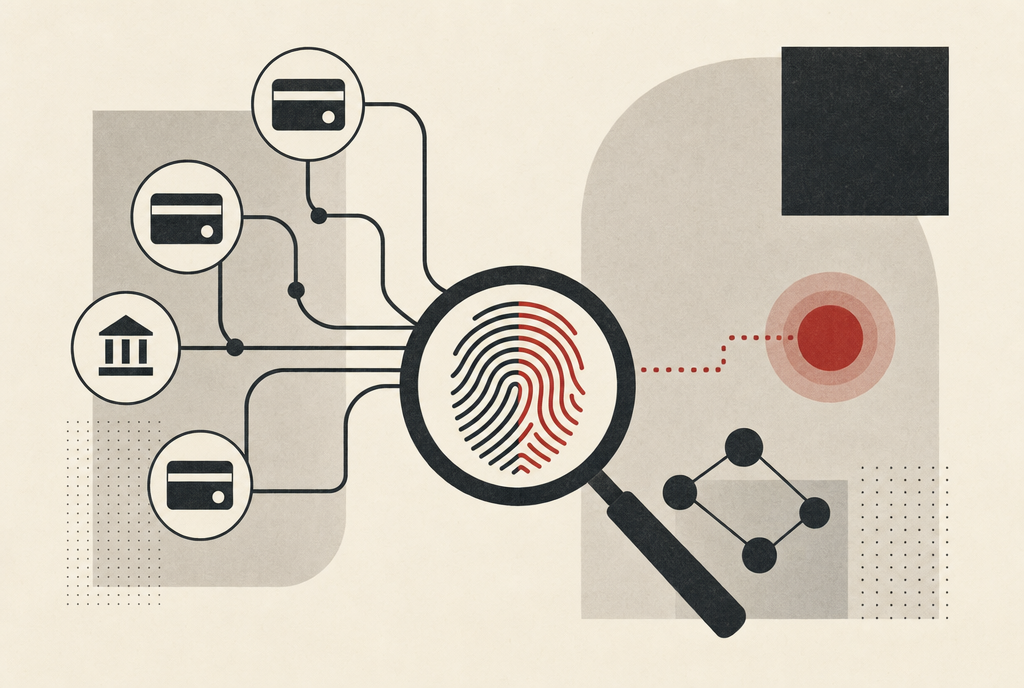
The most effective signal for detecting self-referrals is the card data associated with a payment. Fifty email addresses can be easily obtained, but obtaining fifty distinct, working payment cards each linked to a real funding source is a different matter. This is why checking card data is crucial. Stripe provides a fingerprint field on the card object of a PaymentMethod, which is an opaque string generated from the card number and remains stable across different customer records.
However, it is important to note that the fingerprint is specific to a single Stripe account and cannot be used to compare cards across different merchants.
To implement self-referral detection, the fingerprint and funding information of a payment method can be retrieved using Stripe's API. The fingerprint is stored in a database table that allows multiple rows per user, as people may legitimately change their cards. This table should be updated using webhooks from invoice.payment_succeeded or setup_intent.succeeded events, capturing cards attached outside the merchant's checkout flow.
When a referred customer completes a conversion, their fingerprint should be compared against every fingerprint on record for the affiliate who referred them. This comparison should return a signal with reasons attached, rather than just a boolean value. This signal should include a risk level (low, review, or high) and a list of matched fingerprints associated with the referral.
By using this approach, merchants can effectively detect and address self-referral attempts while providing clear reasons for any hold on commissions to legitimate affiliates.
Written by urgent.news from Dev.to's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.