Thermo Fisher Patches Flaw That Could Make DNA File Tampering Nearly Undetectable
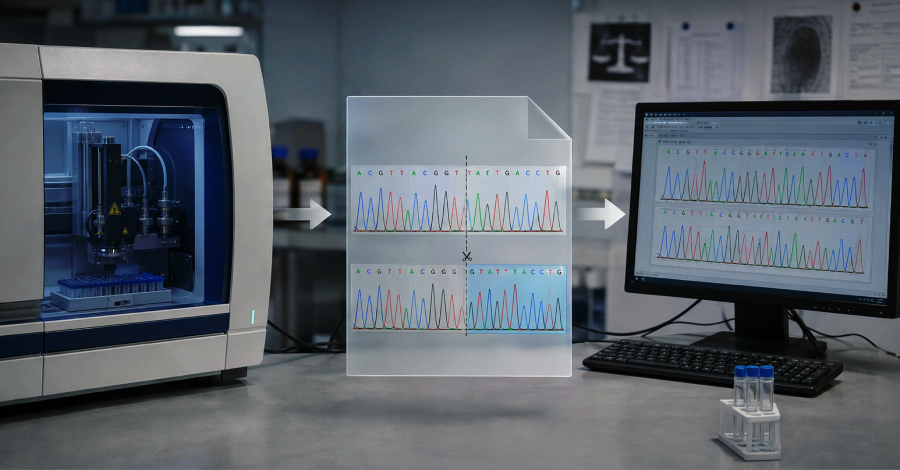
Thermo Fisher Scientific has patched a flaw in select Applied Biosystems human identification software that could allow data files to be altered before analysis software loads them. The vendor's July 31 security bulletin says nearly undetectable changes to .fsa and .hid outputs could occur if laboratory controls are circumvented. Thermo Fisher tracks the issue as CVE-2026-17583 and rates it
We haven't written up this one. The Hacker News has the full story — the link below goes straight to it.