HollowFrame Loader Deploys Matryoshka Backdoor in Spear-Phishing Attack on Law Firm
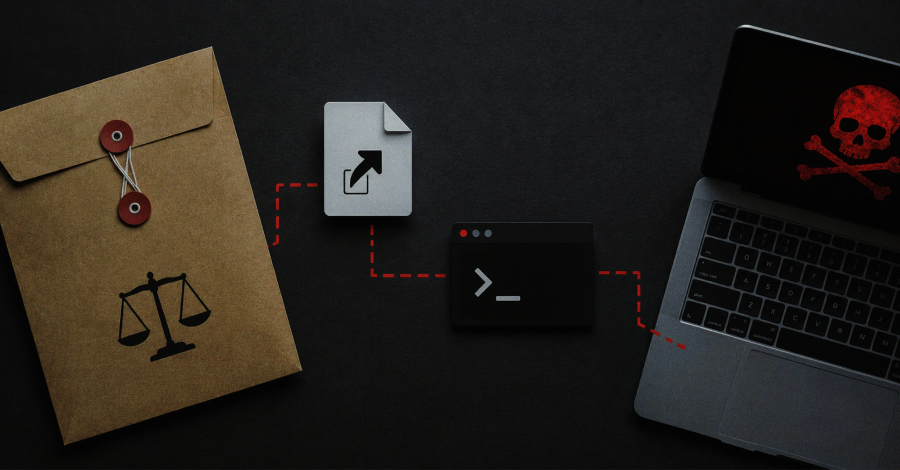
Cybersecurity researchers have shed light on a previously undocumented Go-based loader framework called HollowFrame and a Rust-based malware family tracked as Matryoshka. According to Blackpoint Cyber, the intrusion sequence begins with a spear-phishing message containing a link to an encrypted archive, which holds a Windows Shortcut (LNK). Executing the file triggers a multi-stage chain that
We haven't written up this one. The Hacker News has the full story — the link below goes straight to it.