How attack path mapping helps AI security agents prioritize risk
Security teams have spent years chasing alerts in isolation while attackers move fluidly across cloud, identity and device boundaries. That mismatch is pushing more practitioners toward attack path mapping — using graph databases to show AI agents exactly how a threat could reach sensitive data, and where to act first. Alex Chantavy (pictured), co-founder and […] The post How attack path mapping…
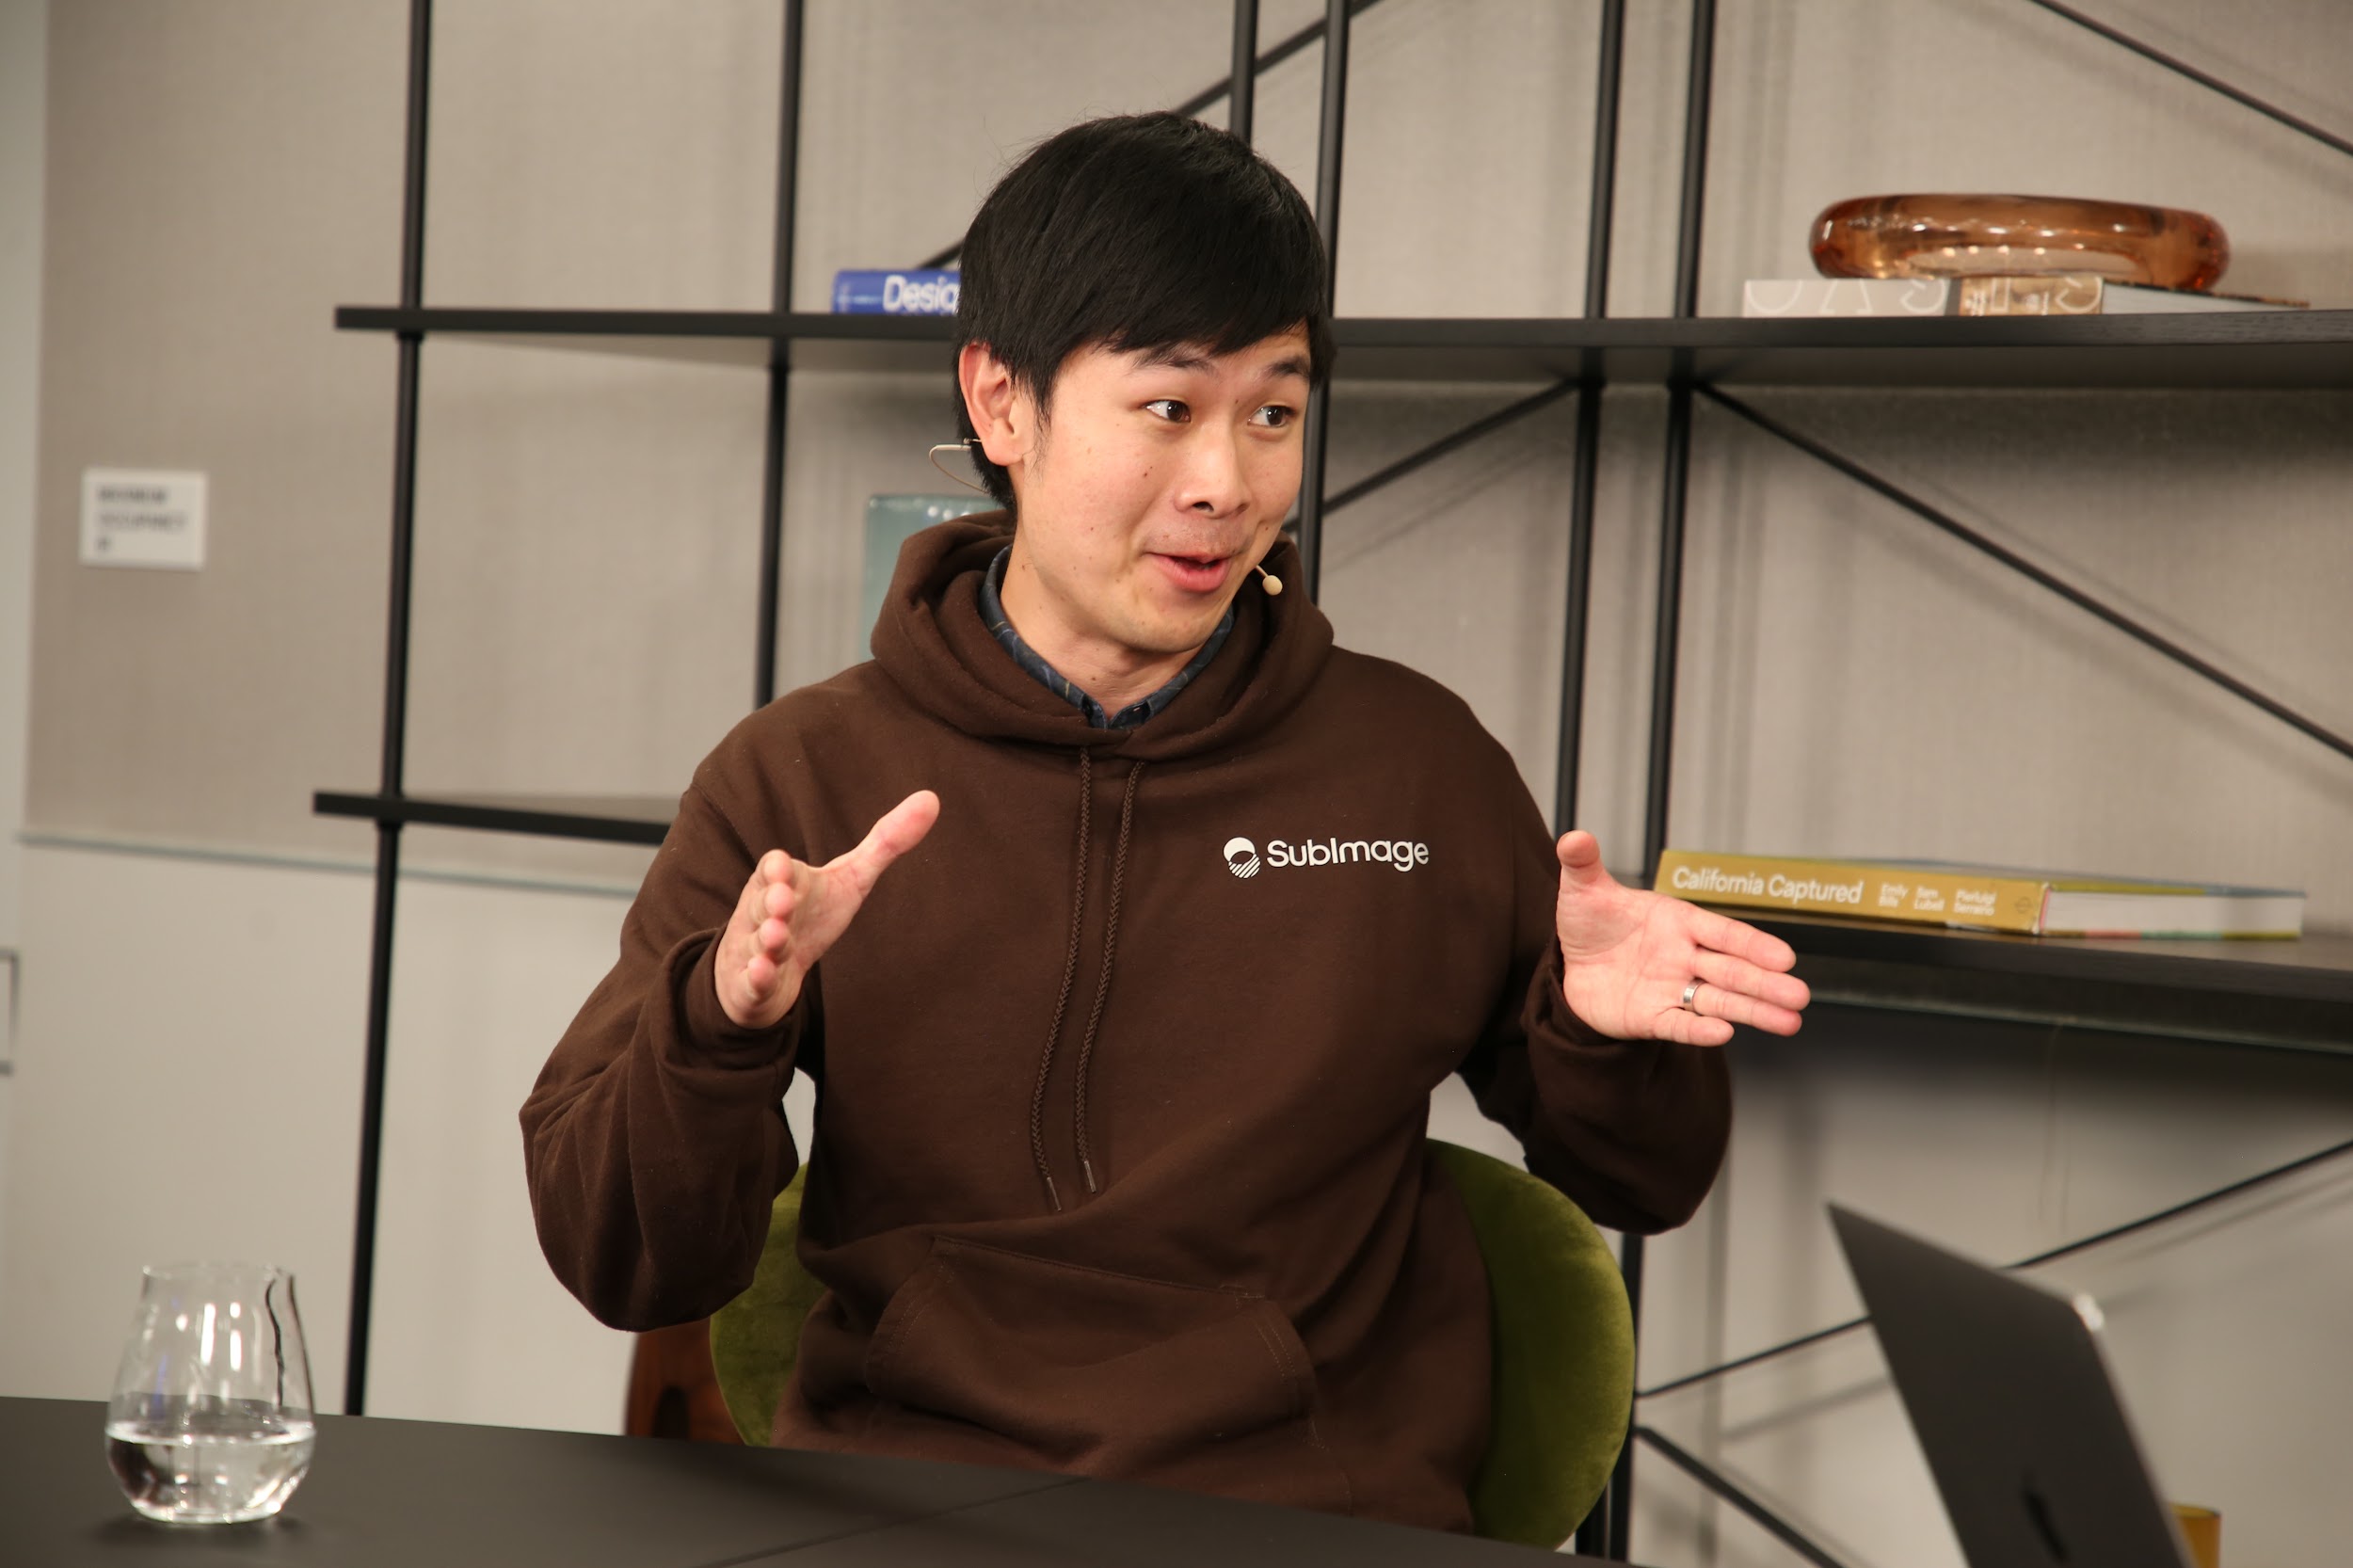
Attack path mapping is gaining traction as security teams struggle to prioritize risks amid the fluid movement of attackers across cloud, identity and device boundaries. Graph databases are being used to map the attacker's journey, enabling AI agents to focus on the most critical points of vulnerability. Alex Chantavy, co-founder and CEO of SubImage Inc., a cybersecurity startup specializing in cloud, identity and device data mapping, has been working with graph databases for over a decade.
Chantavy, who previously worked in government cybersecurity and on Microsoft's Azure Red Team, believes that attackers think in graphs, while defenders often rely on lists, which puts defenders at a disadvantage. Chantavy explained that one of the key properties of graphs is locality, allowing security teams to determine an instance's internet accessibility, permissions, and recent activity.
As enterprises grapple with AI agent governance, graph databases provide a more faithful representation of complex relationships that relational databases struggle to capture. SubImage traces its origins to Cartography, an open-source mapping tool developed at Lyft Inc. before being donated to the Cloud Native Computing Foundation.
The startup recently completed Y Combinator's winter 2025 batch, raised $4.2 million in seed funding, and already has Neo4j Inc. as an early customer.
Written by urgent.news from SiliconANGLE's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.