Sovereign AI: Where control becomes an architectural requirement
We believe sovereignty is becoming an architectural requirement for firms operating globally, especially in highly regulated industries. The business question for buyers is how much control an organization needs over the systems that produce its intelligence, and what happens when that control is ceded to others. U.S. companies supply most of the cloud and frontier […] The post Sovereign AI:…
Sovereignty is becoming an architectural requirement for firms operating globally, particularly in highly regulated industries, according to the source. The primary question for purchasers is the extent of control they require over systems generating intelligence and the implications when that control is relinquished to others. Major cloud and frontier AI technology providers are predominantly U.S.-based.
Purchasers must comprehend the resulting jurisdictional, operating, and commercial risks and implement compensating controls to mitigate them. This applies to U.S. firms operating abroad and even domestic firms, especially those in regulated sectors.
The discussion covers data location, key management, model interaction with data, system operations, and exposure to costs. The premise is that sovereignty necessitates deliberate risk decisions, compensating controls, and proof that those controls function effectively. The ideal architecture involves trade-offs and depends on workload and the consequences of losing control.
Three sources of input were used: Amit Govrin's buyer's guide, a study commissioned with partners at Qualitate, and John Furrier's conversation with Amit at SC26. The buyer's guide assesses documented controls in hyperscaler offerings and buyer territories. The study with Qualitate includes the experiences of eleven senior technology decision-makers in regulated and critical-infrastructure organizations. The conversation at SC26 explains the reasoning behind the framework.
The buyer's guide independently measures vendors' claims. Interviews with the survey sample reveal a gap between buyer priorities and operational reality. Legal exposures are a prominent purchasing decision, but seven out of eleven respondents report no testing of disconnected systems, key-revocation, or exit scenarios. Buyers tend to add controls to existing platforms, with only four out of eleven deploying or piloting a distinct sovereign or dedicated offering. Cost and added burden are the primary reasons for this behavior.
A European IT and telecom buyer highlights that deep support escalations may involve personnel or systems outside the EU during critical technical issues. The key point is that sovereignty is not a purity test; organizations can tolerate such exposure during emergencies. The message is to be aware of the condition, evaluate the risk, and implement compensating controls if needed.
Cost heavily influences sovereignty investments. Buyers justify stronger controls for sensitive workloads while accepting varying levels of exposure for lower-risk activities. Migration effort, retraining, and exit costs affect this decision. Assessing sovereignty exposure is akin to assessing cybersecurity exposure. AI inference requires inference within the sovereign or regional boundary for nine out of eleven respondents.
Model availability can lag inside these environments, necessitating a tradeoff between local jurisdiction risk and model capability for specific workloads.
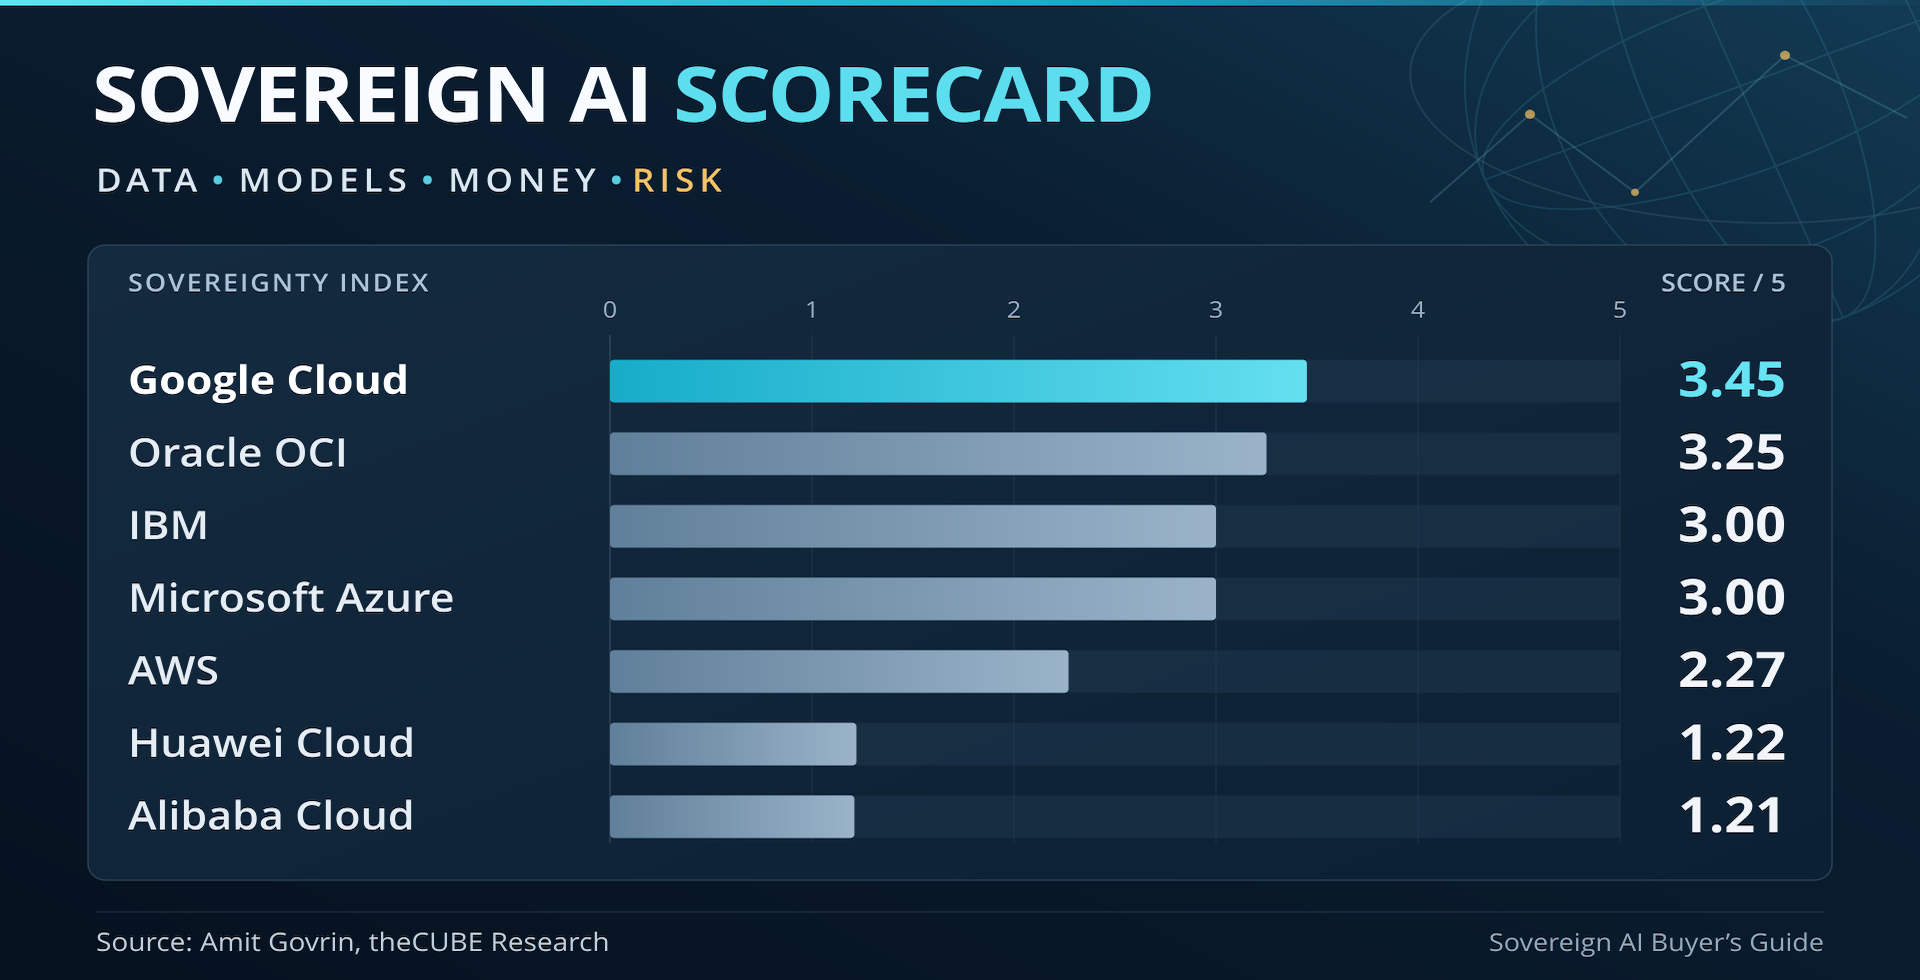
Buyers must weigh the worth of stepping outside the lines to achieve business results, depending on the risk degree and the business value magnitude. Sometimes, paying the parking fine may be justified. The high-level comparison from the buyer's guide shows Google LLC leading with a score of 3.45 across all regions and tests, followed by Oracle Corp. (3.25), IBM Corp. and Microsoft Corp.'s Azure (3.0), AWS (2.7), Huawei Technologies Co. Ltd. and Alibaba Group Holding Ltd. (1.2).
However, this is a point-in-time index from the Nov. 14 revision, and a low score doesn't mean a vendor won't be chosen.
Rewritten by urgent.news; may contain errors — check the original.