CTO of ‘RansomwareHelp’ Indicted for Wire Fraud
The chief technology officer and co-founder of ransomwarehelp.com, a six year old Florida business that claimed to use "advanced cryptographic tools" to restore data locked by ransomware, has been charged with wire fraud after an FBI sting operation found the company was simply paying the attackers for a decryption key and charging victims a markup for work that was never performed.
Juan Ricardo Palacio Escobar, the co-founder and chief technology officer of the Florida-based ransomware help website, has been indicted by federal prosecutors for wire fraud. The indictment alleges that Palacio routinely paid ransomware groups for decryption keys and then charged victims significantly more than he had paid the threat actors.
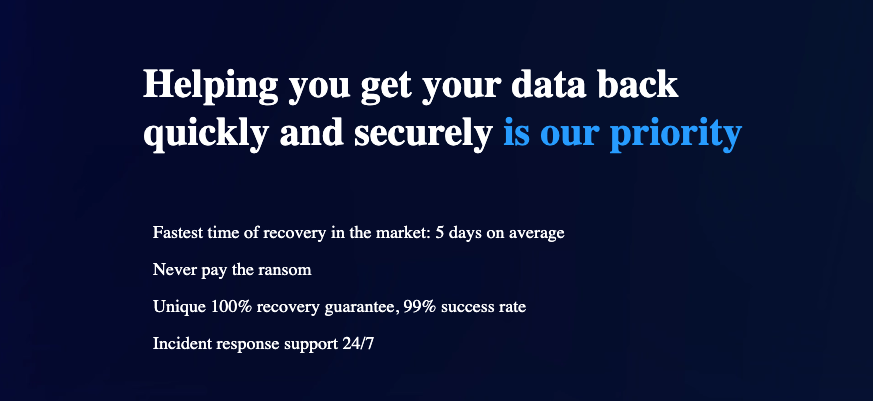
The company's website claimed its "proprietary tools and algorithms" could recover 100% of data, servers, and systems, but in reality, the victims never received any actual recovery work. The FBI set up a sting operation where they posed as both a victim company and a fake ransomware group. When RansomwareHelp contacted the FBI's fake ransomware group, they requested a low price for the decryption key.
The indictment states that Palacio then allegedly negotiated a higher price and charged the fake victim firm $16,010, including an initial diagnostic fee and the full fee for decryption.
Written by urgent.news from KrebsOnSecurity's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.