Urgent.News

What's breaking now, across thousands of outlets.

Tech

WhatsApp Patches 3 Security Flaws, Including Android Bug Suspected of Use in Scams

Meta-owned WhatsApp has addressed security vulnerabilities, including one impacting its Android app that it suspects may have been exploited in connection with scam messages. The vulnerability, tracked as CVE-2026-23871, has been described as a case of incomplete validation of external ad-reply URLs in WhatsApp for Android and WhatsApp Business for Android before 2.26.17.4. The issue could
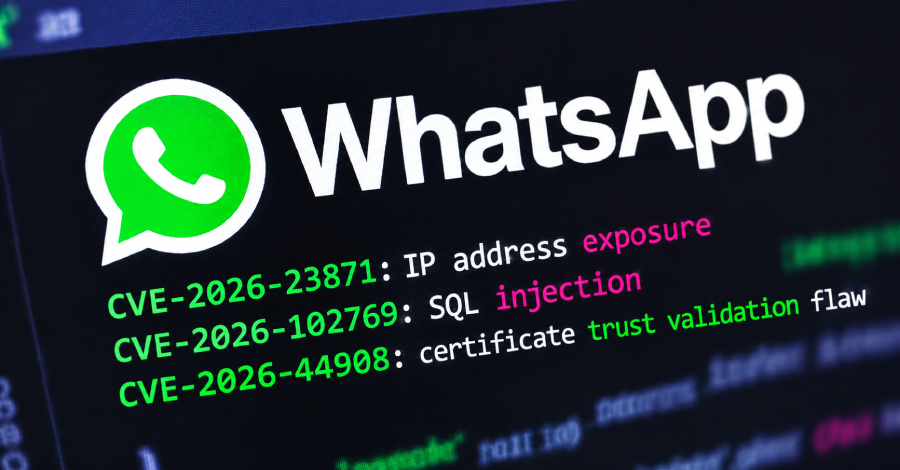
WhatsApp Patches 3 Security Flaws, Including Android Bug Suspected of Use in Scams

We haven't written up this one. The Hacker News has the full story — the link below goes straight to it.

Read the original at thehackernews.com →

More in Tech

Running untrusted pull request code from agents and contributors

Originally published on sandscale.dev . A pull request is a request to run someone else's code on your machine. CI has always worked this way: check out the branch, install dependencies, run the…

  • Pull requests run untrusted code, posing risks like code escaping or data exfiltration
  • Sandscale's sandbox creates a separate kernel and network environment for each PR
  • After tests, sandbox should be stopped and discarded to prevent lingering malicious code

How do you tune speculative decoding in a production serving stack?

Tune speculative decoding against your own traffic, not a benchmark. Choose a method that fits your workload, set draft length from measured acceptance rate, and re-test at production concurrency…

  • Base speculative decoding method on your own traffic data, not benchmarks.
  • Choose n-gram or suffix decoding for modest speedup; use EAGLE or MTP for best latency reduction.
  • Adjust draft length based on acceptance rate; test multiple values and monitor per-request metrics.

More from Friday 20 November →
