Urgent.News

What's breaking now, across thousands of outlets.

Tech

Clicks Communicator hits a supply chain snag, and it isn’t because of RAM

Clicks is still on track to release the phone with a physical keyboard within the next few months, but a Communicator launch before the end of this year isn’t looking very likely as shipping gets pushed back. more…
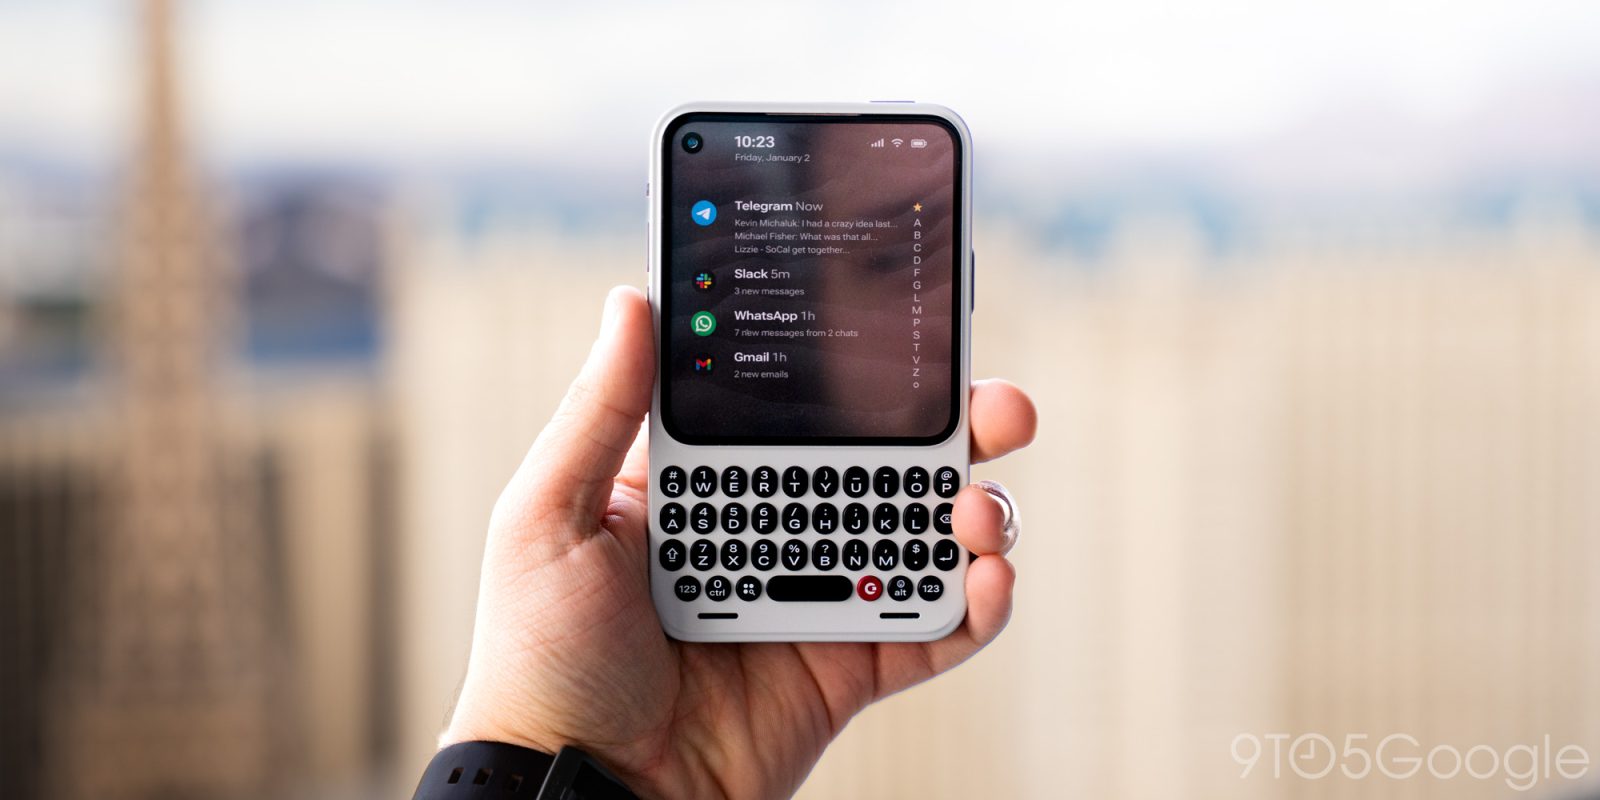
Clicks Communicator hits a supply chain snag, and it isn’t because of RAM

Clicks Communicator, an Android phone with a physical keyboard, faces a supply chain setback that may delay its launch before the end of the year. The device, first introduced at CES, aims to target users seeking a secondary device. Initially slated for a December release, Clicks now anticipates shipping pre-orders as early as late January due to supply chain issues unrelated to RAM.

The primary issue lies with securing a critical component necessary for fabricating printed circuit boards (PCBs). These PCBs are composed of multiple layers, and the specific fabric used to create these layers is scarce due to high demand. Four manufacturers are reportedly unable to meet Clicks' required volume. Additionally, complications arising from geopolitical tensions in the Middle East and rising memory costs have further strained the supply chain.

Despite these obstacles, Clicks remains committed to delivering the Communicator, offering a set of 3.5mm wired headphones for orders placed prior to the update.

Written by urgent.news from 9to5Google's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.

Read the original at 9to5google.com →

More in Tech

5 Security Mistakes I See in Flask + React Apps (and How to Fix Them)

Flask and React are a great pairing: fast to build, flexible, and easy to deploy. But that same speed means security often gets pushed to "later," and later usually means after something breaks.

  • Validate user input against schema using Pydantic
  • Store JWTs in HttpOnly, Secure, SameSite cookies
  • Include token in Authorization header on React frontend

What happens when an offline POS sale syncs twice?

A cashier completes a sale while the connection is down. Later, the server saves it, but the response never reaches the device. The app retries.

  • Unique client sale ID assigned to prevent duplicate transactions.
  • Server handles retries safely with unique database constraint.
  • Testing essential to verify receipt number and inventory accuracy.

NestJS vs Express.js: Choosing the Right Framework for Your Next Node.js Project

Node.js is used by 48.7% of developers in the Stack Overflow Developer Survey 2025. Inside that group, Express.js is used by 19.9% of respondents and NestJS by 6.7%.

  • 48.7% of developers used Node.js in 2025 Stack Overflow survey
  • NestJS has 6.7% adoption, growing due to structured approach
  • Express.js excels in speed and control, while NestJS offers structure and features

How do you tune speculative decoding in a production serving stack?

Tune speculative decoding against your own traffic, not a benchmark. Choose a method that fits your workload, set draft length from measured acceptance rate, and re-test at production concurrency…

  • Base speculative decoding method on your own traffic data, not benchmarks.
  • Choose n-gram or suffix decoding for modest speedup; use EAGLE or MTP for best latency reduction.
  • Adjust draft length based on acceptance rate; test multiple values and monitor per-request metrics.

Running untrusted pull request code from agents and contributors

Originally published on sandscale.dev . A pull request is a request to run someone else's code on your machine. CI has always worked this way: check out the branch, install dependencies, run the…

  • Pull requests run untrusted code, posing risks like code escaping or data exfiltration
  • Sandscale's sandbox creates a separate kernel and network environment for each PR
  • After tests, sandbox should be stopped and discarded to prevent lingering malicious code

More from Friday 20 November →