I turned my old Android phone into a Frigate security camera, and it watches my front door for free
It works well with my local AI summary pipeline, too
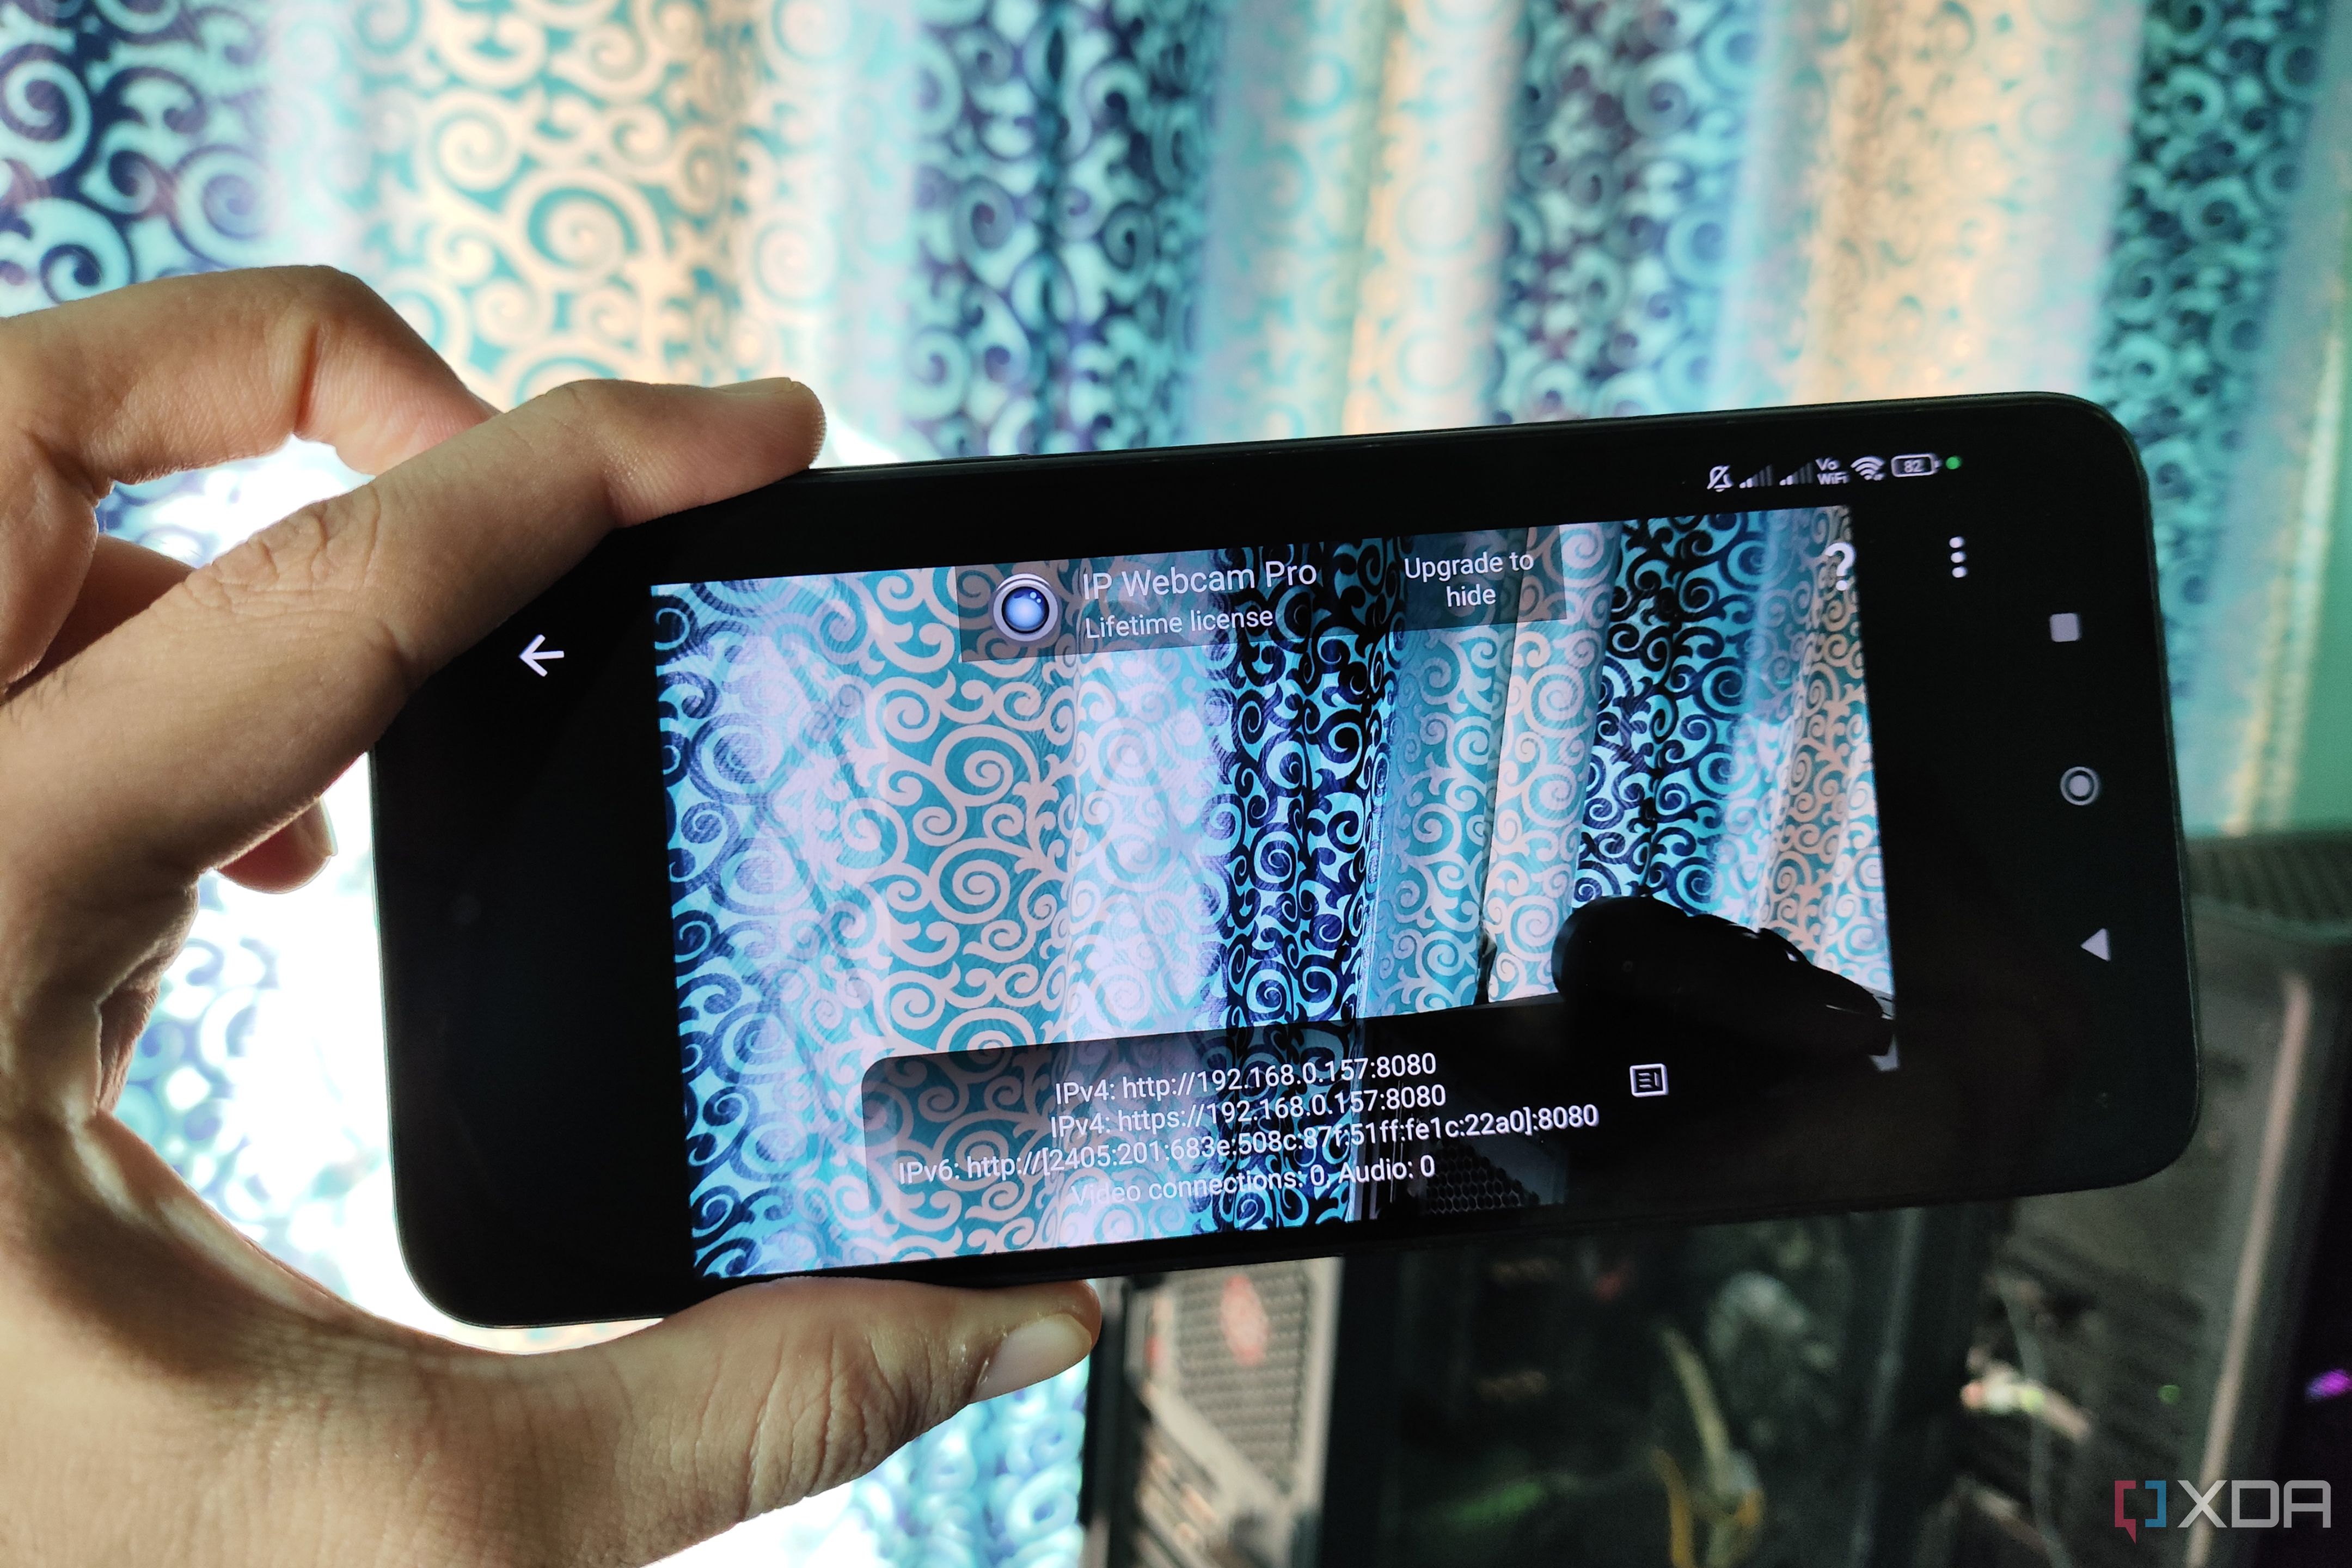
Once an old smartphone was given a new life as a security camera, effortlessly keeping watch over the entrance to the home. The device, despite not being the most picturesque, could still capture footage without turning it into a low-resolution mess. With sensors like a display, microphone, speaker, and gyroscope, the phone could be transformed into a versatile security tool.
Pairing it with Frigate, a surveillance system, allowed the phone to manage its stream and even trigger automation chains through object-detection functionality. This setup was not only cost-effective but also provided peace of mind, knowing that all the footage of the home's premises would remain private and not be processed on any random company's servers.
Setting up the phone as a security camera required tweaking router settings to assign a static IP address to the device, ensuring the network remained stable. The phone could transmit RTSP streams, but it needed a Network Video Recorder (NVR) to record footage. Frigate was chosen for its lightweight nature and extra features for enhancing the security setup.
By running Frigate on a Raspberry Pi 5 and adding a dedicated AI HAT, the phone could handle multiple 720p sub-streams for object detection. Home Assistant was then integrated with Frigate, enabling automation pipelines and generating detailed summaries of detected objects using self-hosted LLMs. This setup not only saved money but also ensured the privacy of the footage, as it remained on local hardware.
Written by urgent.news from XDA Developers's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.