Trump admin orders Kalshi to halt wagers on what words Trump will say
CFTC: Kalshi bets may violate US ban on contracts that can be easily manipulated.
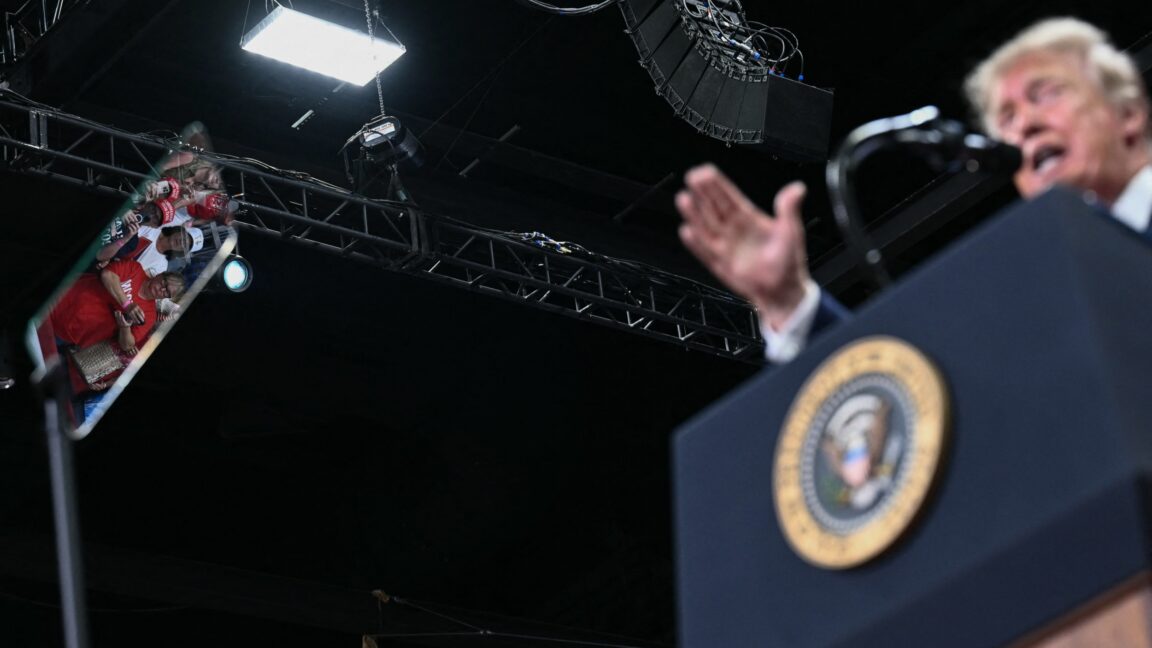
The Trump administration has directed prediction market platform Kalshi to cease offering event contracts that pay out if President Trump utters specific words before a certain date. Kalshi subsequently halted trading in these contracts while the US Commodity Futures Trading Commission (CFTC) investigates whether the mention contracts breach federal law.
CNBC reported that Kalshi discreetly stopped trading in several mention contracts linked to President Donald Trump at the end of last week, at the CFTC's request. Kalshi affirmed to media organizations that it is adhering to the CFTC's directive. The market segments suspended by Kalshi enabled participants to bet on whether Trump would employ certain words, encompassing informal appellations and the names of nations and enterprises.
A comparable expired event contract, still viewable on Kalshi's website, inquired if Trump would utilize the informal terms Marjorie Traitor Greene, Sleepy Joe, and Whack Job before April 2026.
Written by urgent.news from Ars Technica's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.
This story
This is one outlet's version. Read the fullest account.