Attackers Used Optimizely to A/B Test Malware on Top Websites
At least 178 top web destinations unwittingly served a variety of malware exploits against visitors over the past 24 hours thanks to a security vulnerability involving Optimizely, a company that helps websites customize user experiences and test out new features. Experts say the incident, which saw data-stealing malicious software silently injected into sites like the BBC, CNN, Equifax, Ledger…
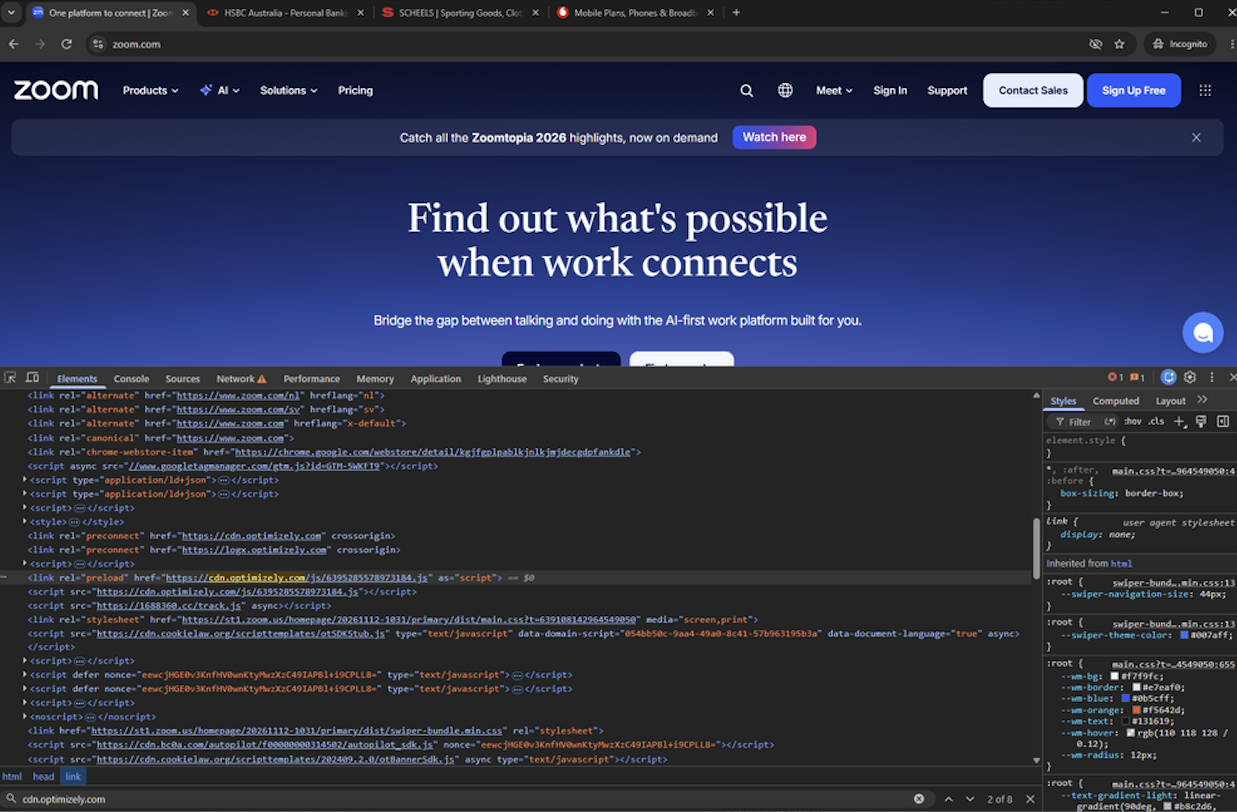
A security vulnerability in Optimizely, a company that helps websites customize user experiences and test new features, led to the injection of various malware exploits into at least 178 top web destinations over the past 24 hours. Sites such as the BBC, CNN, Equifax, Ledger, and Zoom were among those affected. Report URI's Scott Helme explained that the malicious JavaScript code delivered by Optimizely was rebuilt 26 times throughout the day, dropping a multi-purpose malware kit capable of stealing payment card data, cookies, screenshots, and modifying cryptocurrency payment addresses to those controlled by the attacker.
Helme emphasized that trusted JavaScript does not always remain trustworthy, as a compromised third-party dependency can lead to security breaches. Optimizely acknowledged the incident, stating that they swiftly identified and remediated the vulnerability by blocking access to the vulnerable path, deploying a fix, removing injected code, ending active sessions, revoking tokens, and resetting access for affected user accounts. They have also implemented additional protections to prevent malicious code delivery in Cloudflare.
The incident highlights the risks of relying heavily on third-party JavaScript code, which often enables precise browser fingerprinting and tracking. Websites benefit from using Content Security Policies (CSPs) to specify allowed domains for third-party content. However, many websites, particularly smaller ones, do not employ CSPs or have overly permissive policies, making them vulnerable to supply chain attacks.
Report URI found that only 24 of the affected sites had CSPs that fully blocked the malicious payload, while 68 had no CSP at all. Overall, about 10 percent of the web's busiest sites use effective CSPs, according to Helme's site crawler.ninja. The researcher hopes this incident will encourage more websites to adopt effective CSPs to prevent such attacks.
Written by urgent.news from KrebsOnSecurity's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.