I mirrored my network traffic and discovered what my devices hide from me
Most of it was noise but some things stood out
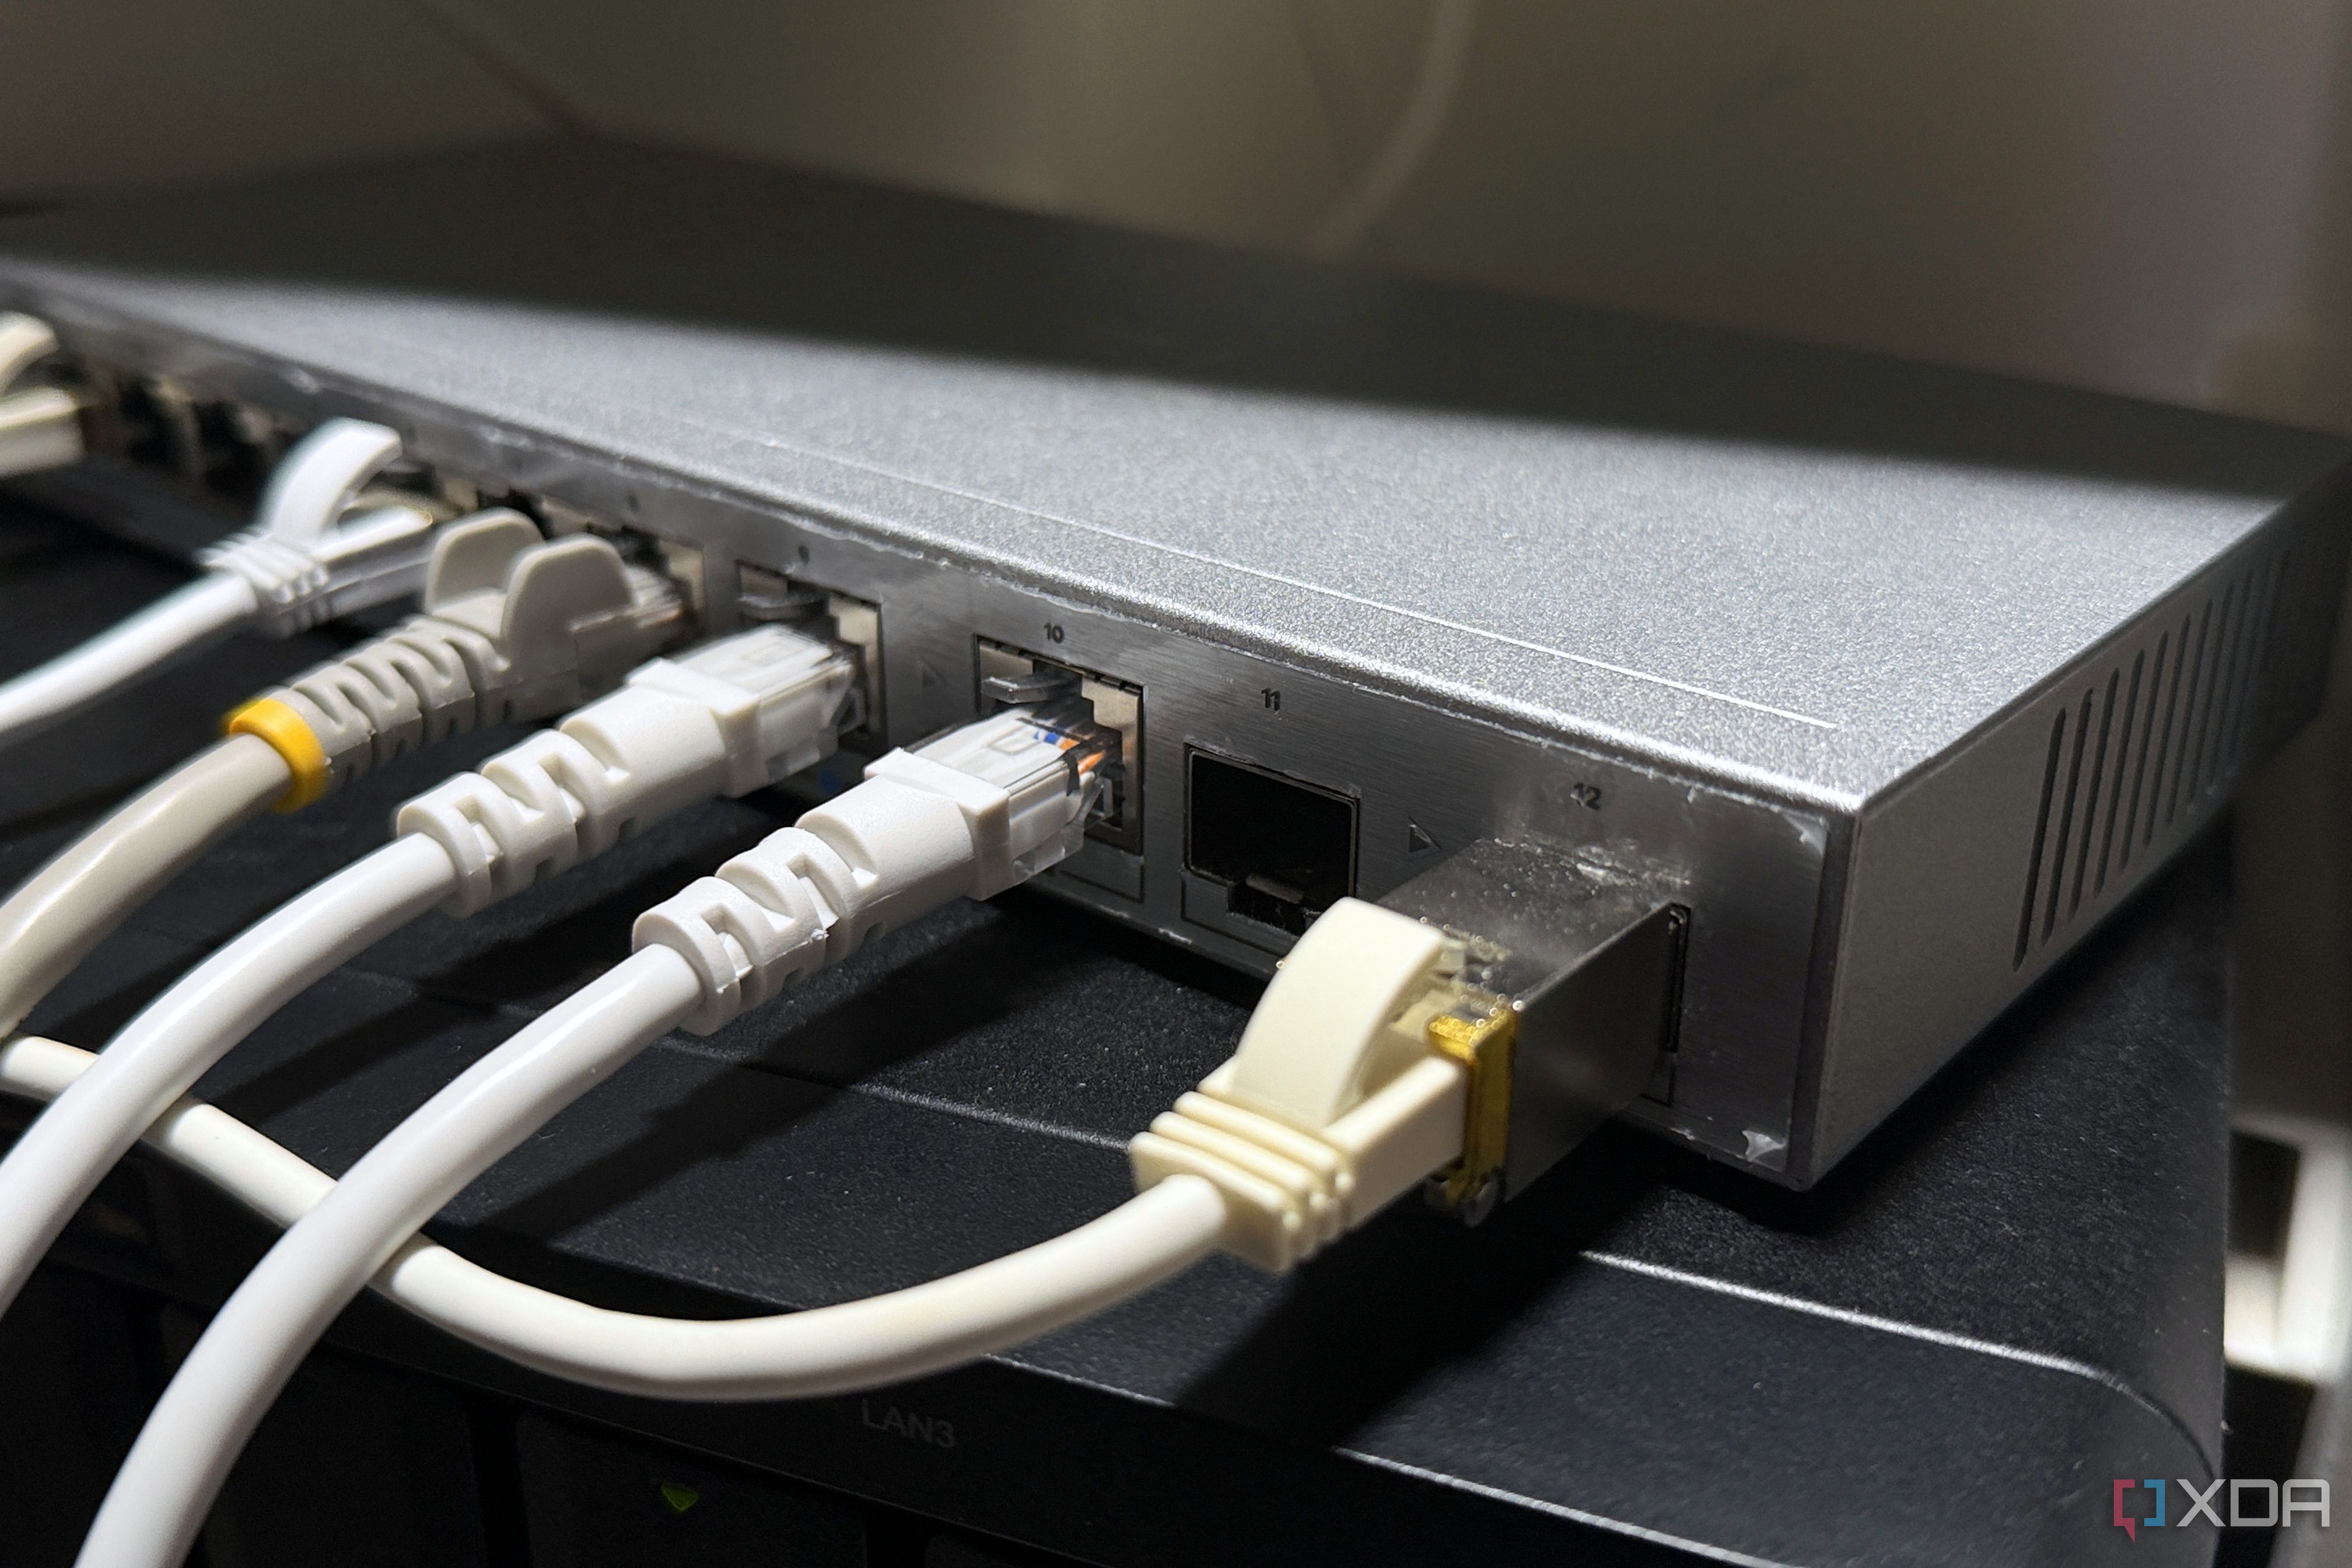
A home network user engaged in traffic mirroring to uncover hidden activities among their devices. Utilizing a Zyxel XGS1210-12 switch, they captured and analyzed half an hour of network traffic, revealing a MacBook performing frequent Time Machine backups, which was expected for backup purposes. Surprisingly, their desktop PC was found to be responsible for a significant number of DNS lookups across 309 different domains, even though no applications were actively in use.
This was attributed to background processes, including Microsoft telemetry endpoints, Grammarly logging, 1Password telemetry service, Sentry error reporting, and GOG Galaxy's log messages. Additionally, the TCL TV was observed communicating with 44 unique domains, with its most frequent contact being on-hweudc-o.api.leiniao.com, the domain for TCL's internet-TV, content, and ads subsidiary.
The TV also broadcast UDP packets to all devices on the network at a frequency of approximately every 2.6 seconds. While most DNS queries were directed towards the user's router, the desktop PC's DNS requests went directly to eero, bypassing the user's filtering. The user also discovered various devices sharing information, such as the Hue Bridge sending UDP packets to Amazon Web Services, Sonos speakers advertising their firmware, an Anker device broadcasting its power service, and the NAS transmitting Plex discovery packets.
These findings highlight how seemingly innocuous devices can inadvertently reveal sensitive information while connected to a home network.
Written by urgent.news from XDA Developers's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.