Navi Mumbai Cyberattack Exposes Alleged Data Theft Of 3.75 Lakh Bank Customers, Records Reportedly Leaked On Dark Web
Navi Mumbai: Data belonging to approximately 3.75 lakh customers of one of the country's leading public sector banks has allegedly been stolen in a cyberattack on its Global IT Centre in Sector 11, CBD Belapur, Navi Mumbai. The hackers reportedly gained unauthorised access to the centre's servers and extracted data from two critical applications, UNO 2.0 and RAAS, before circulating it on the…
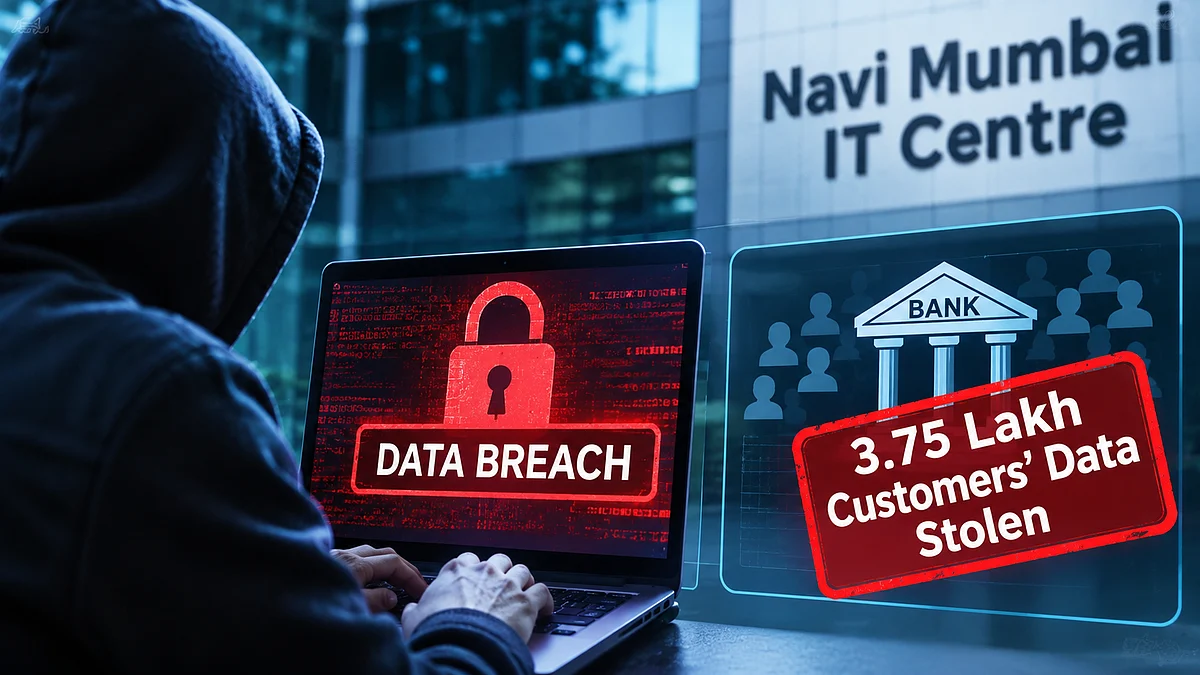
Navi Mumbai police have registered a case against unidentified hackers following a cyberattack on the leading public sector bank's Global IT Centre. According to prosecutors, the hackers allegedly stole data from three critical applications, UNO 2.0, RAAS, and leaked it to the dark web. The breach exposed personal information of approximately 3.75 lakh bank customers.
The bank's servers were targeted on October 9 at around 4:13 pm, and the theft occurred on October 15 at around 6 pm. The incident was detected on October 16, leading to the police probe into the security breach.
Written by urgent.news from Free Press Journal's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.