Synology patches a critical NAS flaw that could let attackers in without logging in
A newly published security advisory discloses two serious vulnerabilities in DiskStation Manager (DSM), the Linux-based OS used in Synology NAS products, one of them rated critical. The storage maker warned that the flaws could be abused to remotely access and attack vulnerable devices, giving cyber-criminals – or rogue AI agents,... Read Entire Article
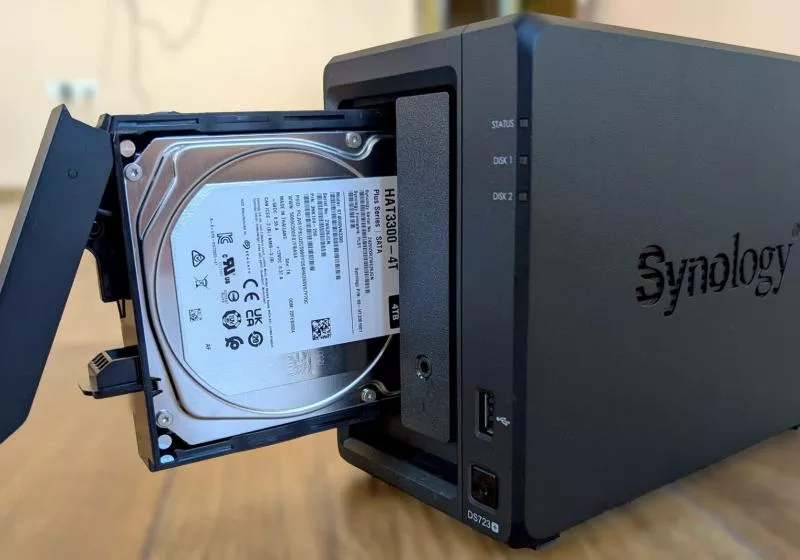
Synology has released a patch for two critical vulnerabilities in its DiskStation Manager (DSM) operating system, which is used in many of its network-attached storage (NAS) devices. The flaws, tracked as CVE-2026-76954 and CVE-2026-85101, could allow attackers to remotely access and manipulate data on vulnerable devices without logging in.
The SQL injection flaw is rated with a perfect 9.8 out of 10 score on the Common Vulnerability Scoring System (CVSS), indicating it poses a high risk. The rsync tool vulnerability, while less severe at an 8.6 score, could still enable attackers to bypass authentication and read or write files. Both bugs can be exploited remotely.
Synology released firmware updates to address the issues in October 2026, and users are advised to install them promptly, especially those who manually update their devices. The company credited external researchers for discovering the vulnerabilities. Despite the patch, some users have expressed dissatisfaction, calling the SQL injection flaw an embarrassment for Synology's software.
The incident has also reignited criticism over Synology's policy of only allowing certified hard drives in its NAS systems.
Written by urgent.news from TechSpot's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.