Software Samaritan revamps borked Indian certs to block smart TV ads
A little tinkering can black hole obnoxious Samsung TV ads and some tracking, until a firmware fix ruins the fun
eMudhra, an Indian company that operated a trusted HTTPS certificate authority, issued over 60 million digital certificates. However, the company's private keys were exposed, with some of the intermediate CA private keys being extremely weak. This exposed a security disaster, allowing anyone to forge eMudhra certificates and potentially spoof websites or conduct malicious activities.
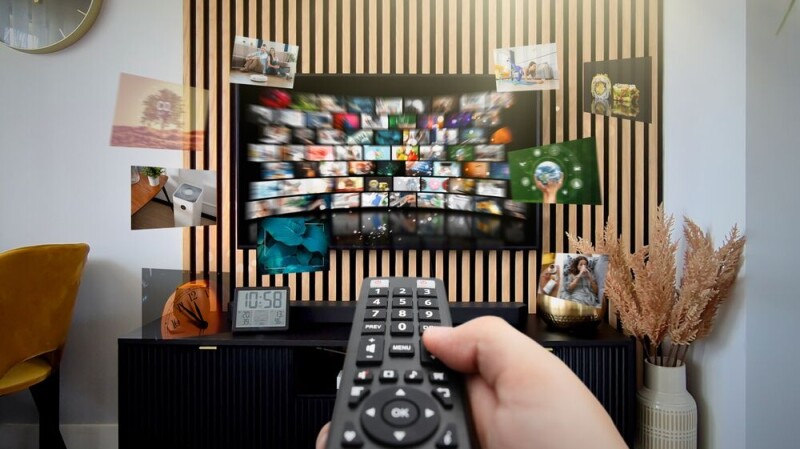
Czech software developer Daniel Vrátil took advantage of this situation and repurposed the exposed keys to block annoying ads on Samsung smart TVs. By using a Pi-hole (DNS-based ad-blocking software) and the mitmproxy service, Vrátil was able to inspect the smart TV's HTTPS traffic, redirect selected requests to his server, and replace the ads with family photos on the TV's main screen.
Vrátil's work has been published on GitHub for others who want to block ads on their smart TVs that still trust eMudhra certificates. However, the process is not one-click and requires users to dissect how their device retrieves ads and modify the code accordingly. The vulnerability is only exploitable as long as vulnerable devices continue to trust eMudhra certificates. As smart TVs become out of support, they may remain exposed to certificate weaknesses even if users block ads.
Written by urgent.news from The Register Software's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.