Critical Apache HTTP/2 Flaw Could Let Unauthenticated Attackers Execute Code Remotely
A critical flaw in Apache HTTP Server's HTTP/2 module, mod_http2, can let a remote attacker run code on the server. Tracked as CVE-2026-119618, it affects versions 2.4.55 through 2.4.70 and is fixed in version 2.4.71, released yesterday. Only servers with HTTP/2 enabled are affected, according to Red Hat, which ships the server as part of Red Hat Enterprise Linux. An attacker who can reach the
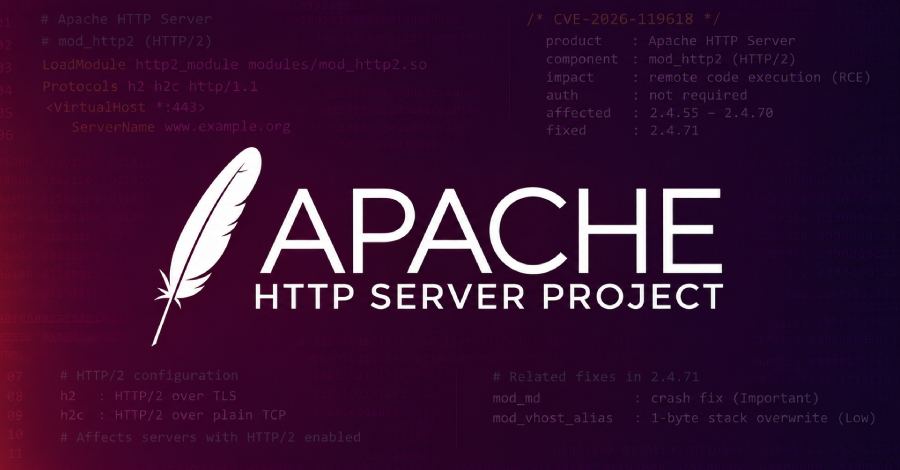
A flaw in Apache HTTP Server's HTTP/2 module, CVE-2026-119618, could enable remote attackers to execute code on vulnerable servers. The vulnerability affects versions 2.4.55 through 2.4.70 and is resolved in version 2.4.71. Only servers with HTTP/2 enabled are impacted. Unauthenticated attackers can exploit the flaw and take full control of the server process.
This critical vulnerability rates 9.8 out of 10 on the CVSS scale. Red Hat, which ships the server with Red Hat Enterprise Linux, rates the flaw Important rather than Critical in the latest release. No exploit is currently available, but public research has demonstrated a reliable attack against a server in its default configuration.
Administrators should verify their server-wide settings and virtual host configurations to ensure HTTP/2 is not enabled. The flaw was reported by Anthropic's OSS Scanner and Google Cloud Vulnerability Research.
Written by urgent.news from The Hacker News's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.