Cybersecurity double standards must end
The Financial Security Institute (FSI) was hit with a cyberattack. Despite the significance of the incident, the news barely made headlines, as cyber breaches have become almost commonplace. Thieves stole about 200 documents, including consent forms for the collection, use and disclosure of personal credit information and the personal information of 300 customers. The victims were employees in…
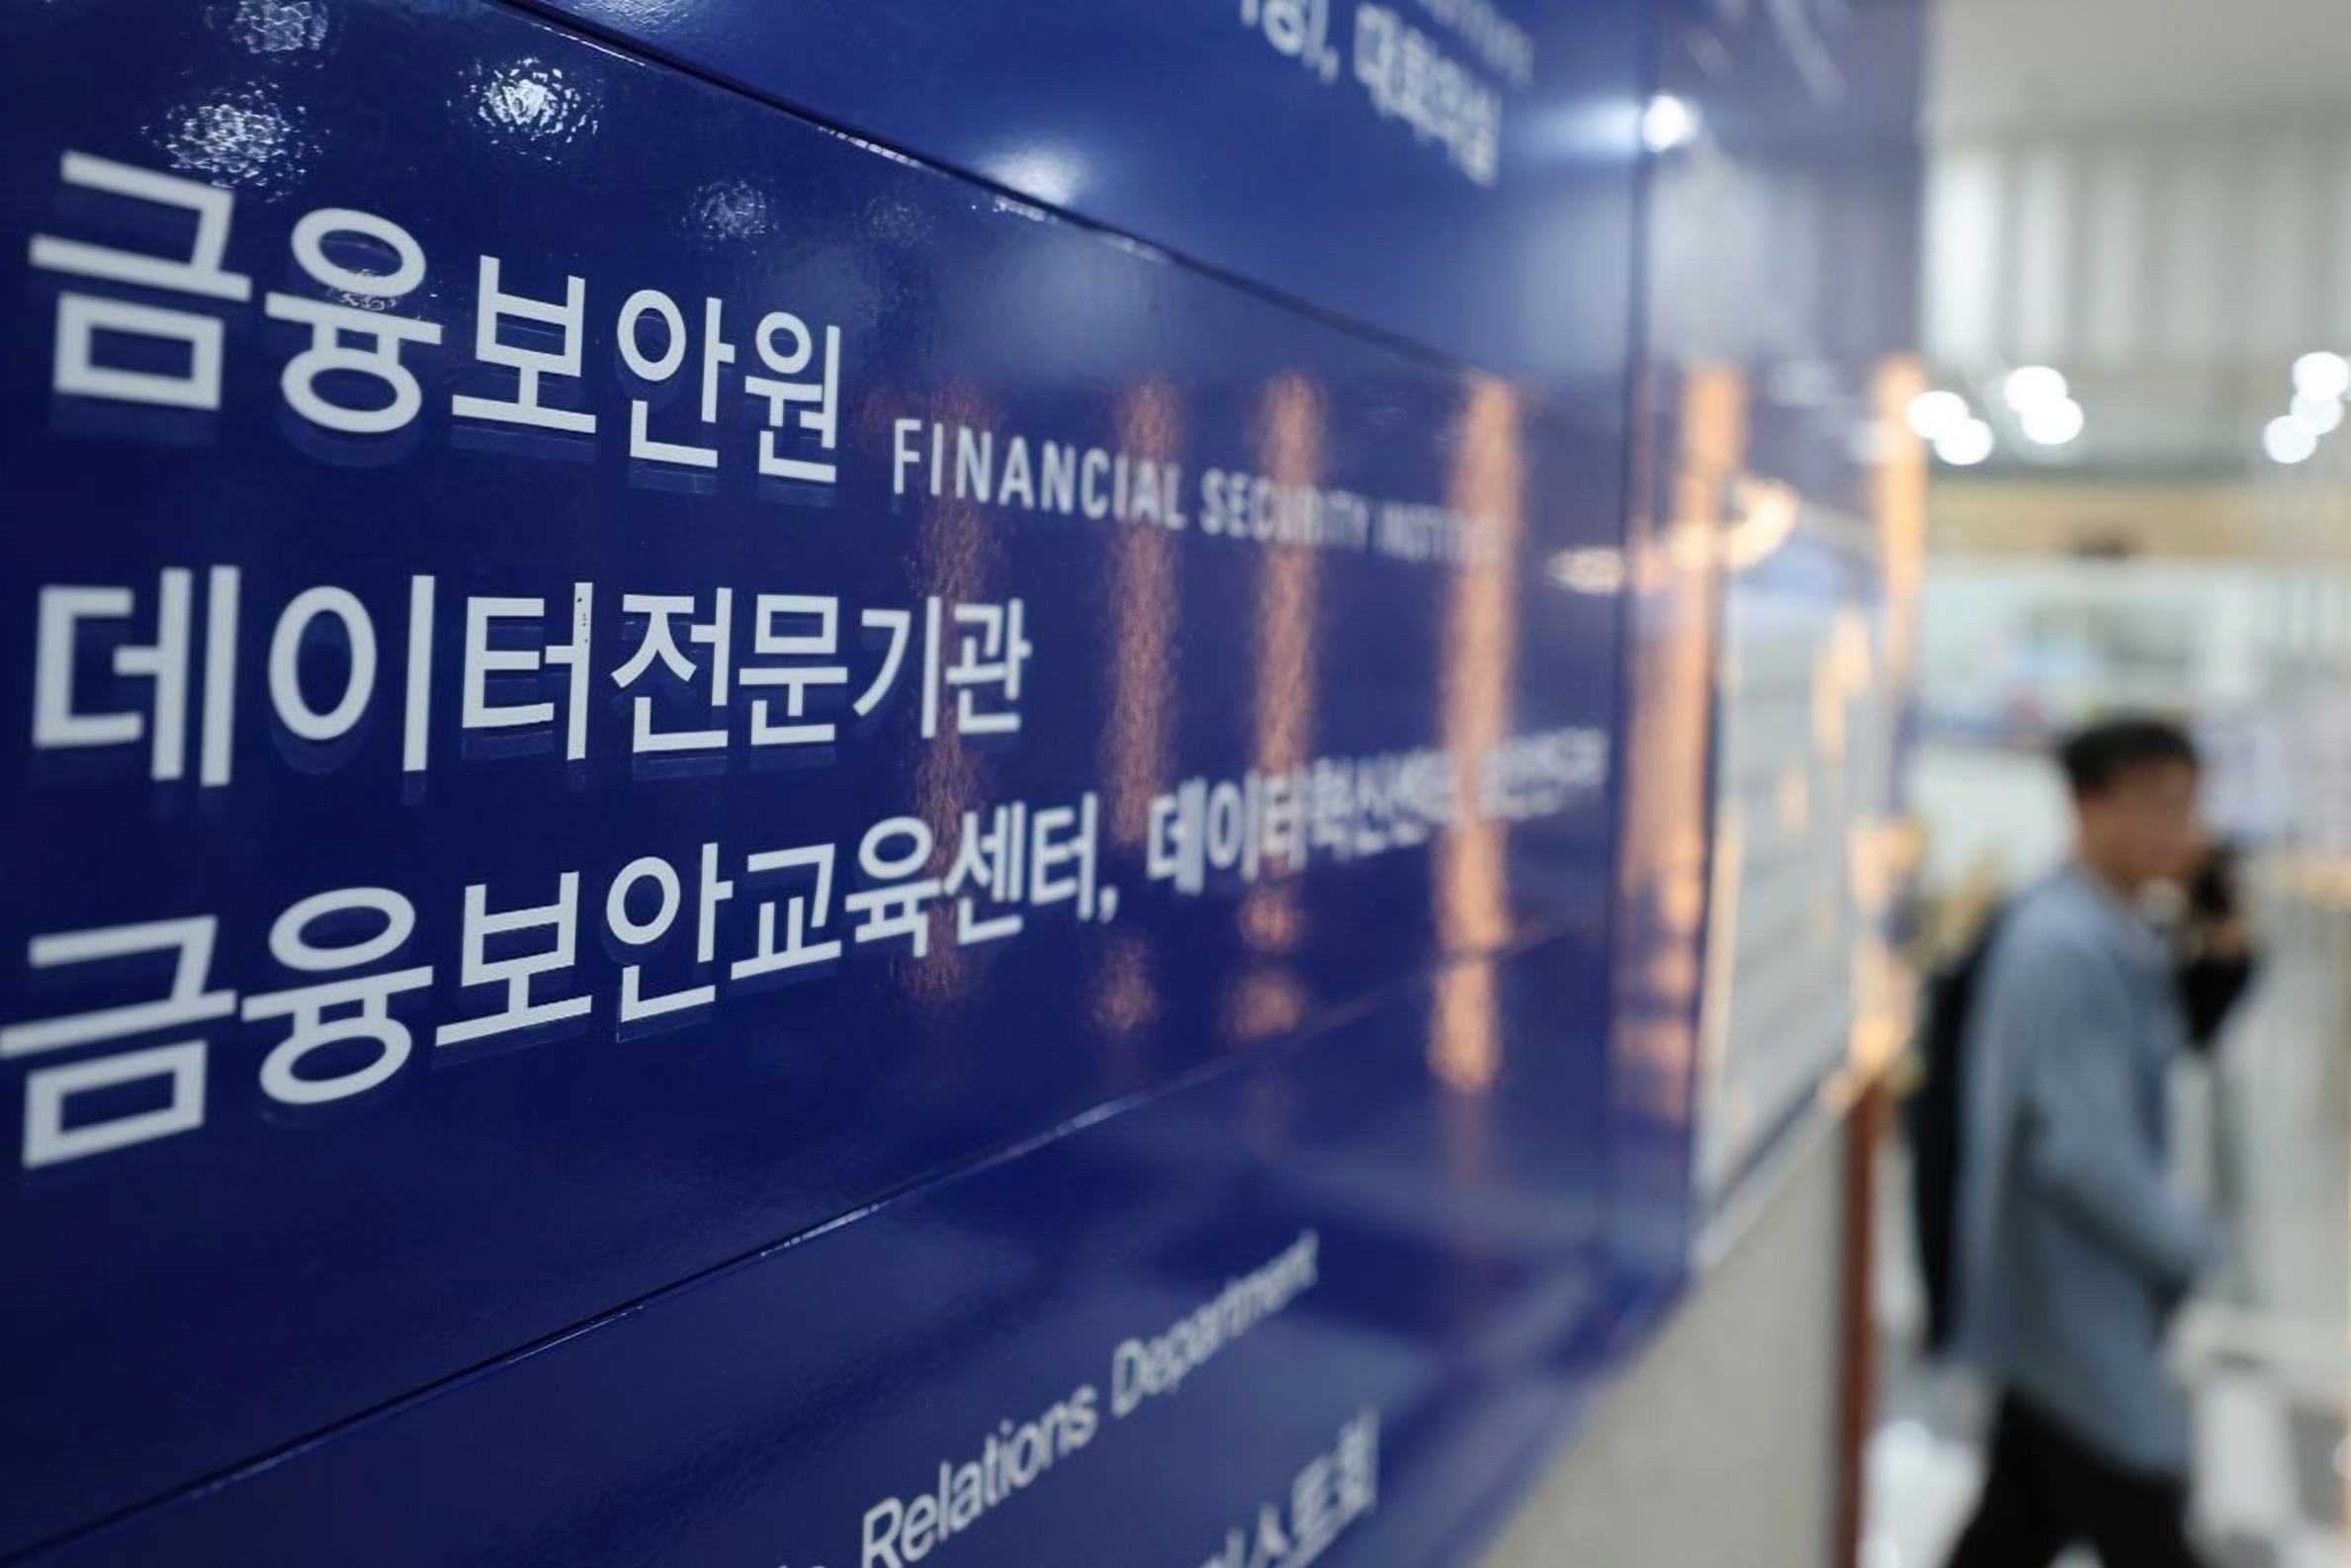
A cyberattack on the Financial Security Institute (FSI) managed to go largely unnoticed despite its severity, as cyber breaches have become all too common. The thieves obtained approximately 200 documents, including consent forms and personal data of 300 customers belonging to banking sector employees. Names and dates of birth were among the compromised information.
This incident follows similar security breaches at two other state-run organizations this year: the Ministry of the Interior and Safety, and the Bank of Korea. However, these public-sector institutions have faced no repercussions or disadvantage following the cyberattacks.
The double standards surrounding cybersecurity are starkly evident when compared to the severe penalties imposed on private companies. Coupang, for instance, incurred a record-high fine of 630 billion won ($470 million) after the personal data of over 33 million customers was compromised, along with other violations. Prior to this, SK Telecom faced similar consequences for data breaches.
The contrast between the lack of accountability for public-sector institutions and the harsh penalties faced by private companies highlights the urgent need to end the double standards in cybersecurity.
Written by urgent.news from The Korea Times's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.
Also reported by 1 other outlet
- Cybersecurity double standards must end koreatimes.co.kr