Software engineer Rickrolls his Prusa 3D printer via remote code execution exploit
A software engineer demonstrated the ability to Rickroll a 3D printer via remote code execution (RCE). This security flaw has been fixed in the latest Prusa software.
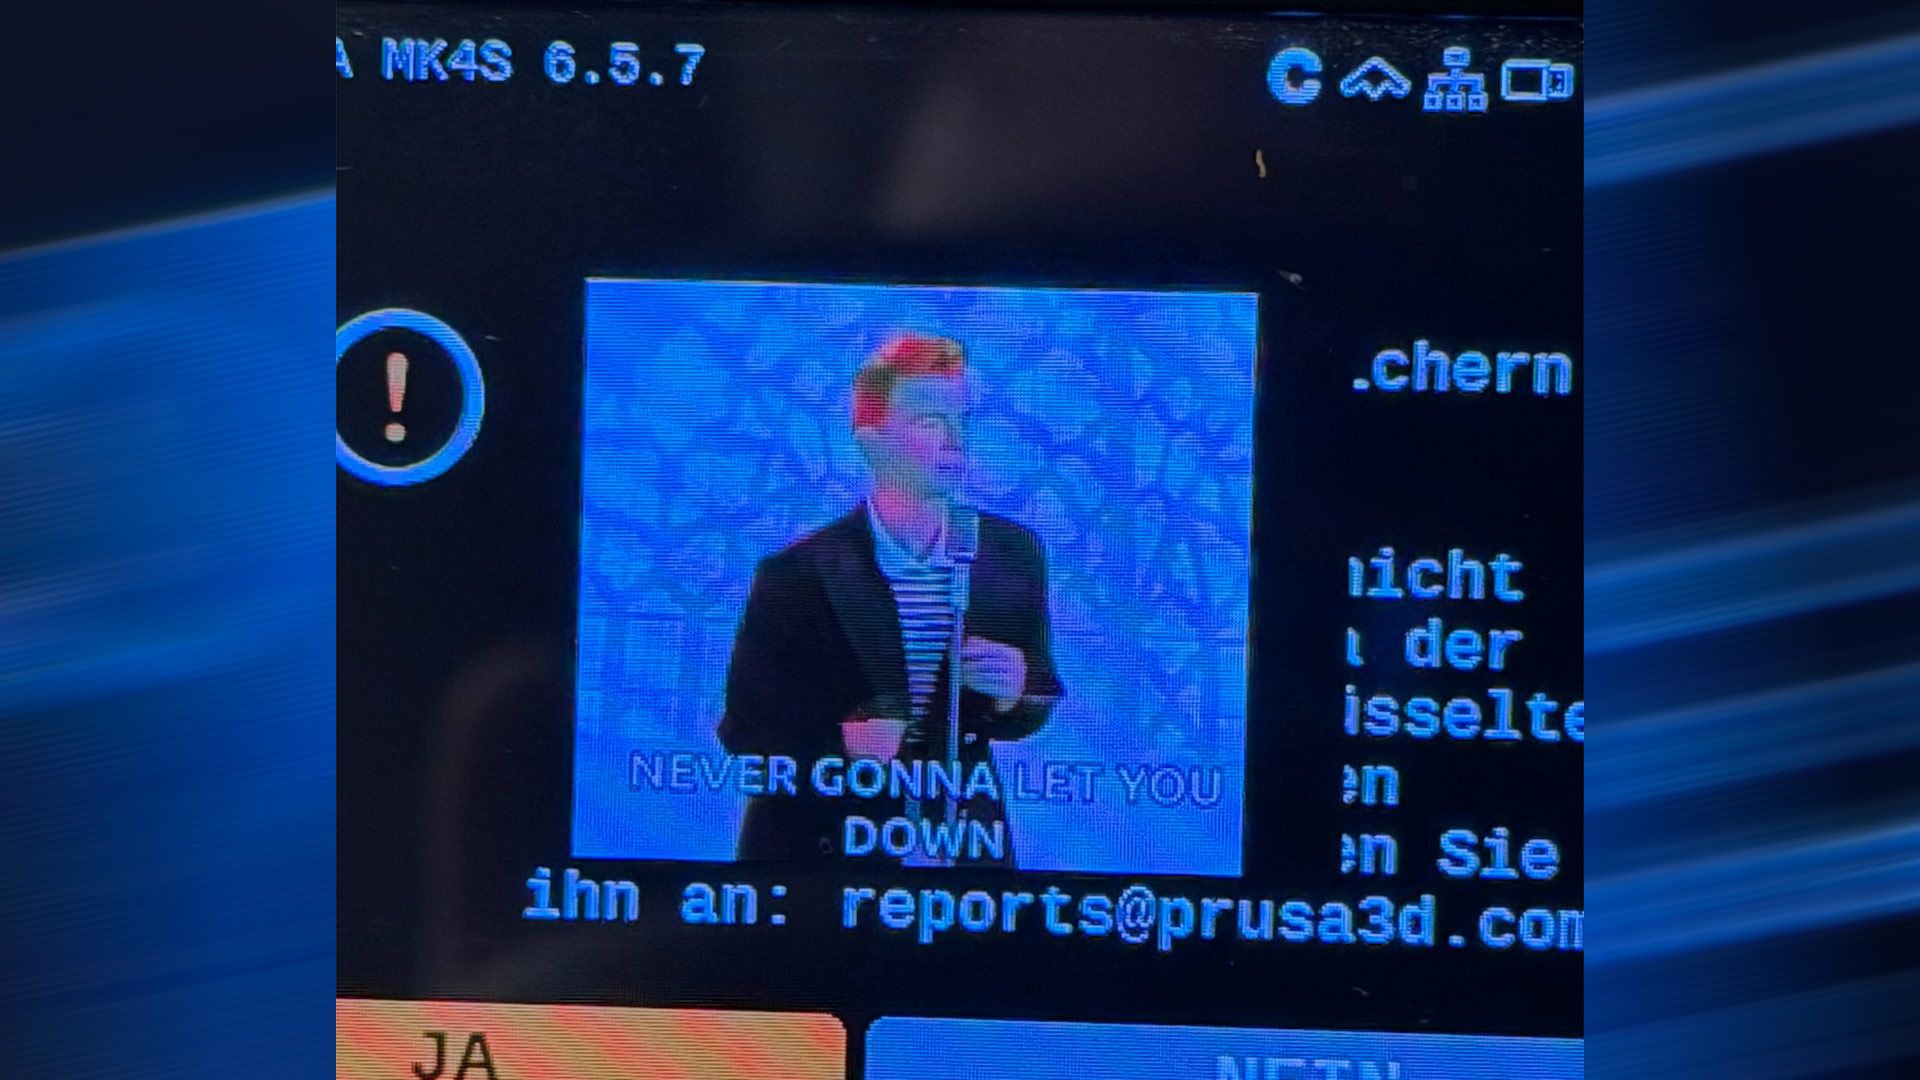
Software engineer Yannick Dixken spent a week hunting for vulnerabilities in his Prusa MK4S 3D printer. Using remote code execution (RCE) as a means to achieve his goal, Dixken ultimately demonstrated the printer's susceptibility to such attacks via a video. He documented a total of 23 individual defects, with a chain leading to the main controller running code sent over the network.
The RCE vulnerability scored an 8.1 and was classified as High Severity. The main issue lay within Prusa Connect, the cloud or self-hosted management platform. Dixken shared proof-of-concept code in the video and promptly sent it to Prusa. In addition to the RCE, he uncovered a USB filename attack, heap overflows, and network denial-of-service flaws.
Most vulnerabilities stemmed from developers' overreliance on assert statements. Dixken responsibly disclosed these issues, and within 24 hours, Prusa's team responded proactively, efficiently, and amiably.
Written by urgent.news from Tom's Hardware's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.