SGLang RCE Exploit Breaches NEAR AI, Steals Data From 18 Agents and About 100 Users
An attacker exploited a remote code execution flaw in SGLang, an open-source inference engine, and ran code on one of NEAR AI's inference servers last Sunday. The attacker could also have seen requests being processed on that server that day, including requests sent in confidential mode, the company said earlier this week. That mode processes requests inside a trusted execution environment (TEE
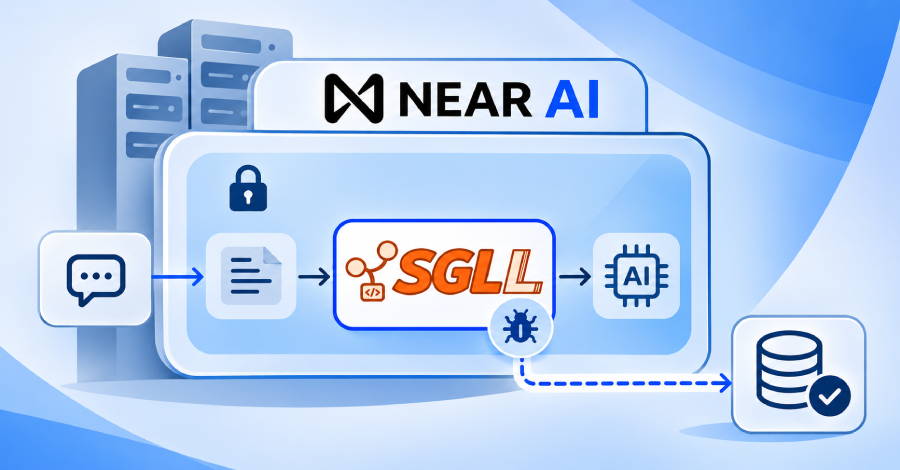
An attacker exploited a remote code execution vulnerability in SGLang, an open-source AI inference engine, to execute arbitrary code on a NEAR AI inference server. The attacker also gained access to requests processed through the company's Private Chat feature, despite the TEE designed to protect those requests. NEAR AI confirmed that the attacker obtained email addresses, names, and optional plan/balance information for approximately 100 users, as well as accessing 18 AI agents on an older deployment of NEAR AI Agents.
The company revoked all active sessions, administrator credentials, and agent tokens, and restored its NEAR AI Cloud services. The vulnerability in SGLang has not yet been publicly disclosed by the SGLang project, though NEAR AI has taken steps to remediate the issue and notified affected users.
Written by urgent.news from The Hacker News's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.