Claude Code's “Don't Ask Again” File Exposes Passwords and Keys in 1,122 Public Copies on GitHub
Passwords and API keys that developers typed into commands they approved in Claude Code are sitting in public GitHub repositories, where anyone can read them. When a user selects "Yes, and don't ask again," Anthropic's AI coding assistant can save the command, word-for-word, including the secret, in a project settings file. Software security company Apiiro said yesterday that 1,122 public
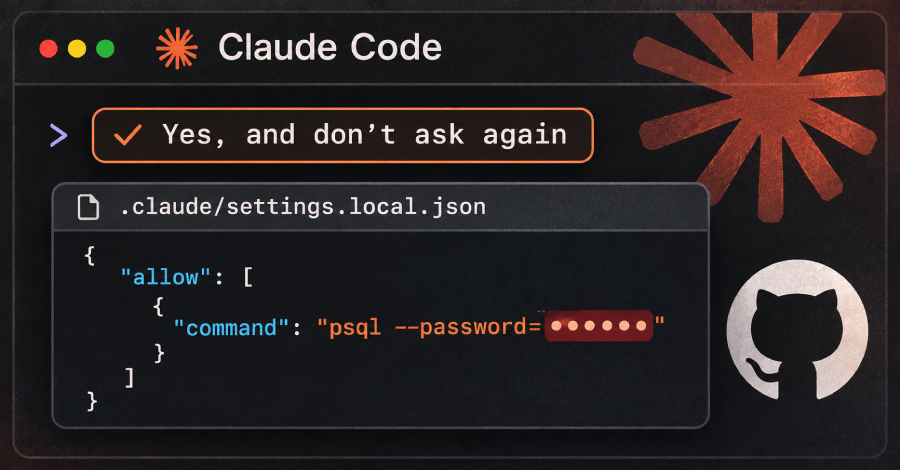
Claude Code's "Don't Ask Again" file has exposed passwords and API keys in 1,122 public GitHub copies. When a developer approves a command with sensitive information, Anthropic's AI coding assistant can save it to a project settings file without encryption. Apiiro, a software security company, discovered that 1,122 public copies of this file contain at least one secret, though they did not verify if any of them are still functional.
When a user selects "Yes, and don't ask again," Claude Code saves the command, including any secrets, in a plain text file. This file, .claude/settings.local.json, can still leak sensitive information as older versions remain in the project's git history and forks. The recommended solution is to immediately rotate all passwords, tokens, and keys, then clean up.
Claude Code attempts to exclude the file from git commits, but this protection only applies to newly committed files, not those already committed. Apiiro's search found 104,185 copies of the file across 103,617 repositories, with 1,122 containing secrets. These secrets include 379 database passwords, 43 SSH logins for public servers, 42 tokens for GitHub, GitLab, and npm, and 23 AWS keys.
Several high-profile organizations, including a database vendor and a medical-records database owner, have been identified as file holders. The secrets are still present on the default branch of every repository, with 217 days having passed in half of them. The file also appears in 298 copies of the shared .claude/settings.json file, mostly containing allow rules.
Claude Code is the only coding agent confirmed to save the full approved command in a project file by default. Developers are advised to rotate their secrets and clean up the leaky files. Even files that never reach GitHub remain vulnerable, as they can be found on developer machines or within other files like npm packages, Docker images, or synced folders.
Common secret scanners like gitleaks and TruffleHog often miss these files due to the lack of verification steps.
Written by urgent.news from The Hacker News's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.