Singapore cyber agency urges stronger defences after fridge cyberattacks in Europe
No similar attacks have been reported in Singapore, but firms are urged to keep remote management interfaces off the public internet and strengthen access controls.
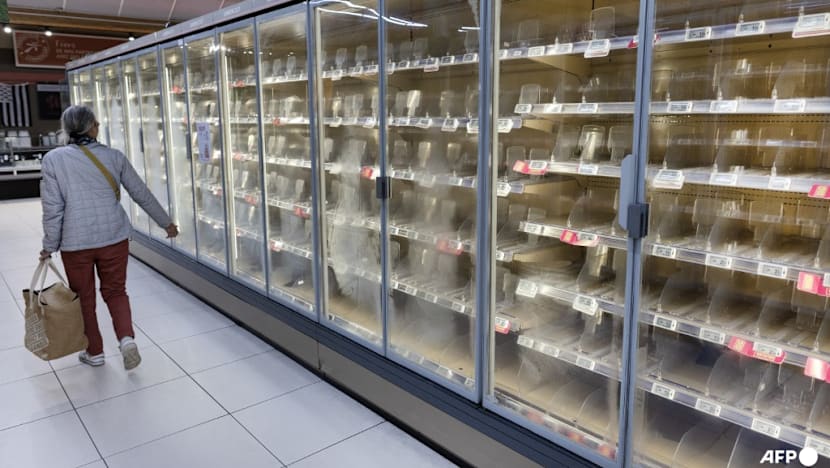
Singapore's cybersecurity agency, the Cyber Security Agency of Singapore (CSA), is urging organizations to bolster their defenses against cyberattacks targeting operational technology (OT) systems, following a series of incidents in Europe. These attacks have compromised refrigeration management systems at numerous supermarkets, highlighting the potential for disruptions to business operations, supply chains, and essential services beyond data loss.
Commissioner of Cybersecurity and CSA CEO Gwenda Fong emphasized that even sectors typically not considered cyber targets can be vulnerable. The CSA advised organizations to keep remote management interfaces off the public internet and strengthen access controls, as poorly secured remote access could allow attackers to manipulate equipment settings, disrupt operations, and pose safety risks. The recent attacks in Europe were reportedly due to poorly secured refrigeration controllers accessible over the internet.
The CSA is collaborating with the Singapore Food Agency and supermarket operators to enhance cybersecurity measures. Potential security weaknesses include weak or default credentials, outdated software, and insufficient access controls. To mitigate these risks, organizations should change default passwords, use strong and unique passwords, and implement secure remote access solutions such as VPNs, multi-factor authentication, and restricting access to authorized personnel.
Additionally, the CSA recommends updating and securing OT systems, implementing network segmentation and security monitoring, and strengthening operational monitoring and incident response. Organizations should also review obsolete equipment and put in place safeguards or replacement plans. In the event of an attack, incident response plans should enable safe isolation of affected systems and revert to local or manual controls to maintain critical operations.
Written by urgent.news from Channel News Asia's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.
This story
This is one outlet's version. Read the fullest account.
- Singapore cyber agency urges stronger defences after fridge cyberattacks in Europe channelnewsasia.com
- Blood banks and grocery stores across Europe hit by cyberattacks mashable.com
- French blood banks hacked amid ‘deeply concerning’ wave of fridge and freezer cyberattacks in Europe siliconangle.com
- Russia denies involvement in fridge hacks across Europe politico.eu
- Hackers escalate Europe's fridge attacks, now target France's blood banks malaysiakini.com