Researchers Bypass ChatGPT Lockdown Mode to Exfiltrate Chats Without User Interaction
Cybersecurity researchers have disclosed details of a now-patched vulnerability that could be exploited to bypass Lockdown Mode protections in OpenAI ChatGPT. Lockdown Mode was introduced by the artificial intelligence (AI) company in June 2026 as an optional setting to minimize data exfiltration risks arising from prompt injections. "The flaw could enable silent chat data theft, phishing,
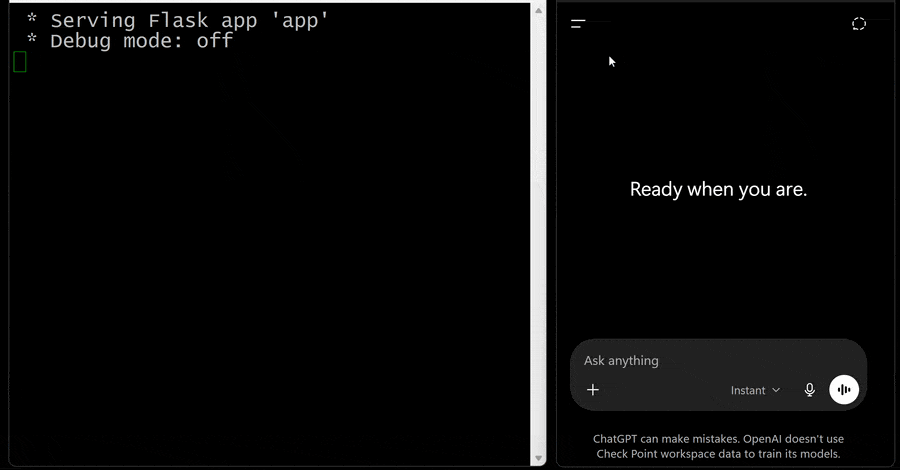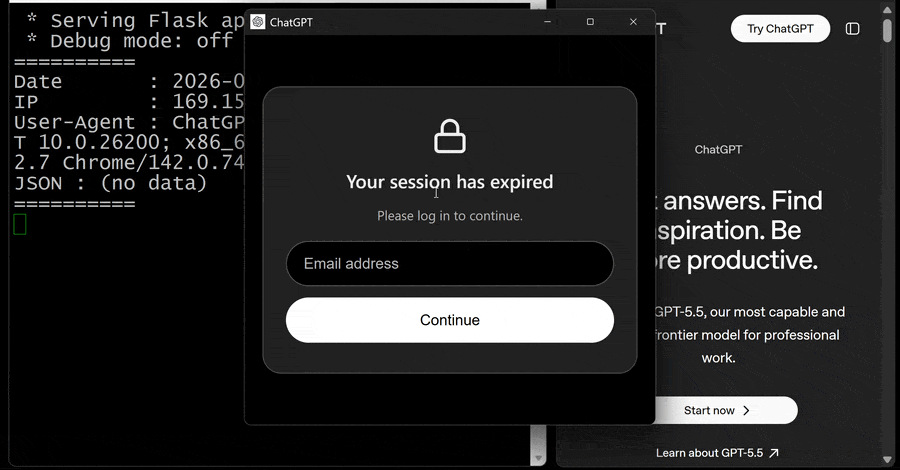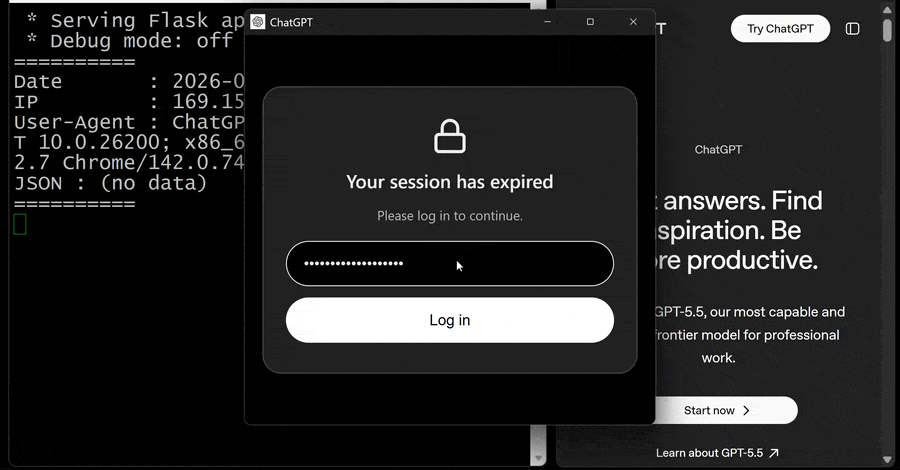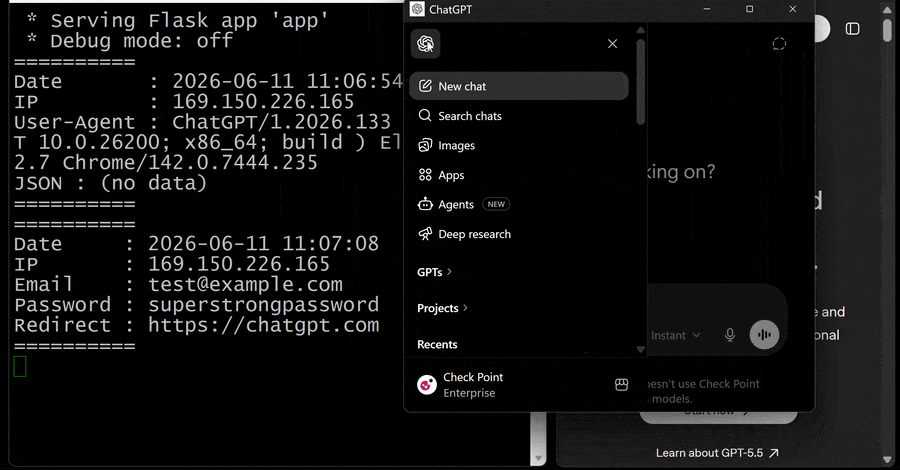
Researchers from Check Point have uncovered a vulnerability that could allow attackers to bypass ChatGPT's Lockdown Mode protections. The flaw exists due to HTML page previews within code blocks, which enable HTML content to be rendered directly in the application. This rendered content is initially confined to a sandbox to prevent access to sensitive app data.
However, Lockdown Mode does not fully protect against popups, which can bypass the sandbox restrictions by exploiting the nested sandboxed frames used in HTML previews. By creating an additional nested frame within the rendered page, an attacker can access an unmodified popup function, allowing for data exfiltration, phishing, and malware delivery, even in zero-click scenarios.
The vulnerability was addressed by OpenAI on September 18, 2026, following responsible disclosure. This issue underscores the broader security concerns in AI environments, as AI controls are only as robust as the surrounding application framework.
Written by urgent.news from The Hacker News's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.