ChatGPT now lets you generate GIFs
ChatGPT now allows users to make GIFs from text prompts or images, with OpenAI unveiling its Images 2.6 AI image generation model.
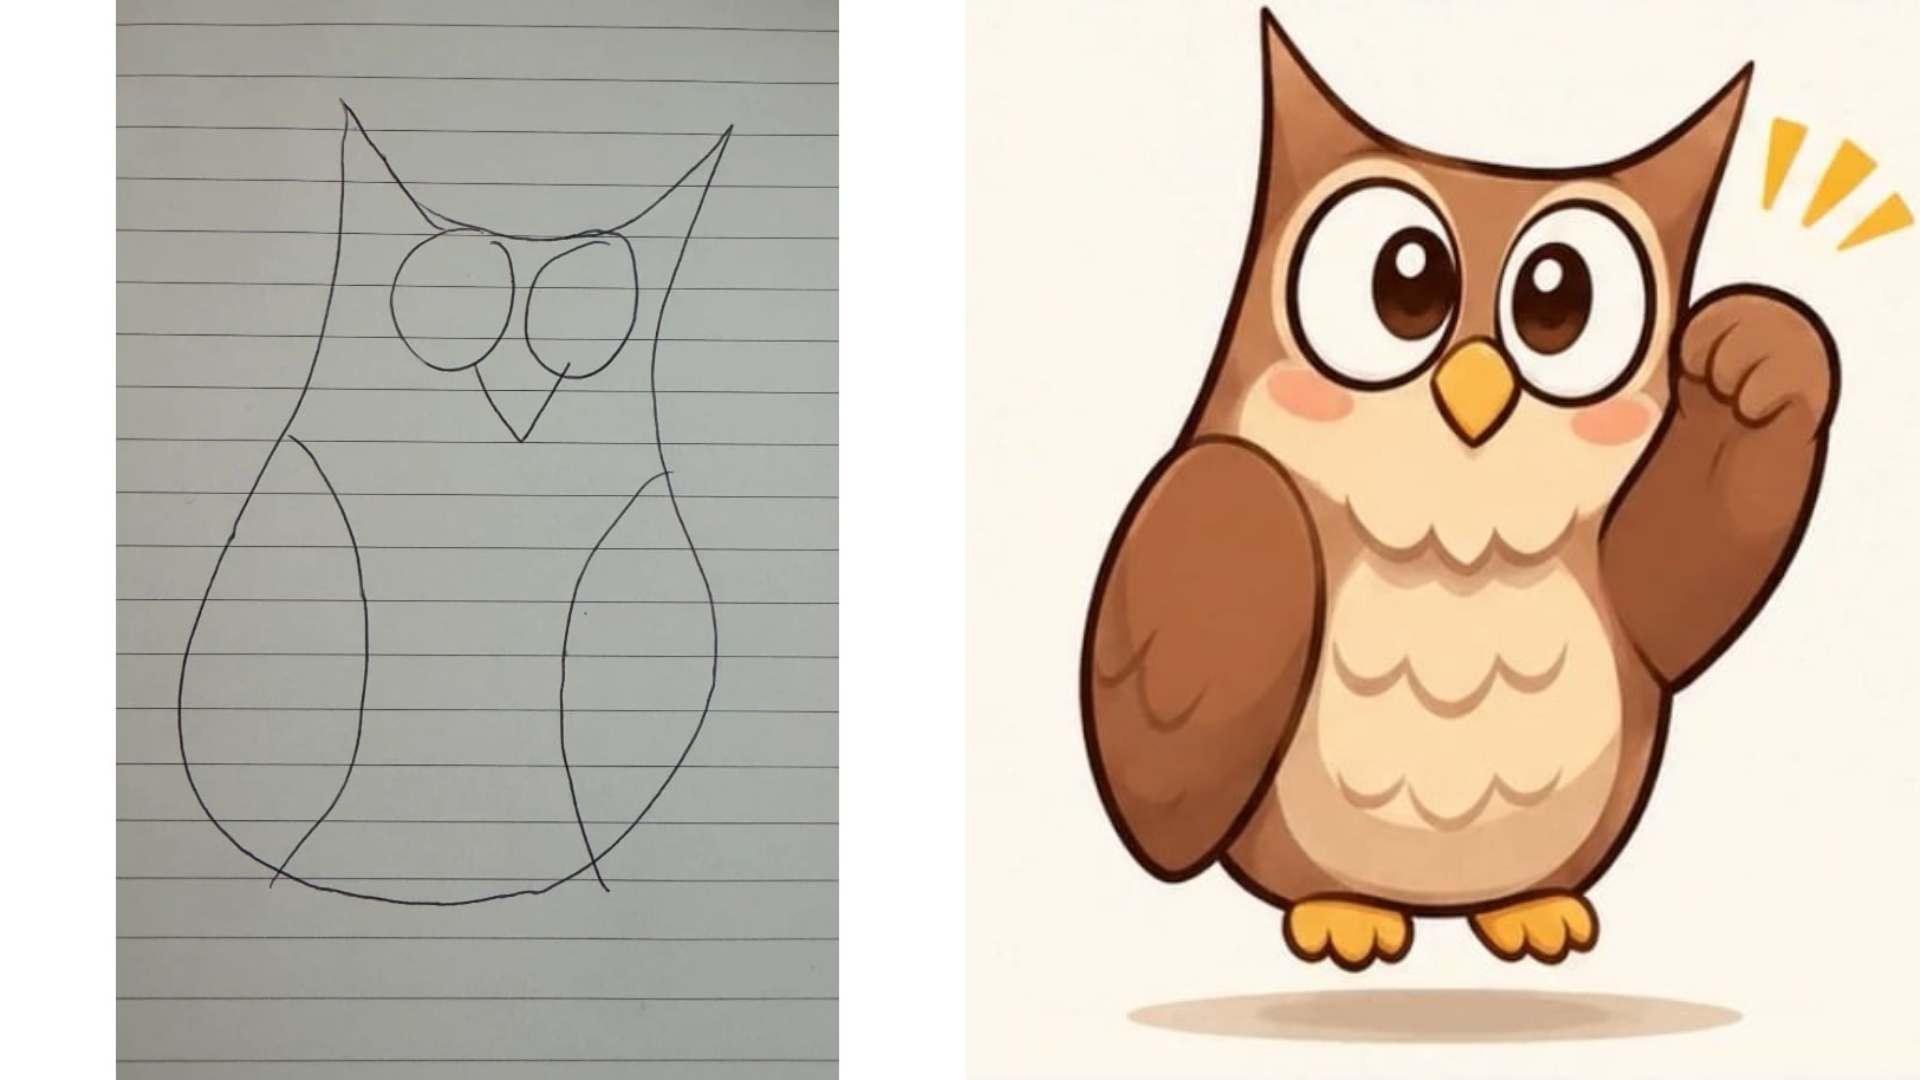
OpenAI has introduced a new feature to ChatGPT and its coding tool Codex, allowing users to generate GIFs from text prompts or uploaded images. The feature, powered by Images 2.6, OpenAI's latest AI image generation model, was unveiled on Wednesday and rolled out globally to both platforms today. Users can either describe the GIF they want to generate or upload an image to be animated.
They can also upload a rough drawing and have the AI model generate a more complete version to animate. Once generated, users can adjust the GIF's animation speed and view and edit individual frames. OpenAI stated that the GIF-generating capability is not an AI video generator, but rather a tool for creating animated storyboards or exploring character movement before video production.
The company has discontinued its AI video generation app Sora earlier this year due to few users and significant financial loss. Images 2.6 generates images 50 percent faster than its previous model, Images 2.5, and can create an image in about six seconds on the company's speed-focused GPT‑Image‑2.6 Flare model. The new feature is available across all ChatGPT and Codex subscription tiers.
Written by urgent.news from Mashable's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.
This story
This is one outlet's version. Read the fullest account.
- ChatGPT will now make you animated GIFs theverge.com