Why Europe's supermarket fridges were easy targets
BRUGES, Belgium — Hackers who cranked up fridge temperatures at supermarkets across Europe may have gained access through public internet-connected systems protected by default passwords or outdated software, a cybersecurity expert said. The second cyberattack in three weeks hit fridge systems at supermarket chains including Carrefour and Delhaize in Belgium, and ICA and Coop in Sweden, forcing…
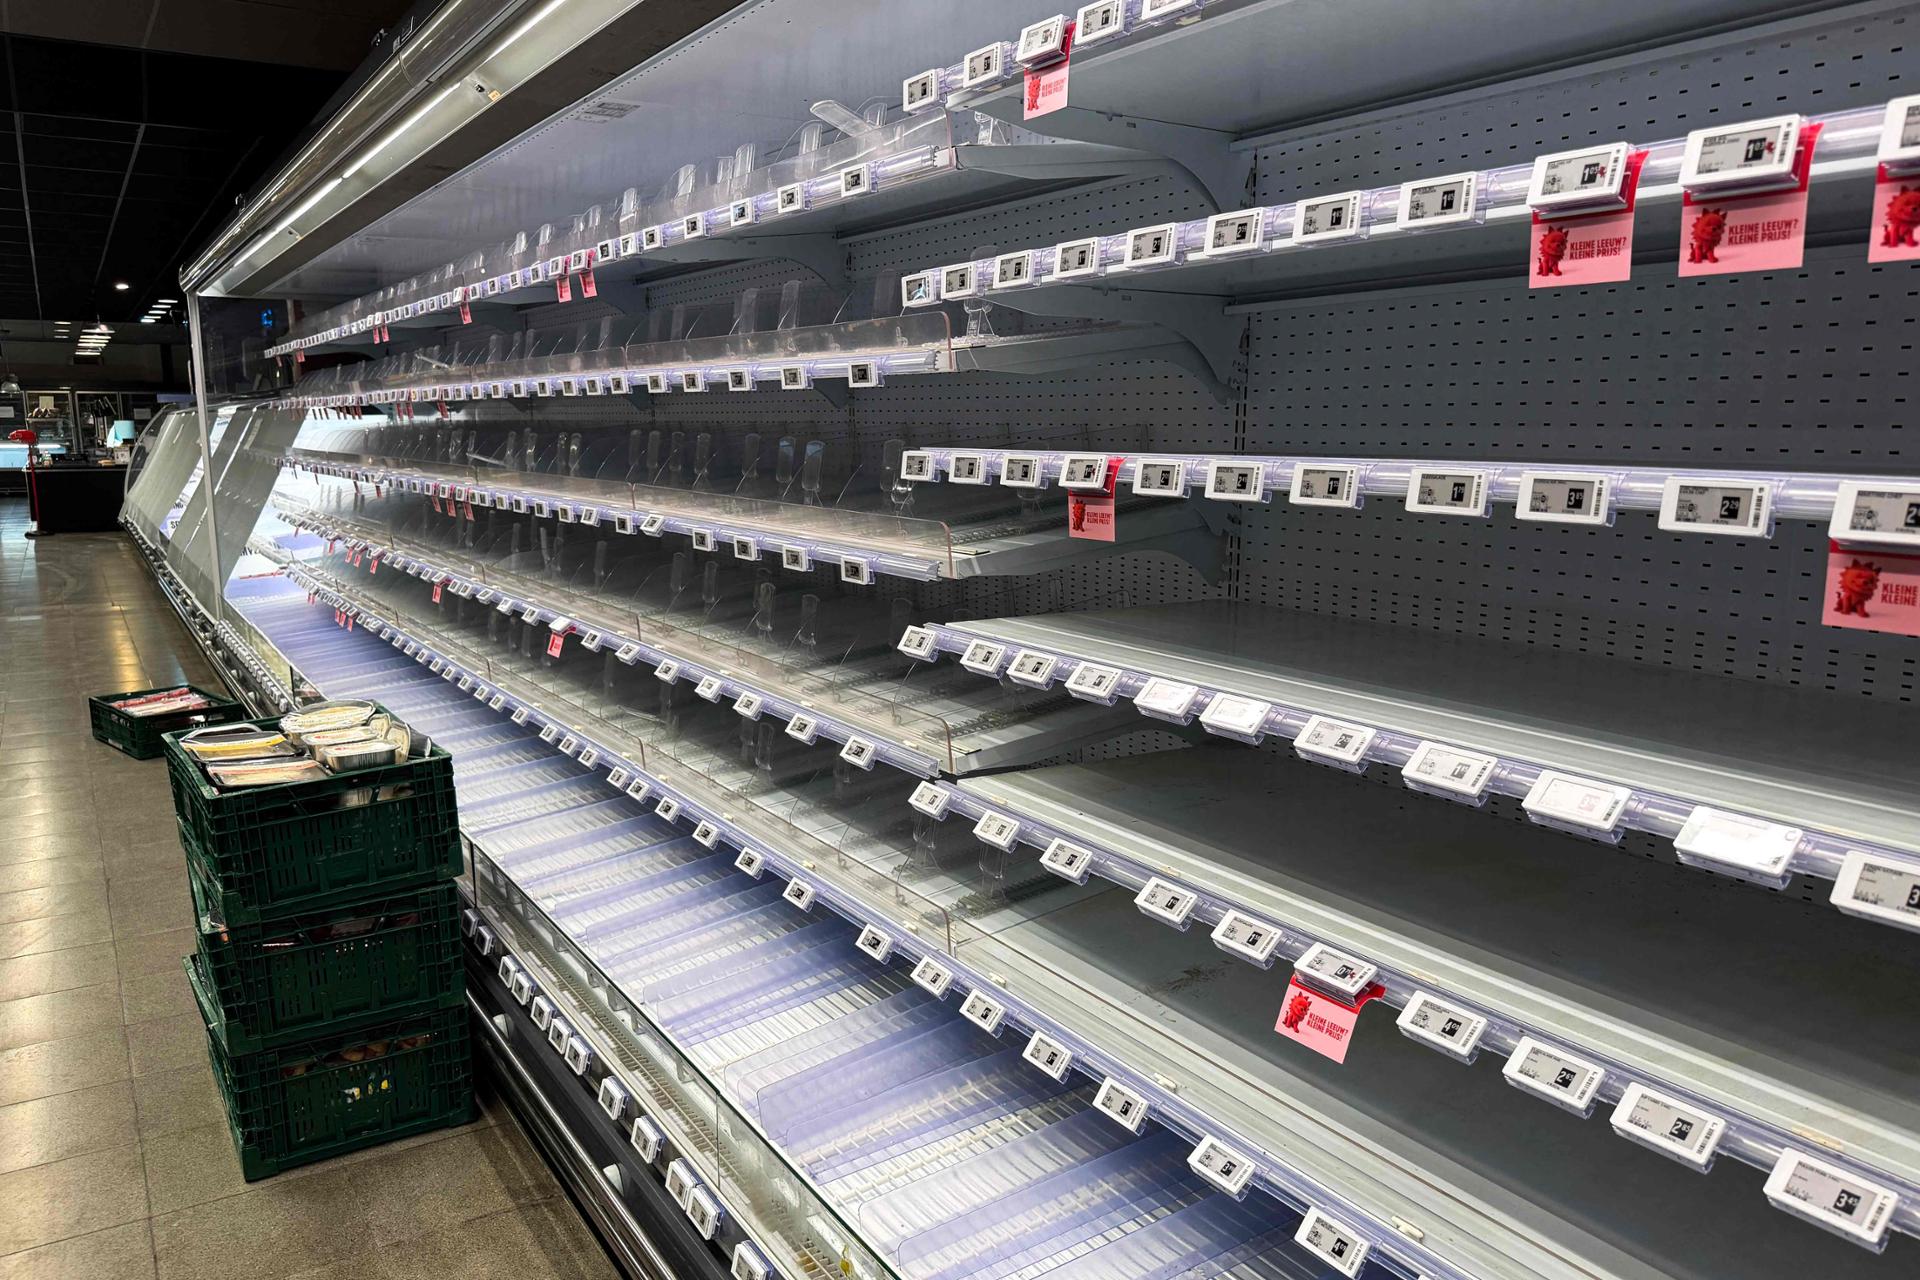
Bruges, Belgium — Cybersecurity experts suggest that hackers infiltrated supermarket refrigeration systems across Europe due to insufficient security measures, such as using default passwords or outdated software. The recent attack affected various supermarket chains in Belgium, Sweden, and France, including Carrefour, Delhaize, ICA, and Coop.
These incidents led retailers to discard spoiled products, raising alarms about the vulnerability of food supply chains. Three blood banks in France were also targeted. The source of the attack remains unknown, and no perpetrator has been identified. Laurens Singier, an ethical hacker and researcher at the Cyber 3 Lab in Bruges, explained that internet-connected systems, especially those accessible remotely, often lack robust security.
He emphasized that these devices should not be connected to public internet networks, as they are more susceptible to exploitation.
Written by urgent.news from The Korea Times's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.
Also reported by 2 other outlets
- Why Europe's supermarket fridges were easy targets koreatimes.co.kr
- Why Europe's supermarket fridges were easy targets channelnewsasia.com