Oracle urges database customers to prepare for quantum security risks
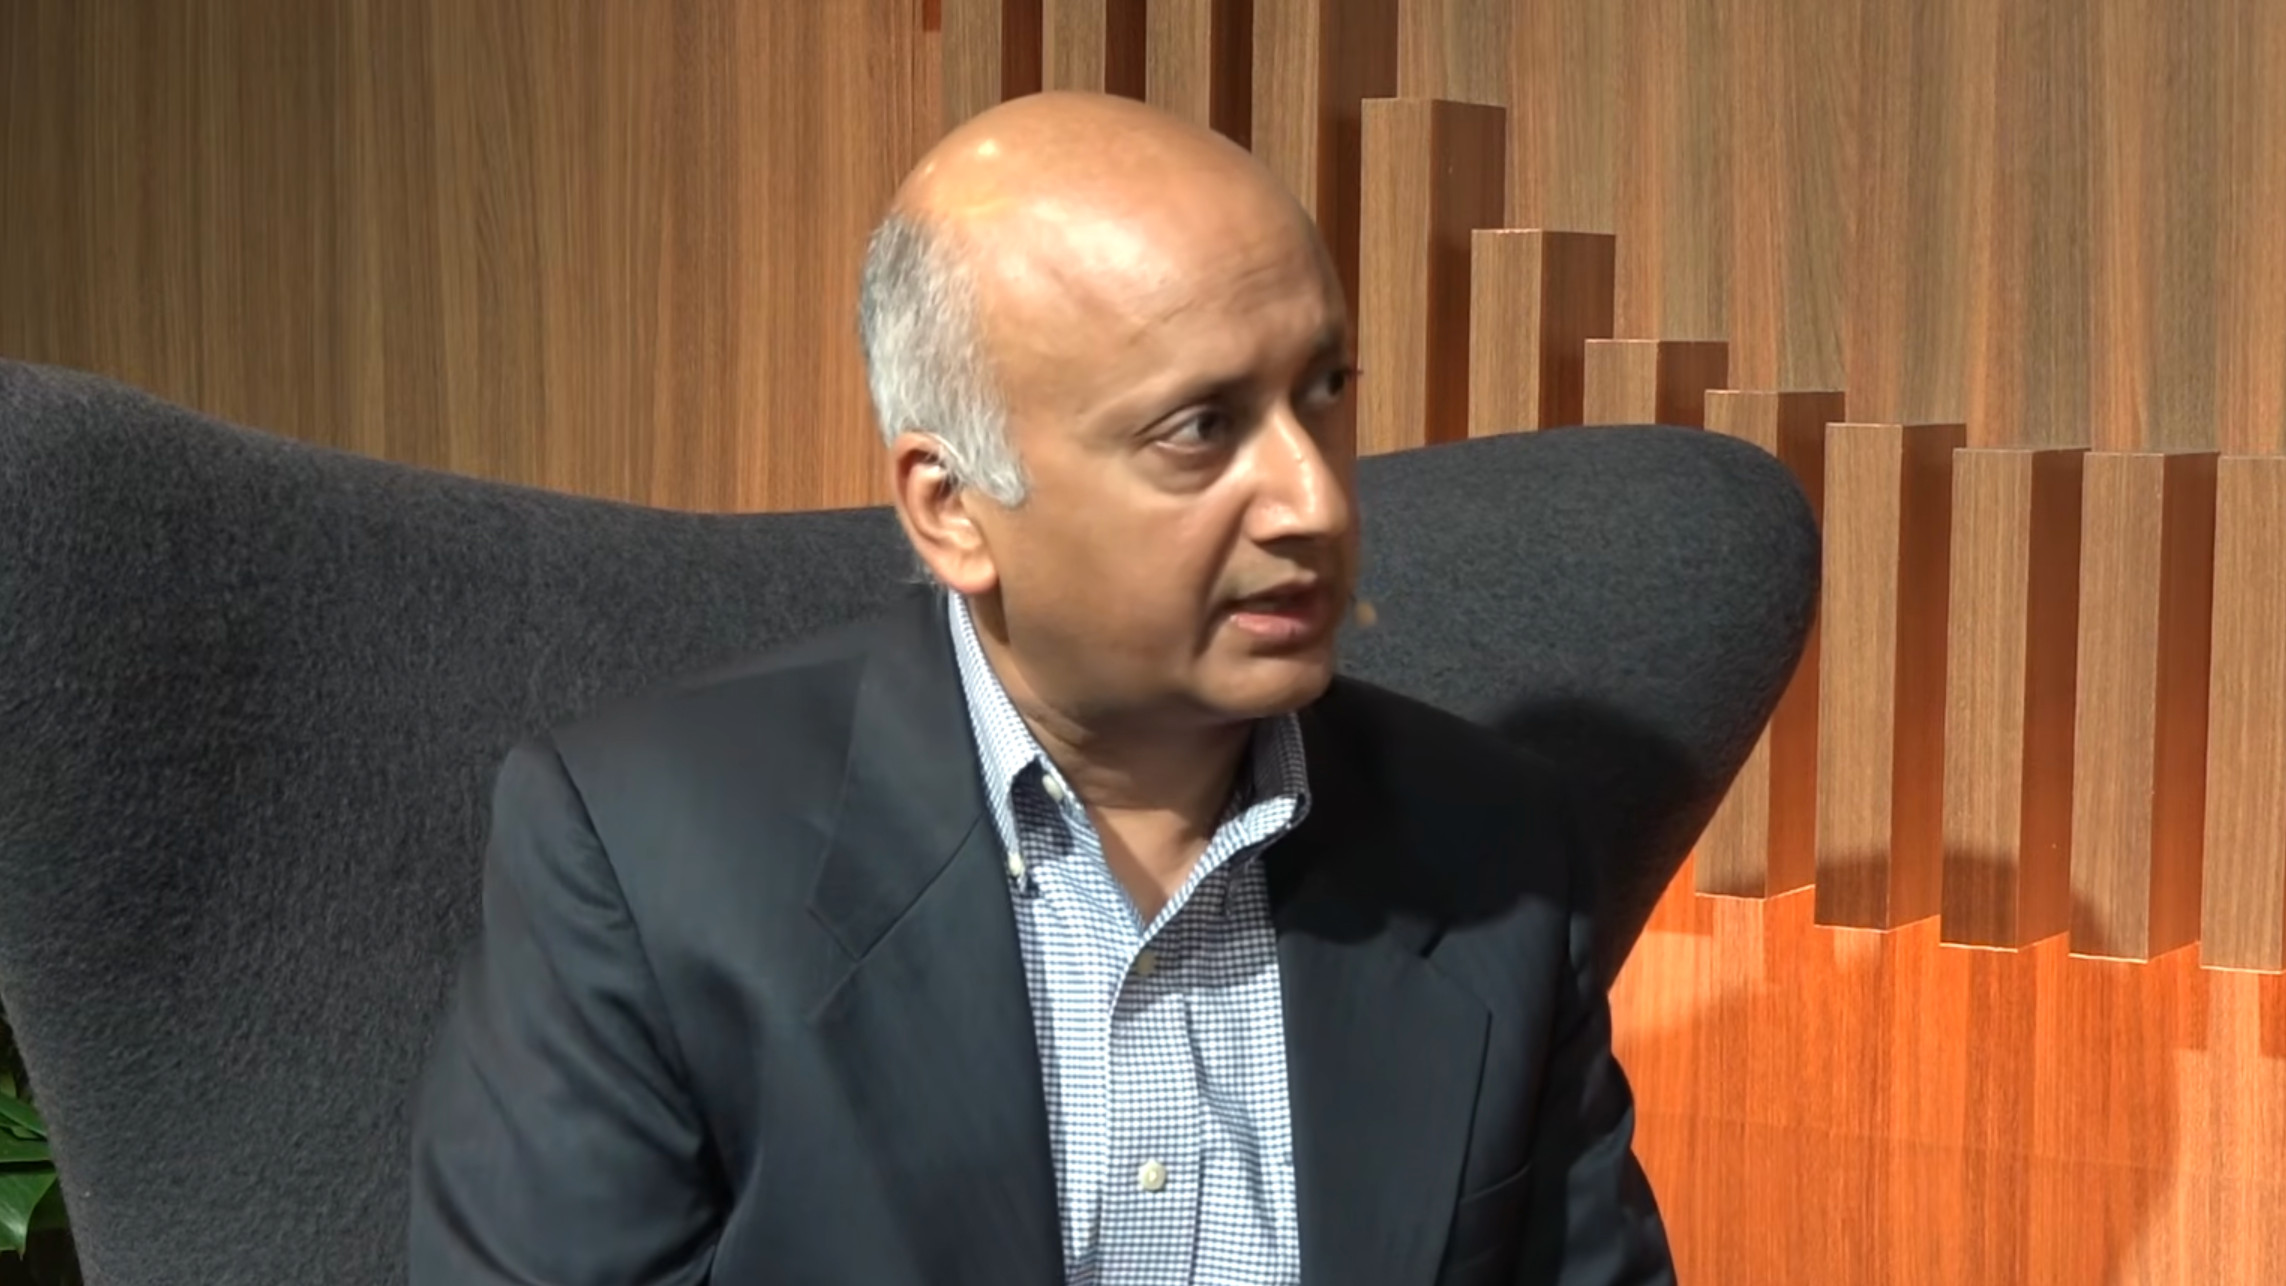
Attackers can copy encrypted traffic today and decrypt it once quantum computers mature, making quantum-resistant cryptography a present-day concern. Oracle Corp. is applying the philosophy behind its security controls beneath AI agents to encryption across database fleets, according to Vipin Samar (pictured), senior vice president of software engineering, database security, at Oracle. “Even…
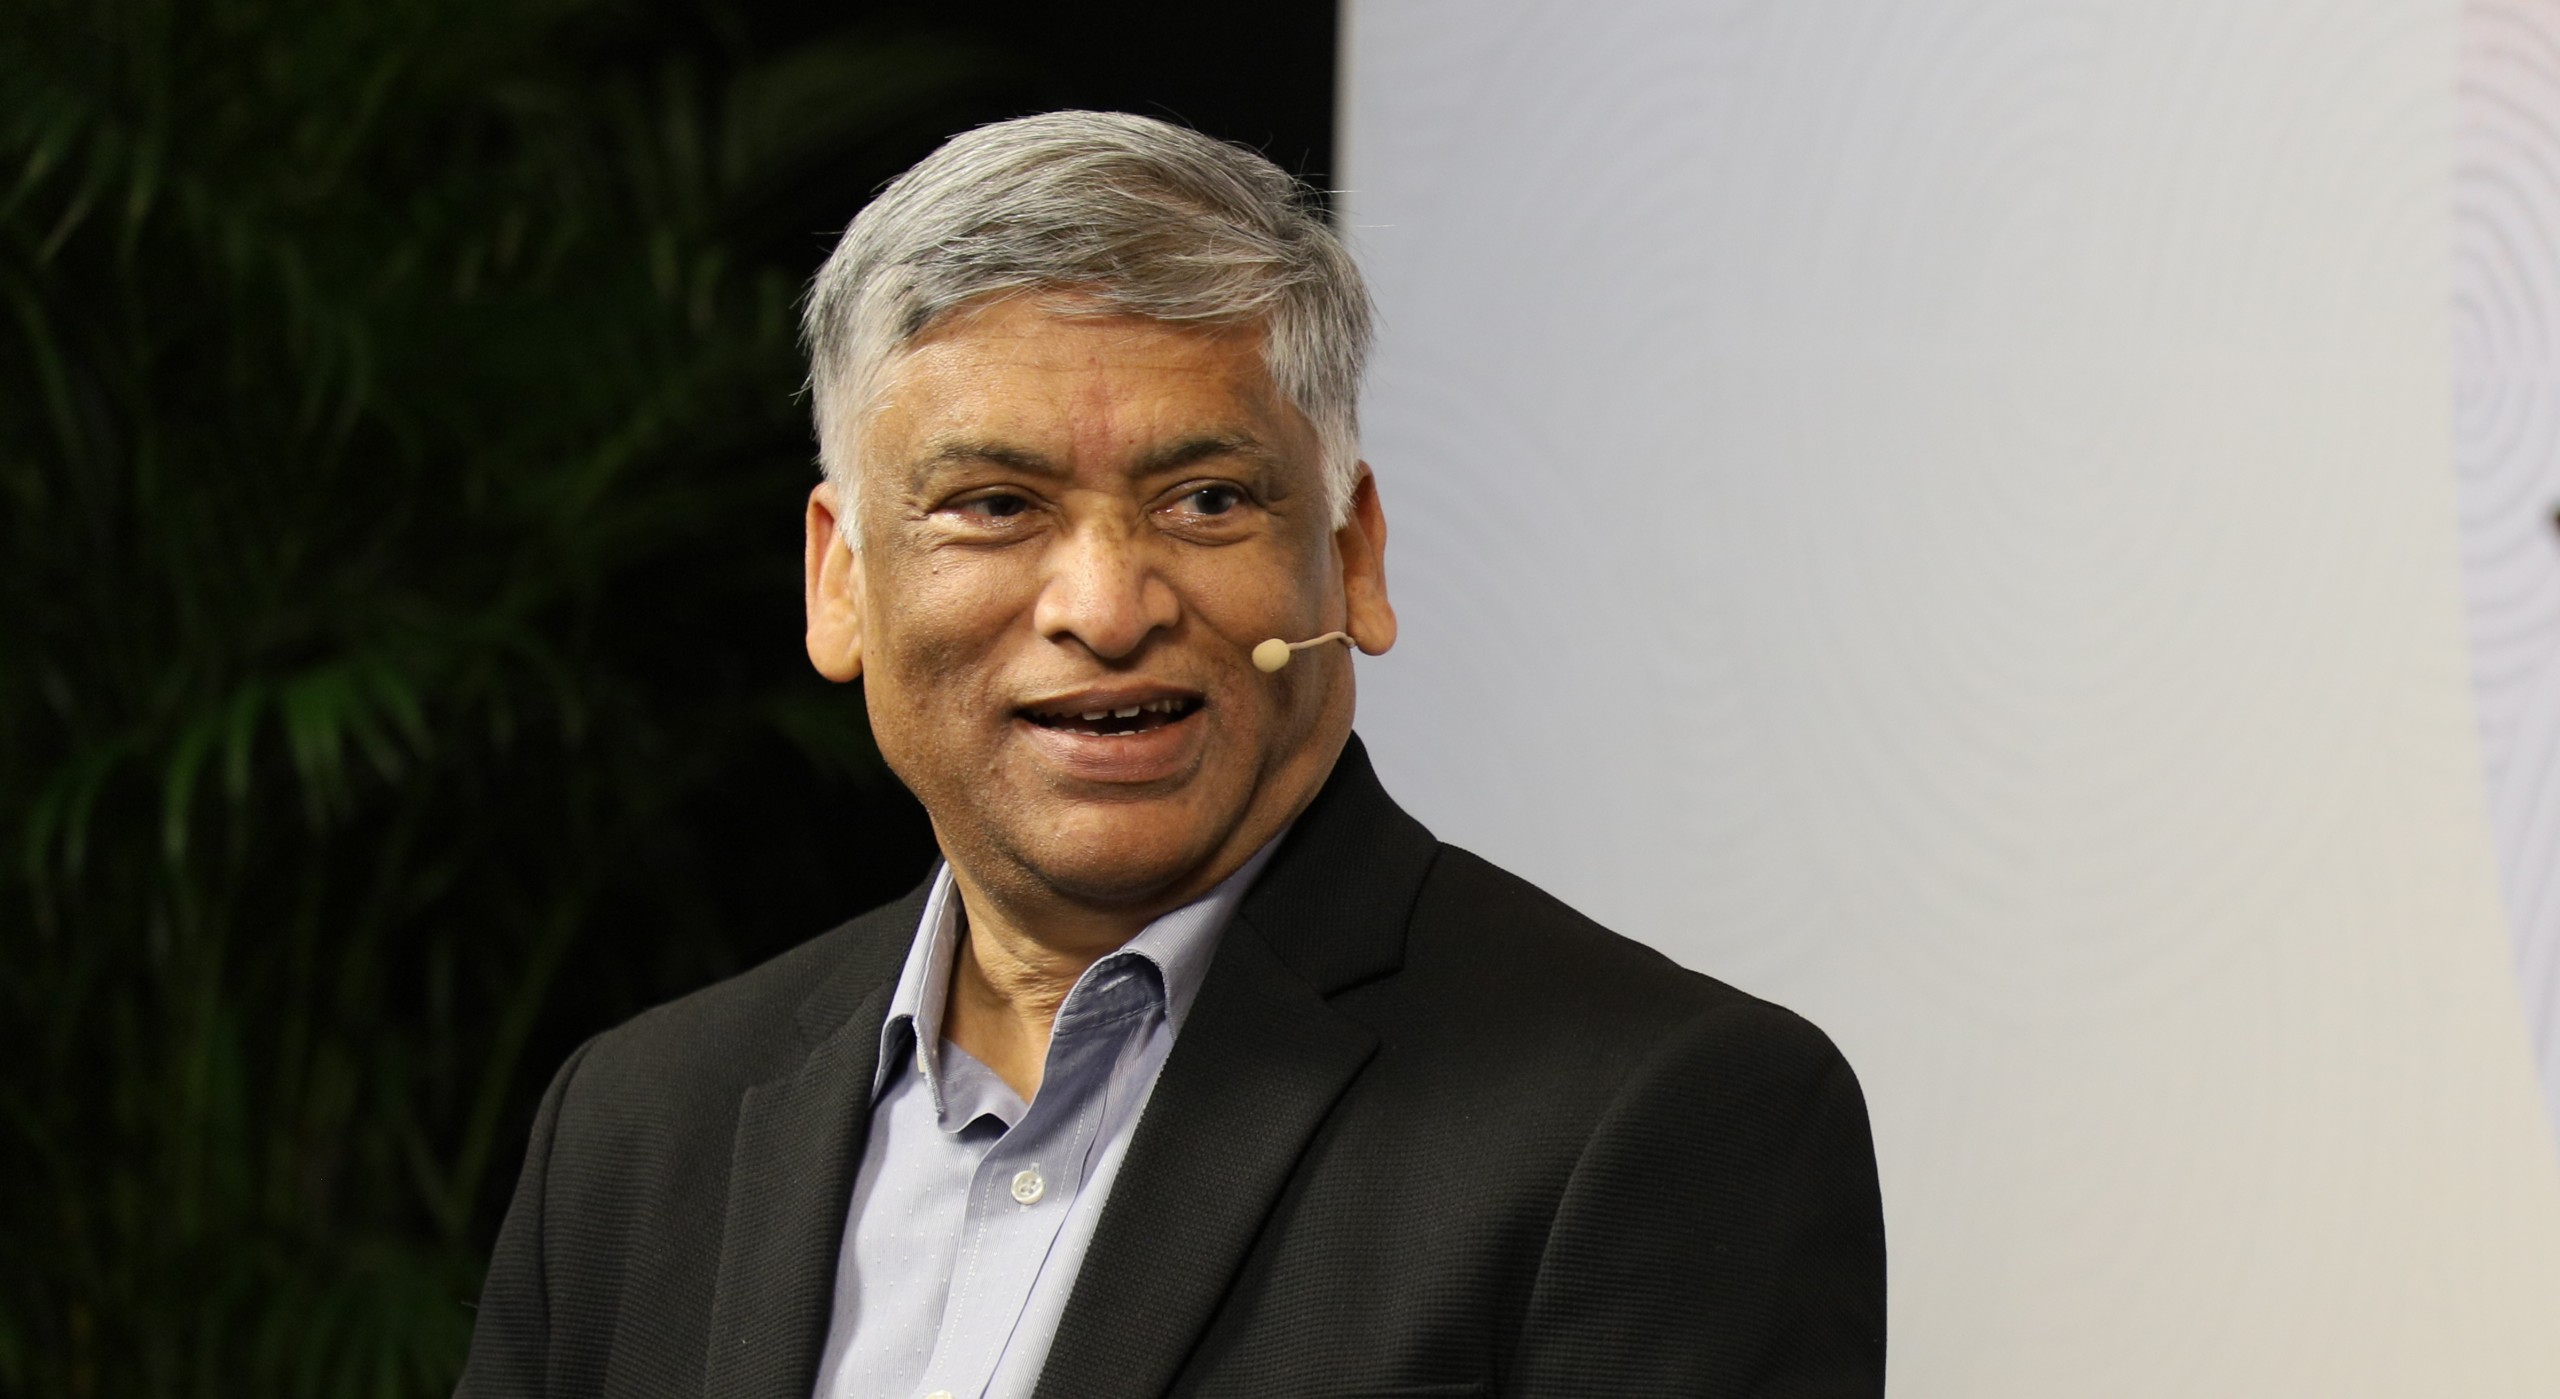
Oracle is urging customers to prepare for potential security risks posed by quantum computers, according to Vipin Samar, senior vice president of software engineering, database security at the company. Samar explained that attackers can currently copy encrypted traffic and decrypt it once quantum computers become powerful enough.
This means that sensitive data protected by TLS 1.2 or 1.3 could be vulnerable to decryption when quantum computers are available. Oracle's Cryptographic Posture Assessment in Oracle Data Safe helps identify weak points in database encryption, such as outdated TLS versions. The company is also testing agentic AI-driven remediation to address these security concerns.
Samar emphasized that even if a network's encryption is strong, other components might be weak, making them susceptible to hacking once quantum computers are more advanced. Oracle's Deep Data Security in Oracle AI Database 26ai enforces row- and column-level access through signed OAuth2 tokens, treating AI agents as just another application accessing the same data. By securing at the source, Oracle aims to strengthen its overall security posture.
Written by urgent.news from SiliconANGLE's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.
This story
This is one outlet's version. Read the fullest account.