Hacker-Attacke: Sabotage an Kühlanlagen: Experte rügt Hersteller
Ob Kühlanlage oder Wärmepumpe: Vernetzte Technik kann Angriffsflächen bieten. Ein anerkannter Experte fordert deshalb auch strengere Prüfungen – was sich aus seiner Sicht ändern muss.
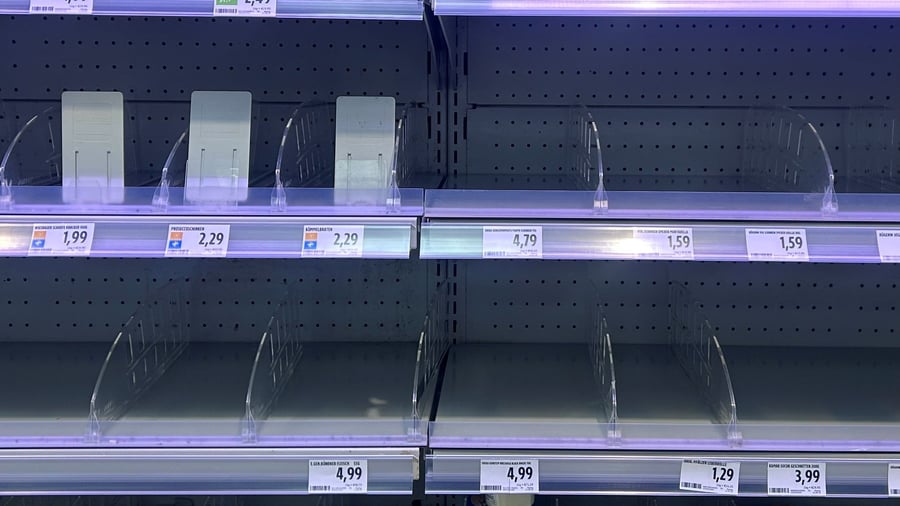
Cyberattacks on refrigeration systems in European and German supermarkets highlight the responsibility of manufacturers of connected devices, according to Karlsruhe IT security expert Christoph Fischer. He criticized the delivery of control systems with unchanged factory settings and default passwords as a grave oversight. "That is unforgivable," Fischer told Deutsche Presse-Agentur (dpa).
Affected operators should have received updates from the manufacturer long ago, which prescribe mandatory changes to such standard access credentials. Secure encryption has been feasible for some time. Fischer believes manufacturers should design their systems so that individual passwords are assigned at the first commissioning.
While remote access for maintenance purposes is generally useful, there are sufficient technical means nowadays - like certificates and asymmetric encryption - to safeguard against such access. Running everything on modern control processors already provides enough computational power. Fischer warned against limiting the discussion to the food retail sector, as connected technology is now widespread in various domains, from solar panels to heat pumps.
Even household appliances are increasingly being unnecessarily connected. "It doesn't have to be on the internet," Fischer cautioned. If network access becomes unavoidable, robust protection mechanisms must be in place. Moreover, the security expert called for more rigorous checks: consumer protection organizations, such as the Stiftung Warentest, should integrate mandatory minimum IT security requirements as a fixed criterion into their assessments.
Written by urgent.news from Handelsblatt's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.