Critical Rails Flaw Lets Attackers Write Server Files via Crafted ImageMagick Uploads
A critical flaw in Ruby on Rails could allow an unauthenticated attacker to write arbitrary files on an app's server by uploading a crafted file if the app processes uploads using ImageMagick. The Rails project disclosed the flaw in an advisory and fixed it in versions 8.1.4.1 and 8.0.5.2. The flaw is in Active Storage, the part of Rails that handles file uploads. Some apps store
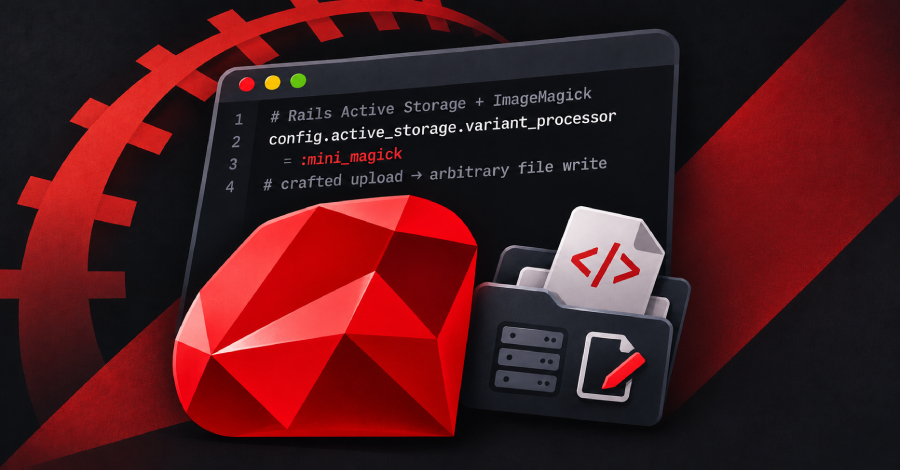
A critical vulnerability in Ruby on Rails, discovered by RyotaK via HackerOne, permits unauthenticated users to write arbitrary files to a server by exploiting ImageMagick functionality when processing file uploads. This issue stems from Active Storage, the file upload management system within Rails. The flaw exists in versions prior to 8.1.4.1 and 8.0.5.2, affecting apps that utilize Active Storage's Disk service for storage.
In such cases, attackers could potentially gain access to sensitive data like the app's secret_key_base and system credentials, leading to remote code execution or lateral movement. ImageMagick selects a coder based on the file content, and Active Storage lacks any restrictions on which coders can be used for uploads. The Rails project addressed this vulnerability in versions 8.1.4.1 and 8.0.5.2.
It is important to note that not all apps are impacted by this flaw; an app is vulnerable only if it processes uploads using the Disk service and has not implemented the fix. The advisory does not confirm if the flaw has been exploited, but Rails strongly recommends upgrading immediately due to the high severity of the issue.
Written by urgent.news from The Hacker News's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.