APT29-Linked Hackers Hijack Web Analytics Script to Deliver iOS and Android Exploits
The Russia-linked threat actor known as APT29 is said to be behind a large-scale watering hole campaign targeting iOS and Android users through compromised websites, fake domains, and a supply chain attack involving a Ukrainian web analytics service called Plerdy SEO Tracker. "The injected JavaScript code collects browser and device attributes," Sekoia researchers Amaury-Jacques Garçon and
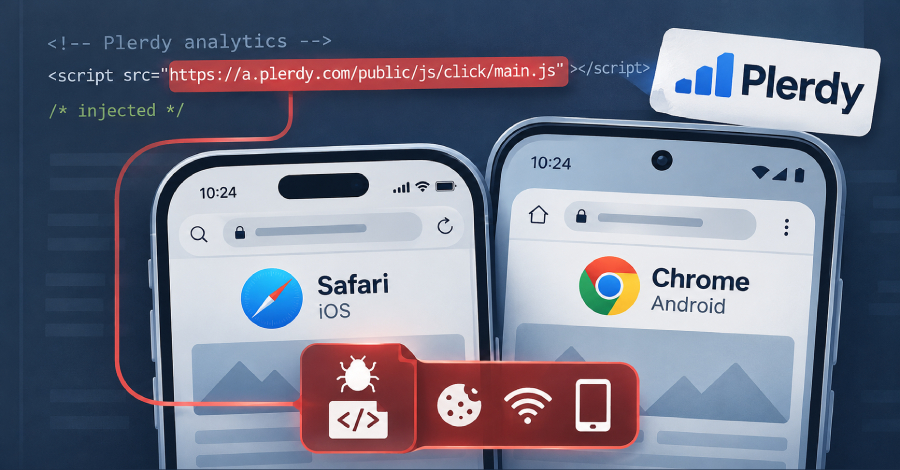
A Russia-linked hacking group called APT29 is responsible for a widespread watering hole campaign targeting users of iOS and Android devices. Compromised websites, fake domains, and a Ukrainian web analytics service called Plerdy SEO Tracker were used to inject malicious JavaScript code that collects browser and device attributes.
This code then delivers a specific exploit chain tailored to either iOS or Android devices. The ultimate goal of the attacks is to steal browser cookies and, in some cases, Wi-Fi passwords or full mobile device data. The campaign, known as Poisoned Source, was discovered by French cybersecurity firm Sekoia in mid-October 2026. The compromised websites included major industry trade associations, a far-right European political party, and Bulgarian military-related websites.
The attackers may have targeted specific individuals rather than a broad audience, but it's unclear whether they sought to compromise as many unpatched mobile devices as possible. The supply chain attack spread through high-value targets, such as army, special forces, and military equipment websites. Three different exploits have been identified, with each delivering data to the ad.starx-net[.]com:8881/telemetry/v12 endpoint.
One exploit checks if the targeted device is a Samsung Galaxy S25 Ultra and terminates exploitation if it matches. The adoption of packaged N-day exploit chains, like DarkSword, lowers the cost and technical threshold required for advanced mobile exploitation. The P7 variant of DarkSword was delivered via half-click attacks using ad-based infrastructure and through criminal campaigns like DeadTag, which acquires expired domains behind old analytics and advertising tags.
Written by urgent.news from The Hacker News's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.