UK food suppliers hit by European cyberattacks
British food suppliers have been caught up in a wave of cyberattacks targeting supermarket refrigerators across Europe, prompting warnings that outdated technology is leaving the UK’s food supply chain exposed. The National Cyber Security Centre (NCSC) confirmed on Tuesday that vulnerable refrigeration technology had been exploited in a small number of incidents in Britain, after [...]
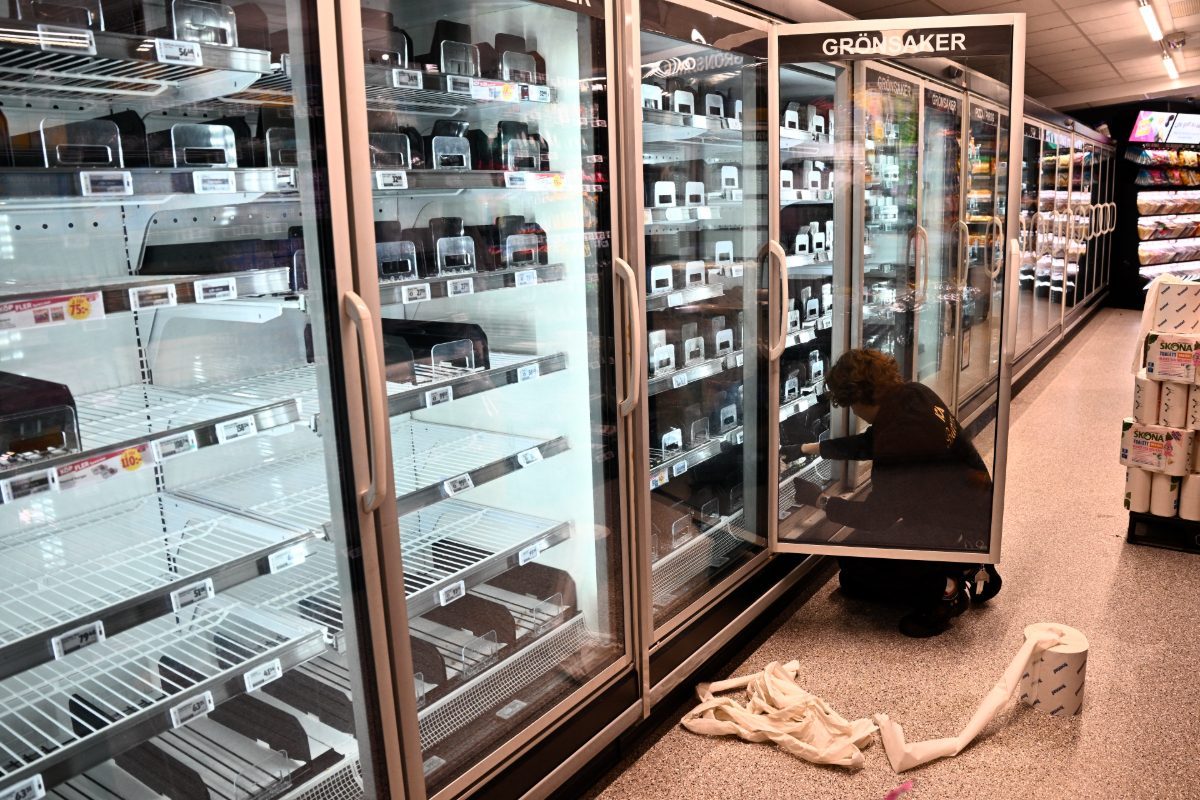
British food suppliers have fallen victim to a series of cyberattacks targeting supermarket refrigerators across Europe, raising concerns about the vulnerability of the UK's food supply chain. The National Cyber Security Centre (NCSC) revealed on Tuesday that outdated technology in refrigeration systems had been exploited in a few incidents in the UK, after hackers remotely manipulated fridge temperatures in several European countries.
This forced retailers in Sweden, Belgium, Ireland, and other nations to discard significant amounts of fresh and frozen food as refrigeration systems were forced into defrost mode. Richard Horne, NCSC chief executive, stated that the agency worked through the night to warn potentially affected British businesses. The British Association of Independent Meat Suppliers confirmed that some of its 300 members had been impacted, though no inventory was lost.
These attacks follow a similar incident last month affecting hundreds of French supermarkets, causing millions of euros in damage after hackers exploited vulnerabilities in remotely managed fridges. Cybersecurity researchers have identified more than 800 fridge interfaces associated with British retailers accessible over the public internet, although this does not guarantee hacking capability.
Martin Riley, Bridewell's chief technology officer, warned that the food industry is particularly exposed due to perishable products and the critical need for tightly controlled temperatures. He noted that a supermarket fridge holds no secrets and that changing its temperature overnight can destroy the value of its contents within hours, with no backup to restore the lost stock.
Riley emphasized that attackers are increasingly targeting operational technology, which controls physical equipment, rather than just stealing data or disrupting IT networks. The incidents have heightened concerns about the broader consequences of cyberattacks on essential infrastructure, especially as supermarkets rely more on internet-connected equipment and third-party contractors.
Charl van der Walt, Orange Cyberdefense's global head of security research, stated that the cyberattacks on UK and European supermarkets demonstrate how incidents can quickly escalate beyond IT disruption, affecting food supplies, businesses, and consumers. The motives and identity of the attackers remain unclear, but van der Walt highlighted that attacks do not need to be designed to spread fear to cause that effect.
Ed Hayes, data protection partner at TLT law firm, pointed out that operational technology has historically been a cybersecurity blind-spot, with retailers prioritizing payment systems and customer data over refrigeration and logistics equipment. He noted that legacy OT systems, never designed with cyber resilience in mind, are frequently still in use and often operate without basic security controls.
The latest incidents follow cyberattacks on Marks & Spencer and the Co-op last year, disrupting deliveries and leaving supermarket shelves empty. The British Retail Consortium said retailers are collaborating with the NCSC to enhance their defenses against similar attacks. However, the NCSC has not identified the perpetrators of the latest incidents, stating it is too early to determine who is behind them.
Written by urgent.news from City AM's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.