NIS asks 2,100 public institutions to conduct emergency cybersecurity checks
SEOUL, Nov. 3 (Yonhap) -- South Korea's spy agency has asked 2,100 public instit...
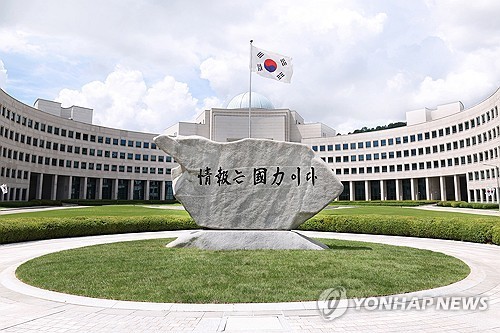
SEOUL, Nov. 3 (Yonhap) -- South Korea's spy agency, the National Intelligence Service (NIS), has instructed 2,100 public institutions to conduct emergency cybersecurity inspections in the wake of recent cyberattacks on financial firms that led to customer data breaches, according to government sources on Tuesday. The NIS has requested that central and local government agencies perform security checks using a checklist, the sources revealed.
Additionally, the NIS intends to carry out its own vulnerability assessments of critical information and communications infrastructure within its purview, the sources added. These assessments are projected to be finalized by mid-November. The cyberattacks targeted various local financial entities, including banks, savings banks, and insurance companies, resulting in the exposure of around 100,000 instances of personal information, such as email addresses, names, and phone numbers.
The NIS has emphasized the importance of addressing potential cyberattack entry points, the functioning of security monitoring systems, and the implementation of security patches. Furthermore, the agency is conducting direct vulnerability assessments of internet-facing systems at public-sector facilities classified as critical information and communications infrastructure.
Written by urgent.news from Yonhap News's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.