Binance Reveals How Fake Job Interviews and AI Tool Abuse Led to $6.43 Billion Theft
Binance on Tuesday said the record-setting theft of $6.43 billion in assets from the world's largest cryptocurrency exchange was the culmination of a "sophisticated, multi-stage campaign" that involved the use of a tampered Homebrew installation and recruitment-themed social engineering attack targeting two of its engineers. "It was not a single isolated breach or a simple phishing incident,"
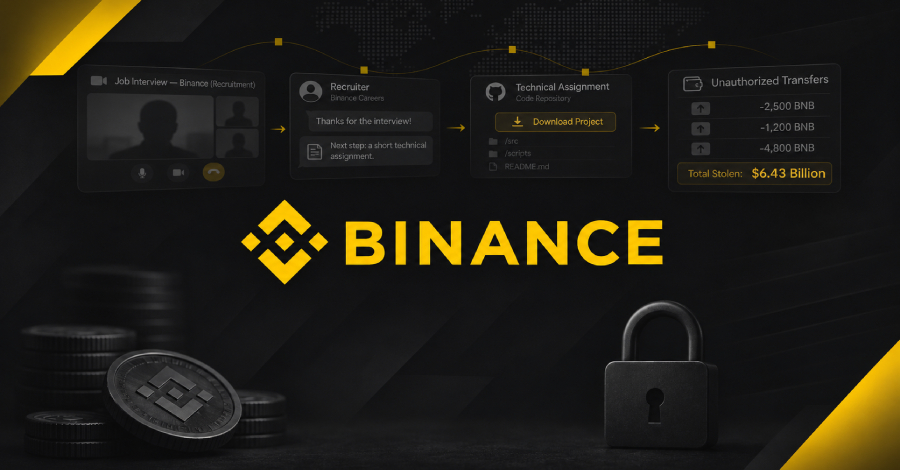
Binance disclosed on Tuesday that the $6.43 billion theft from its platform was the result of a complex, multi-stage attack involving multiple techniques. The breach began in June 2026 when an engineer, Engineer A, inadvertently downloaded a malicious Homebrew installer, leading to the theft of sensitive information about his and his colleagues' roles within the Wallet DevOps team.
In September 2026, another engineer, Engineer B, was lured into a fake job interview by a threat actor posing as a Project Director. During the interview, Engineer B was asked to download a malicious code repository, which initiated a series of unauthorized activities. By October 2026, the attacker had gained control over Engineer A and another Wallet Software Engineer C using an internal AI tool.
The attacker then exploited a container deployment permission token on Engineer A's computer to initiate the theft. Binance has since reconstructed the affected wallet system and internal AI tool, implemented tighter device controls, and enhanced wallet-service risk controls. Additionally, they have expanded AI-based behavioral anomaly detection and increased investment in AI-enabled detection, endpoint protection, developer-environment security, and behavioral anomaly monitoring.
Since the beginning of the year, Binance has reportedly thwarted 57 suspected North Korea-linked cyber threat cases.
Written by urgent.news from The Hacker News's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.