Adopt a cyber warfare legal framework for true resilience
MALAYSIA has a law to protect its critical systems. It has no law to answer when another state attacks them. Today’s warning from the Prime Minister shows why that gap must close.
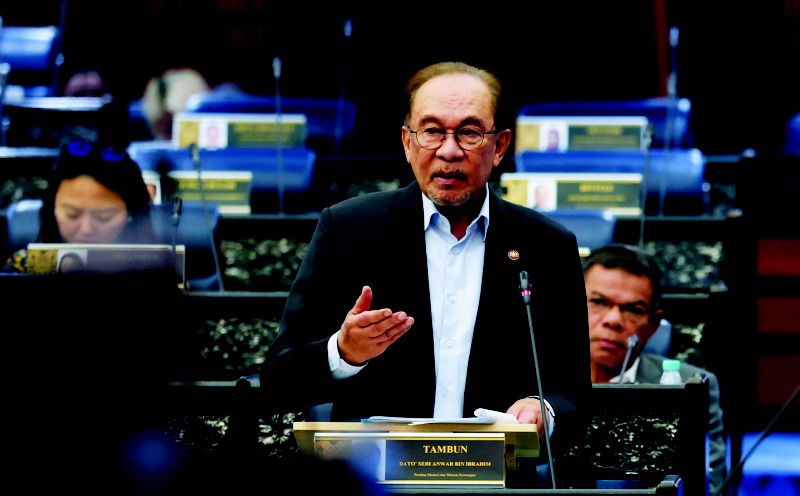
Malaysia has a law to safeguard its vital systems, but it lacks legislation to handle when an external state launches an attack. Prime Minister Datuk Seri Anwar Ibrahim recently warned the House of Representatives that Malaysia is indeed among the nations deemed potential targets of cyber and hybrid threats. This is not merely about crime; he emphasized the possibility of cyber warfare, which involves hostile activities potentially orchestrated by a state, aiming to disrupt a nation's infrastructure and sway its will.
He highlighted two reasons for this vulnerability. Firstly, Malaysia's data centers and digital infrastructure now rival those of Europe. Secondly, Malaysia's principled stance on Palestine and Gaza has rendered it unpopular in certain capitals. While these factors hold national pride, they also make the country susceptible to cyber attacks, especially as incidents targeting portals, public registries, and government systems have recently shaken Europe, the United States, and Japan.
A special National Security Council meeting was convened on Monday, involving all departments under the Chief Secretary, a meeting with Bank Negara, and a closed-door briefing with MPs. These are crucial initial measures, but a nation cannot simply brief its way through a war. It requires comprehensive legal frameworks. Currently, Malaysia's resilience lacks a cyber warfare framework.
The Cyber Security Act 2024 (Act 854), effective since August 26, 2024, represents a significant milestone. It established a National Cyber Security Committee headed by the Prime Minister, conferred statutory authority on the National Action Plan for Cyber Security (NACSA), and imposed obligations on National Critical Information Infrastructure (NCII) entities across eleven sectors, encompassing codes of practice, risk assessments, audits, and incident reporting.
However, this act primarily focuses on resilience and compliance, asking whether critical operators are secure and whether they report incidents. It fails to address the critical question of what legal actions Malaysia can take when confronted by a foreign state or its proxies, and the aim is coercion rather than theft. A cyber warfare legal framework is essential for resilience.
There are five key gaps that need to be addressed. First, Malaysia lacks a legal definition of cyber warfare, distinguishing it from cyber crimes, cyber incidents, and cyber attacks by states. Without this distinction, every response remains ad hoc. Secondly, there is no threshold or escalation ladder to determine when a cyber operation becomes a national emergency or a use of force under international law.
Thirdly, there is no attribution process for identifying the state responsible for an attack, including the criteria and consequences involved. Fourthly, the legal basis for response is absent. The powers of NACSA, MKN, the Ministry of Defence, and the Armed Forces to respond, including lawful countermeasures and active defense, are not explicitly outlined in law.
Lastly, there is no protection for civilians in cyber conflicts. Malaysia's framework does not legally commit the country to the principles of distinction, proportionality, and precaution in cyber warfare. Estonia and Singapore have taken different approaches to cyber resilience and defense. Estonia, after experiencing cyber attacks in 2007 that crippled its banks, media, and ministries, integrated cyber into its national defense by creating a military cyber command, a volunteer Cyber Defence Unit, and actively participating in NATO's cyber defense center of excellence in Tallinn.
Singapore, on the other hand, developed its framework incrementally. Its Cybersecurity Act 2018, a model for Malaysia's own, protects critical infrastructure, and a 2024 amendment extended its scope to cloud, data centers, and other digital foundations. However, Singapore went beyond regulation by incorporating Digital Defence into its Total Defence doctrine and establishing the Digital and Intelligence Service as a fourth branch of its armed forces.
Malaysia should adopt a similar approach, treating cyberspace as a domain where war can be waged and legislating accordingly. The proposed Cyber Warfare Legal Framework should include definitions and thresholds for cyber attacks, state-sponsored operations, and warfare, as well as a clear escalation ladder. This should be accompanied by a statutory cyber emergency regime, outlining the processes for declaring a national cyber emergency and the powers it grants, with firm sunset clauses and parliamentary oversight.
Attribution and lawful response mechanisms must also be established, enabling a formal process for determining the state behind an attack and the consequences of such actions. A legislated chain of command is necessary to define the roles of NACSA, MKN, the Ministry of Defence, and the Malaysian Armed Forces, specifying when a cyber attack becomes a defense matter and when the Armed Forces' cyber units should take the lead.
Humanitarian safeguards must be incorporated, committing Malaysia to the principles of distinction, proportionality, and precaution in cyber operations, and protecting civilian infrastructure such as hospitals, water supplies, and power grids. Finally, Malaysia should adopt a whole-of-society approach, extending the Act's reach to data centers, cloud services, and supply-chain vendors, ensuring comprehensive cyber resilience.
Written by urgent.news from New Straits Times's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.