Building Production MCP Servers & Tool-Calling AI Agents: Sandboxing, Schemas & Approval Gates
Most "AI agent" demos stop at the happy path: the model picks a tool, the tool returns JSON, everyone claps. Production is different. The moment an agent can call refund_order , run_sql , or send_invoice against a real tenant's data, you are no longer building a chatbot. You are building a privileged RPC surface that takes instructions from untrusted text. At Loop Origin we build custom SaaS…
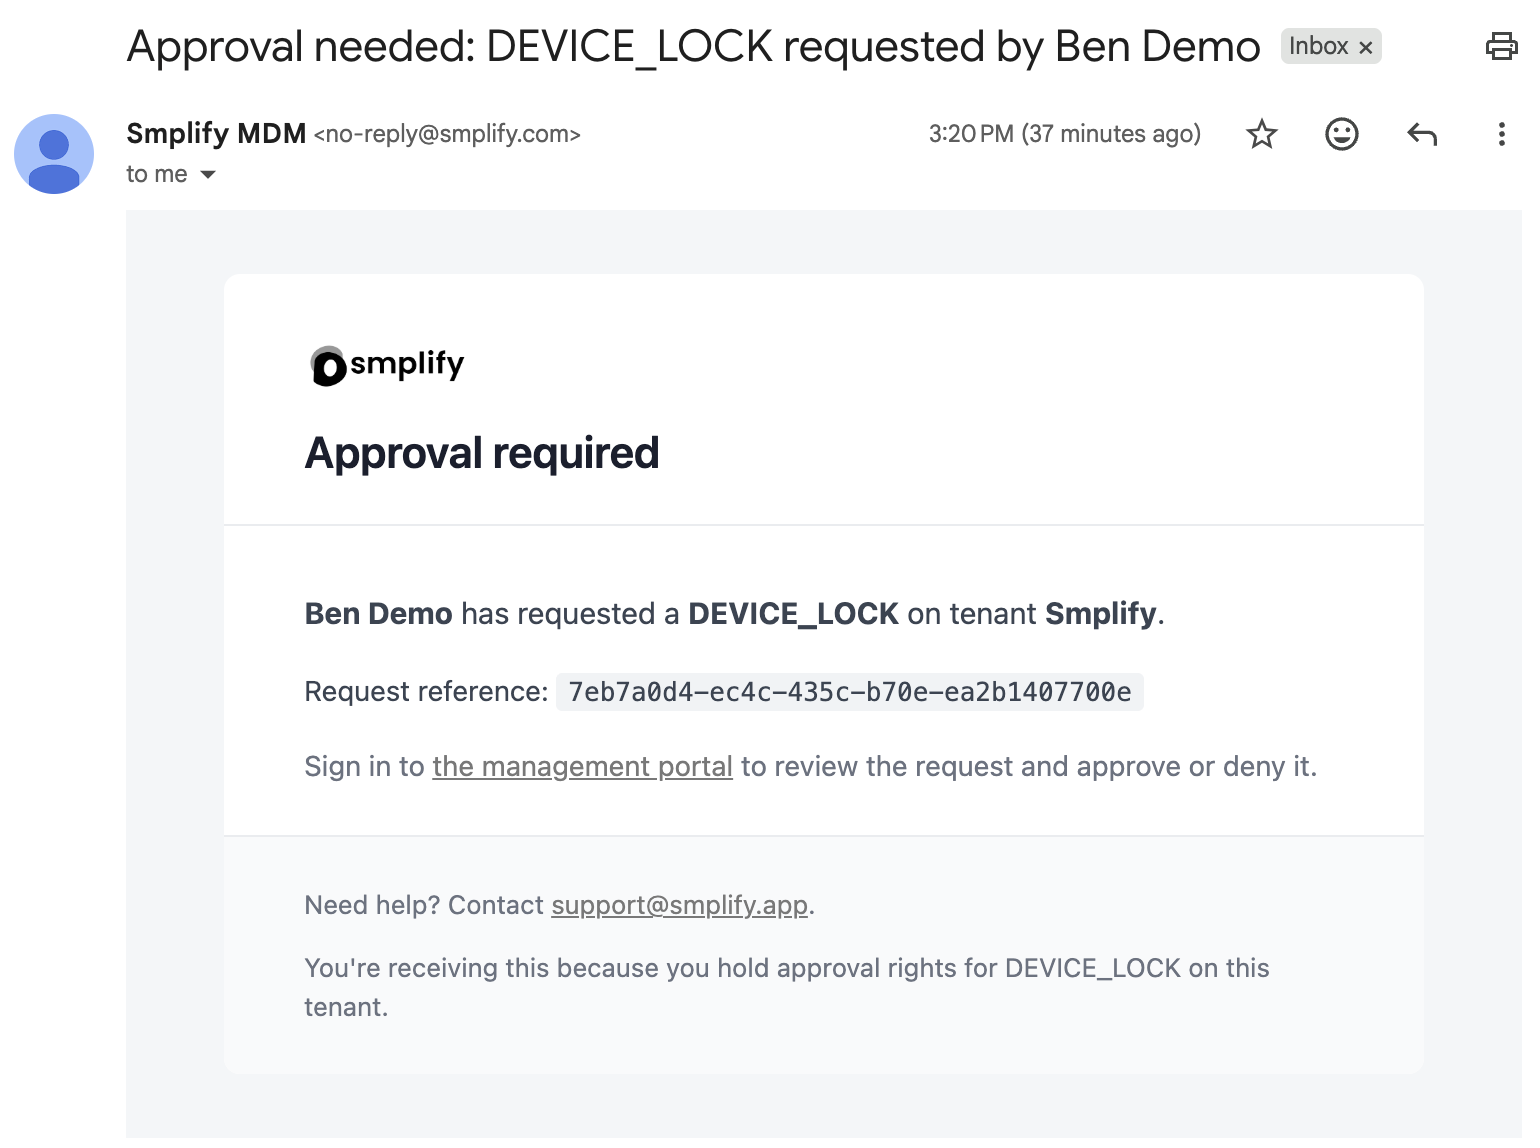
Building secure MCP servers for AI agents involves treating every tool call as untrusted input and enforcing strict validation. Define narrow, validated JSON schemas for each tool and run calls under scoped credentials per tenant. Separate read and write tools, require human approval for irreversible actions, and enforce timeouts and rate limits.
Log all calls with arguments, approver, and result for audit and replay. This approach treats tool-calling agents as a security boundary rather than a feature, protecting against model compromise and ensuring production-safe interaction with business systems.
Written by urgent.news from Dev.to's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.