FBI leads action to shut down Virtualine bulletproof service linked to major cybercrime activity
Virtualine was hosting illegal forums and helping launder stolen cryptocurrency.
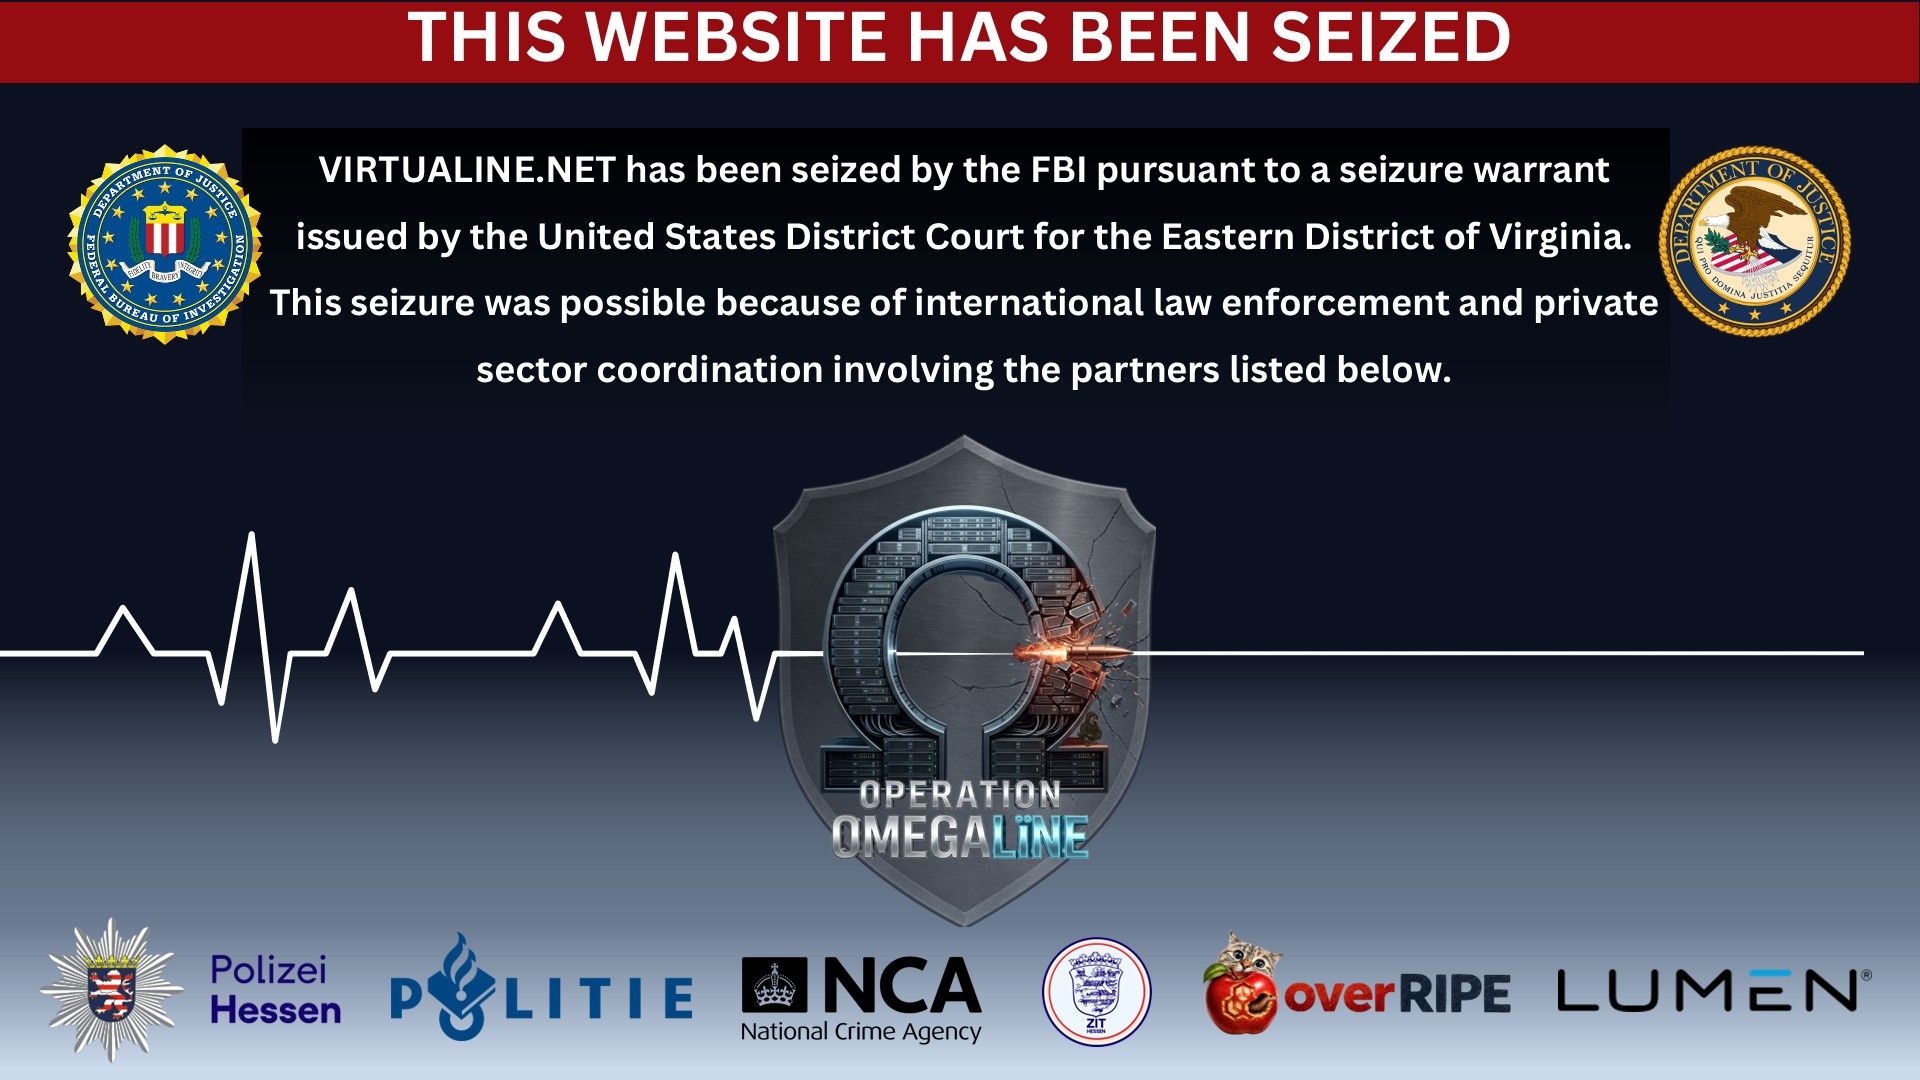
The FBI, along with international partners, successfully dismantled the Virtualine bulletproof hosting service, which was linked to extensive cybercrime activities. The service allegedly facilitated phishing, ransomware operations, illicit cryptocurrency transactions, and other crimes. Authorities seized servers and customer data, although no arrests have been made yet.
The FBI seized the website of Virtualine, a bulletproof hosting service that allegedly allowed child pornography, laundered stolen and extorted cryptocurrency, and enabled a variety of illegal activities. The operation involved a partnership with German and Dutch authorities, as well as multiple private companies, who conducted raids at a data center in Limburg to seize "dozens of physical servers" that also hosted "hundreds" of virtual servers.
This resulted in the FBI gaining access to information about over 3,000 of Virtualine's customers. The police are currently pursuing follow-up actions against these users. Bulletproof hosting refers to a subset of hosting providers that are unusually resistant to pressure from law enforcement agencies. While some of these services have legitimate uses in countries with strong censorship or for protecting website owners' identities, Virtualine was found to be openly criminal.
The FBI had previously warned that Virtualine advertised its services to criminals on cybercrime forums and even offered an "additional protection plan" to help clients evade takedown requests. Despite Virtualine claiming it did not accept child pornography or terrorism content, the DOJ stated that the company engaged in these activities.
One of Virtualine's clients created a forum for the sale of explicit images and videos, including those of minors, which Virtualine continued to host despite warnings from law enforcement agencies in Germany, Canada, and Australia. The company even provided customers with unhosted Bitcoin addresses to facilitate payments without raising suspicion.
Chainalysis data revealed that Virtualine's wallet received funds from ransomware operations, infostealers, Russian-language cybercrime forums, and other illicit sources. The FBI defaced Virtualine's main website, replacing it with the standard "this website has been seized" message. However, no arrests have been made, suggesting that the service will likely remain partially online and resume operations soon.
Written by urgent.news from TechRadar's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.