Urgent.News

What's breaking now, across thousands of outlets.

Tech

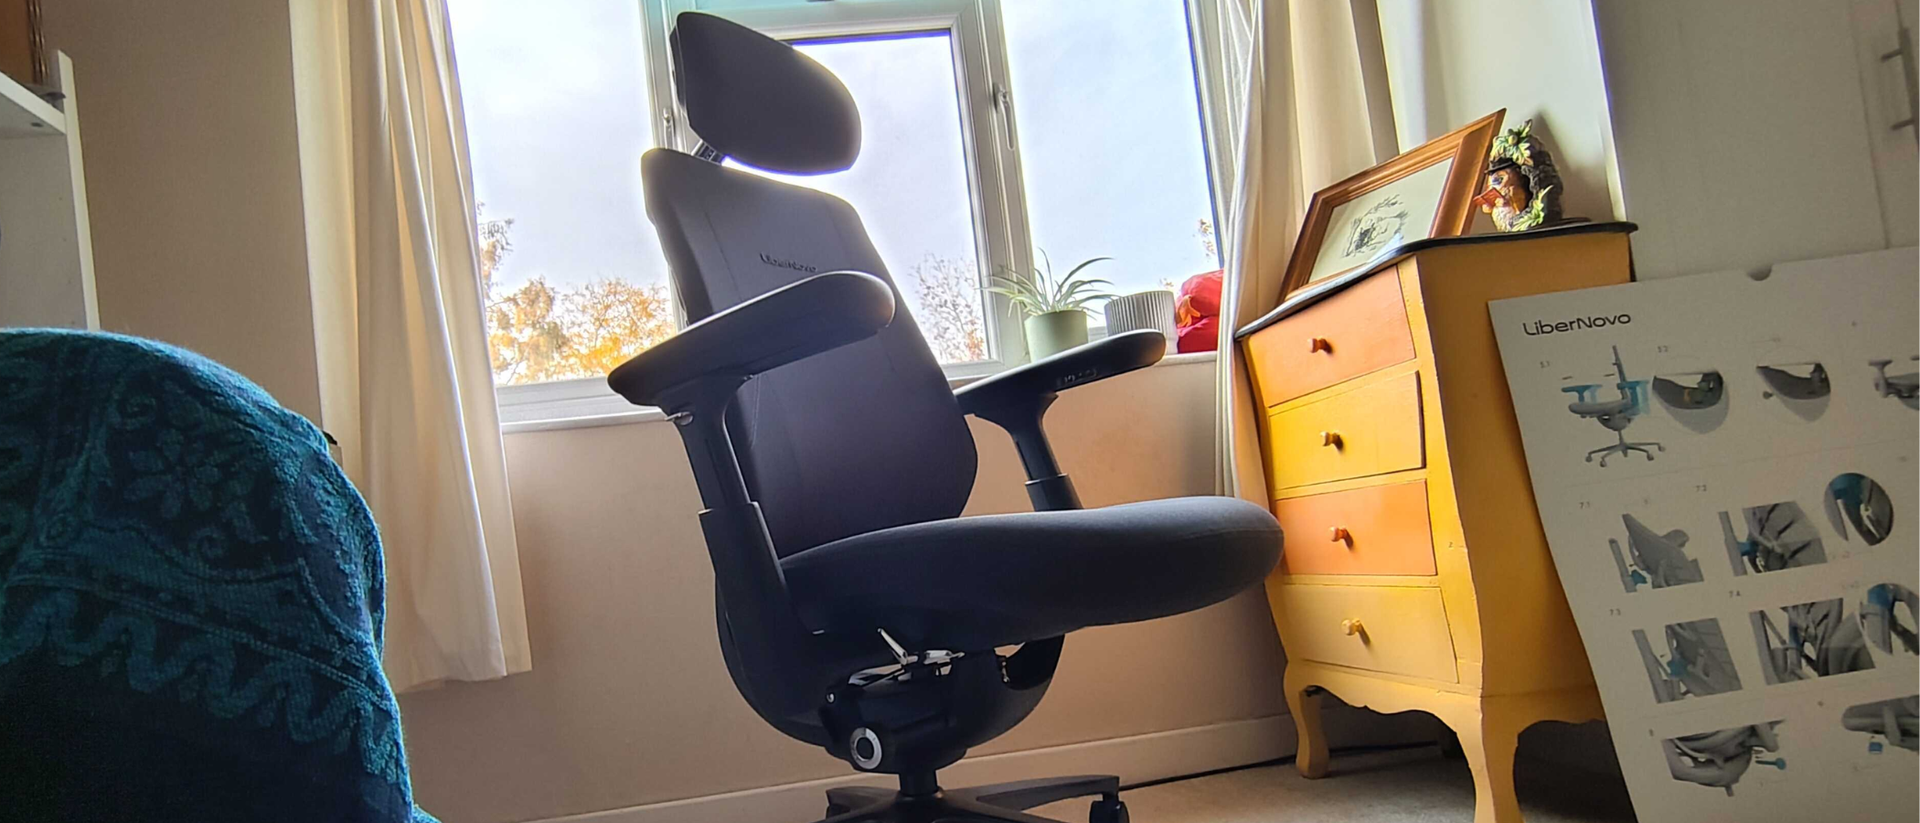
LiberNovo Maxis review: A clever and comfortable office chair for big and tall users

The LiberNovo Maxis is a chair specifically engineered for big and tall users - and it packs in a raft features. But the premium price may make you think twice.
LiberNovo Maxis review: A clever and comfortable office chair for big and tall users

The LiberNovo Maxis is an office chair designed for users who are 5'10" to 6'7" tall, with a reinforced frame capable of supporting up to 399 lbs. It features a motorized lumbar support system, a bionic FlexFit backrest, a built-in fan, and an OmniStretch massager for relieving tension. The chair is available in different models, including the Airflow, which has a cooling fan and enhanced lumbar adjustments.

Priced at $1299 US or £1099 UK, the Maxis is positioned in the premium price bracket alongside brands like Herman Miller and Steelcase. Despite its high cost, the chair is praised for its build quality, stylish design, and exceptional comfort, making it an ideal choice for big and tall professionals seeking all-day comfort and top-tier features.

Written by urgent.news from TechRadar's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.
Read the original at techradar.com →

More in Tech

OAuth for MCP: A Reference Architecture

OAuth integrations for MCP become confusing when the MCP server is expected to be everything at once: resource server, login page, token issuer, and client registry.

  • MCP server handles multiple roles, risking loss of trust boundaries in OAuth integrations
  • Four distinct roles: MCP client, authorization server, access token, and MCP protected resource
  • Metadata from RFC 9728 and RFC 8414 guides client to authorization and token endpoints

After the Drupal Gin Patch: Preventing CVE-2026-110738 Regressions

After the Drupal Gin Patch: Preventing CVE-2026-110738 Regressions The day after a Drupal security update is when regressions tend to appear.

  • CVE-2026-110738 vulnerability mitigated in Gin versions 4.1.4 and 5.0.16
  • Post-patch monitoring essential to detect regression of security flaw
  • Validate installed package, record container image digest for containerized deployments

More from Wednesday 28 October →