Japan's GMO Offers $1 Million Bounty to Catch Hackers Behind FX Trading Cloud Breach
Japan's GMO Internet Group is offering up to $1 million in total for tips that help catch the attackers who breached its Onamae.com Desktop Cloud service, after refusing to pay an extortion demand. The reward program opened on October 28 and pays only if a tip helps lead to an arrest or an international wanted notice. The service hosts Windows desktops used for FX trading,
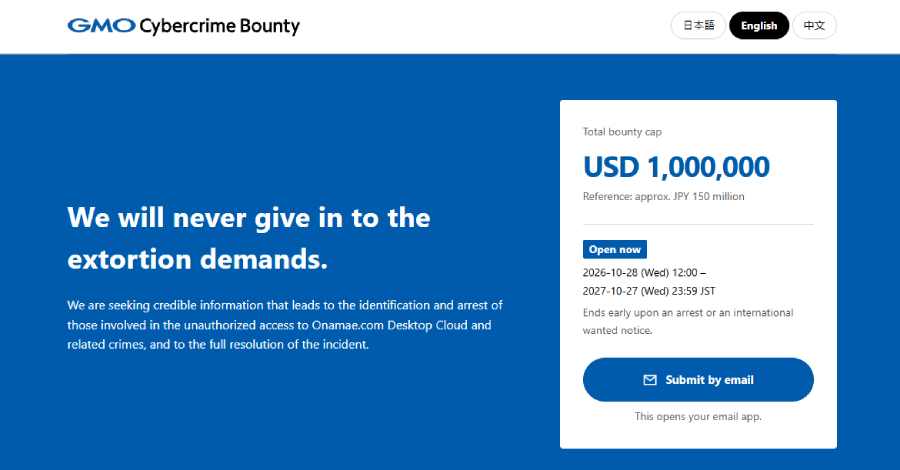
GMO Internet Group is offering a substantial reward of up to $1 million to help apprehend the hackers responsible for breaching its Onamae.com Desktop Cloud service. The company refused to pay an extortion demand of about $50 million (around ¥8 billion) and opened the bounty program on October 28. The service hosts Windows desktops used for foreign exchange trading, and unauthorized trades linked to leaked login credentials have been traced back to the breach.
GMO claims that attackers stole customer data and threatened trading accounts and information. On October 27, the hackers posted details about GMO and its customers on their website, which was subsequently taken down. The bounty program, called GMO Cybercrime Bounty, accepts tips in Japanese, English, or Chinese through an email address listed on a dedicated website.
Tips can remain anonymous, and the program remains open until an arrest, international wanted notice, or October 27, 2027. Tips are only eligible for rewards if they lead to an arrest or international wanted notice. GMO will determine the value of each tip and may split the $1 million reward among multiple tipsters. To receive payment, tipsters must prove their identity, and certain individuals, such as those involved in the crime or those who obtained information illegally, will not be eligible for payment.
GMO advises against breaking into systems, negotiating with or paying the attackers, or sharing leaked data, credentials, or malware. The company has already provided all relevant evidence to the police and intends to take action against any new sites that may emerge. GMO discovered on October 20 that a third party had installed malware on some customers' servers, which were subsequently shut down.
Approximately 26,739 servers are potentially affected, though this does not equate to confirmed breaches or data thefts. Customers have reported unrecognized trades since October 21, and a broker, OANDA Japan, has restricted trading on potentially affected accounts. Another broker, FXTF, warned of potential theft of login credentials from VPS servers, which may have been used to access customers' accounts. GMO has not yet confirmed the extent of the breach's impact on its other services.
Written by urgent.news from The Hacker News's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.