Anthropic's Unreleased AI Model Chains Flaws Into Working Chrome, Safari, Windows and Linux Exploits
An unreleased Anthropic AI model found security flaws in Chrome, Safari, Android, Windows, and Linux and chained them into working proof-of-concept exploits, the company said in its latest report. The exploits were built in the lab after the model was prompted, not seen in any real attack, and Anthropic reported every flaw to the vendor first, so all of them are already patched. One proof of
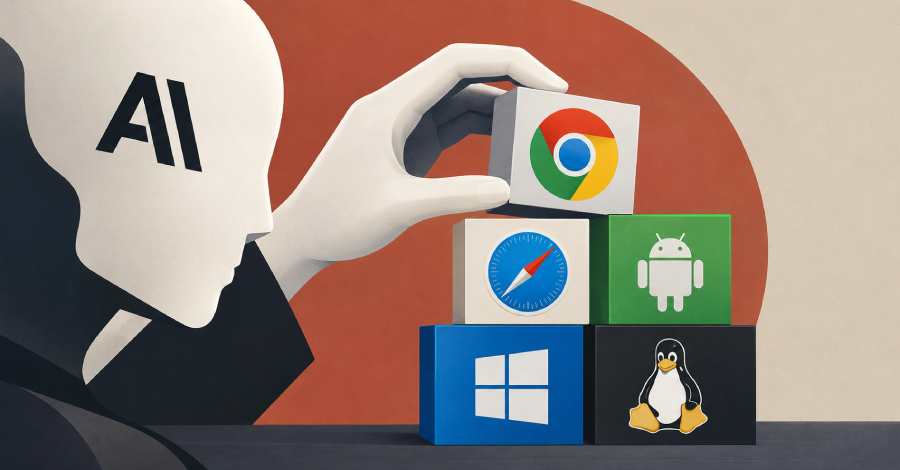
Anthropic's unreleased AI model discovered security flaws in Chrome, Safari, Android, Windows, and Linux, and combined them into working proof-of-concept exploits, according to the company's latest report. These exploits were not observed in real-world attacks but were created in a lab setting after the model was prompted. Anthropic promptly reported all discovered flaws to the respective vendors, which have since been patched.
The company's Frontier Red Team detailed five chains of exploits in a research post, with the strongest claim being that one model identified multiple bugs and combined them into a functional exploit, a feat typically requiring specialized teams. However, Anthropic cannot confirm the extent of the model's contribution to each chain, only that it required minimal human intervention.
One of the flaws was publicly attributed to Windows in CVE-2026-33096, but the description does not match the component referenced. The Linux chain is considered the most impactful, allowing root access over the network on servers running multipath TCP. Anthropic frames its research as aiding defenders and provides resources for strengthening security operations against such AI-driven threats.
Written by urgent.news from The Hacker News's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.