Amazon ECS Gateway: managed, shared ingress for ECS services (and the traps to avoid)
Originally published in Spanish on CloudAcademy.ar . On October 20, 2026, AWS launched Amazon ECS Gateway , an account-level resource that owns ingress for your ECS services. Instead of every service carrying its own Application Load Balancer, listener, target group, security group and certificate, a platform team defines a gateway once and services opt in with a single parameter on…
Amazon recently introduced Amazon ECS Gateway, a managed service ingress solution for ECS services. Instead of each service requiring its own Application Load Balancer, this new feature allows a platform team to define a gateway once and have services connect to it. Up to 25 services can share a single ALB via host-based routing.
The gateway provisions all necessary resources, including ALBs, HTTPS listeners, target groups, security groups, and ACM certificates. Each service is assigned a unique URL in the format https://unique-id.ecs.region.on.aws. HTTPS traffic on port 443 is supported, and the gateway only works within the same account. There is no cost for the gateway itself, but charges apply for ALBs, public IPv4, logs, metrics, and data transfer.
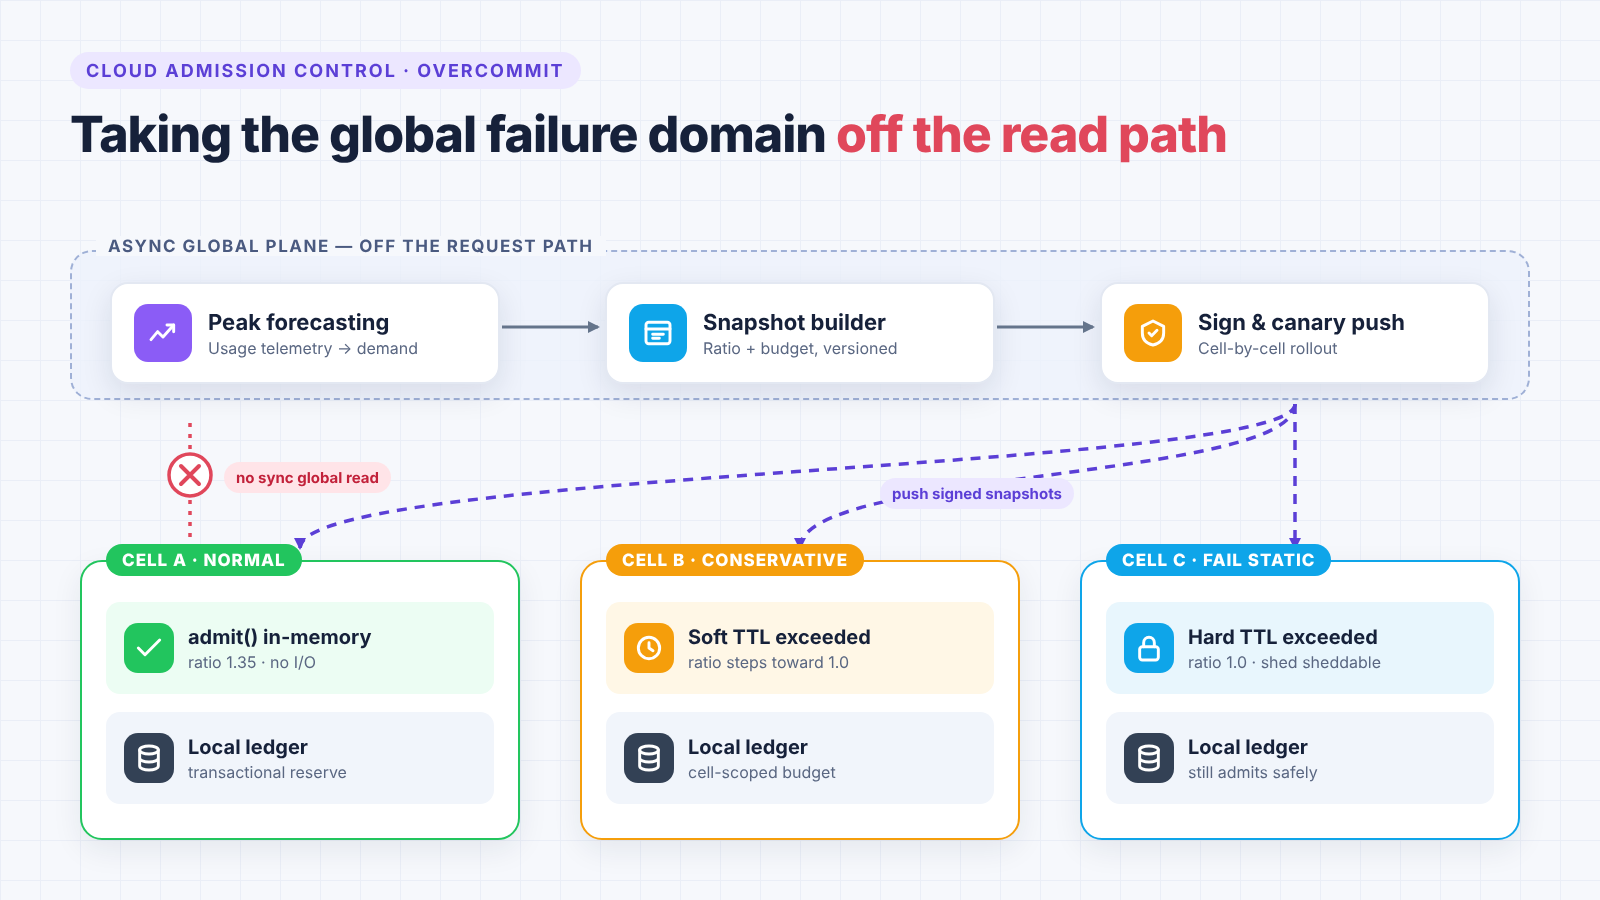
The gateway can only be used in regions where ECS runs, and it has some limitations, such as only supporting EC2, Fargate, and ECS Managed Instances in awsvpc network mode. One significant trap is that updating the gateway replaces the entire configuration. The architecture involves a platform declaring ingress, each service getting a route on a shared ALB, and a gateway connector connecting the service to the gateway.
Services are connected to gateways based on compatibility rules, including filters for internet-facing or internal access, matching VPCs, and availability zones. If the service requires internal access, a PRIVATE filter must be used to prevent exposure when an internet-facing gateway is added later.
Written by urgent.news from Dev.to's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.