UK pentester 'killa' claims $2K Bitcoin prize in PHP2Shell capture-the-flag contest
Jaydip Modhwadia beats challenge designed to test real-world exploitability of PHP2Shell in around 3 hours
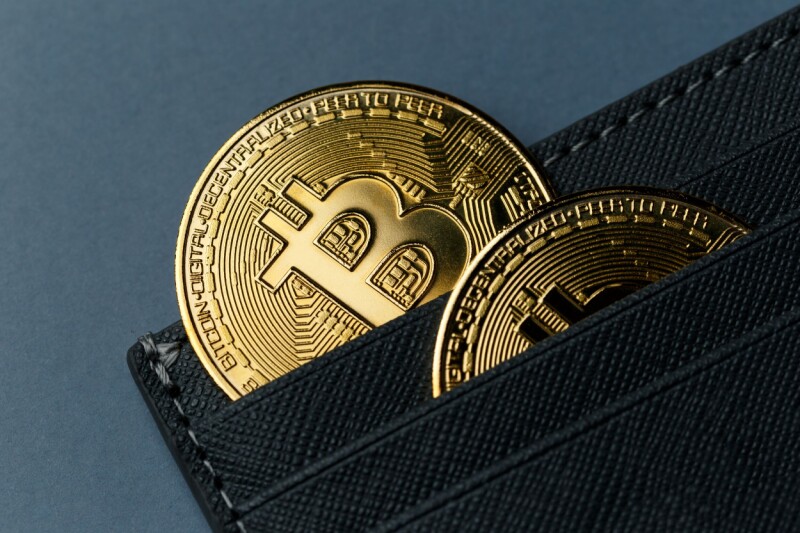
A 26-year-old UK developer, identified as Jaydip Modhwadia or "Killa," has been awarded a $2,000 Bitcoin prize for successfully exploiting the PHP2Shell vulnerabilities in a recent Capture The Flag (CTF) contest. The challenge, initiated by James Pavur on October 24 through the site "Steal My Bitcoin," aimed to demonstrate that the PHP2Shell exploit was not as straightforward as initially believed.
Modhwadia achieved the required Remote Code Execution (RCE) on the website in just three hours after the contest began, despite initial skepticism from the cybersecurity community regarding the exploit's feasibility. The website's owner, Pavur, later increased the prize to $2,000 after an error with the Bitcoin wallet key. Modhwadia provided a write-up detailing his approach, which involved a single Python script with a maximum of 20 HTTP requests.
Despite the site becoming unusable due to high traffic, Modhwadia's success highlights the exploitability of PHP2Shell, even with technical constraints in place. Experts have praised Modhwadia's work, noting that while it demonstrates the exploit's potential, it does not imply that the attack can be automated at scale.
Written by urgent.news from The Register's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.
This story
This is one outlet's version. Read the fullest account.