Korean Air breach exposes blind spot in airline cybersecurity
A recent data breach involving Korean Air and Asiana Airlines demonstrates the aviation industry’s structural vulnerability to cyberattacks targeting third-party IT providers. Carriers depend on external IT system operators to manage critical operations, as they have to share passenger booking and ticketing data with external partners for real-time global operation. Last week, Korean Air and…
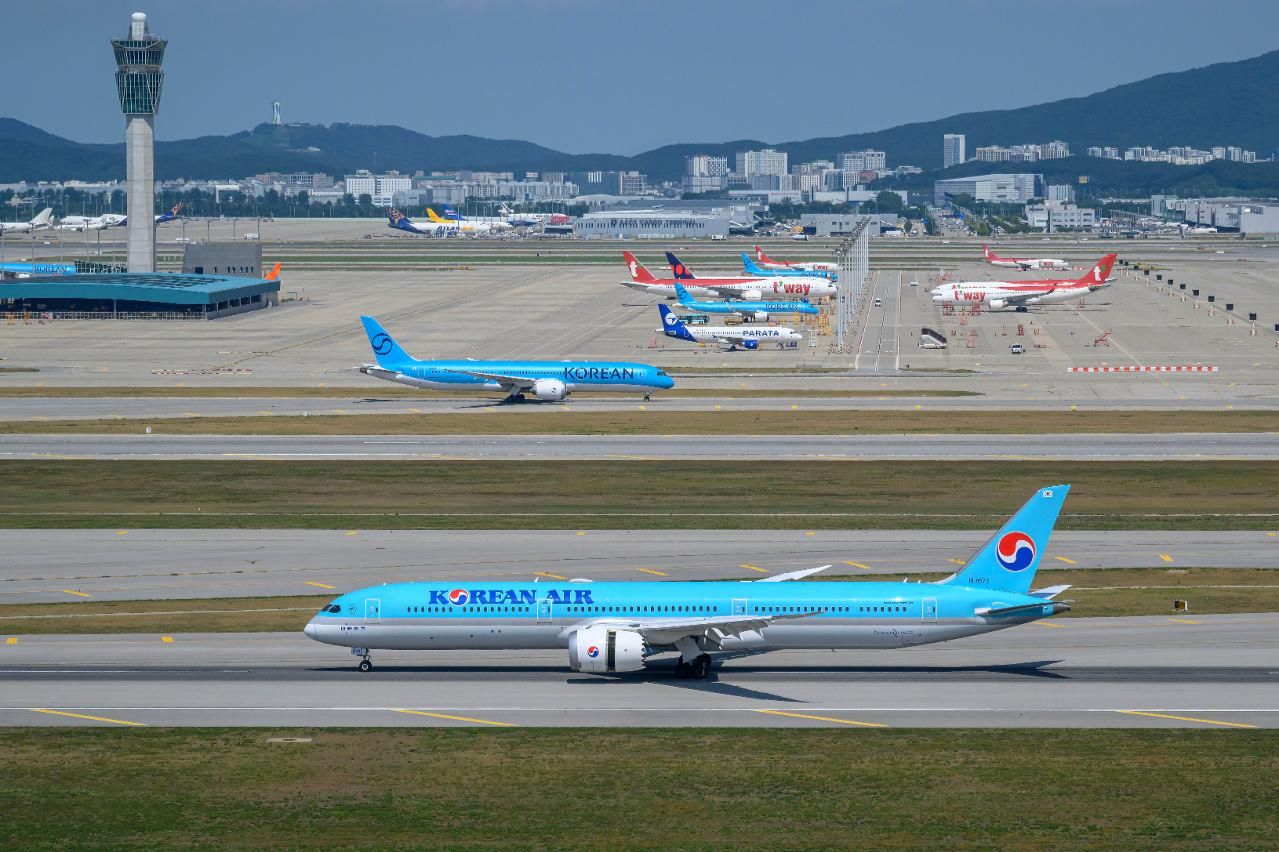
The Korea Times reports on a data breach affecting Korean Air and Asiana Airlines, highlighting the industry's reliance on third-party IT providers and the associated cybersecurity risks. The breach occurred due to unauthorized access using login credentials assigned to an account within Amadeus IT Group, a global aviation technology provider.
Korean Air and Asiana Airlines learned of the incident on Tuesday, and it is believed that the unauthorized access took place between August 2023 and the recent past. The breach resulted in the exposure of customer booking reference numbers, though the full extent of the leak and the total number of affected customers remain undisclosed.
This incident underscores the structural vulnerabilities faced by airlines in managing critical operations through external IT system operators, emphasizing the need for enhanced cybersecurity measures in the aviation sector.
Brief written by urgent.news from The Korea Times's own syndicated text. Machine-written — may contain errors; check the original before relying on it.
This story
This is one outlet's version. Read the fullest account.
- Korean Air breach exposes blind spot in airline cybersecurity koreatimes.co.kr