Switch 2 security takes a hit as hackers unlock homebrew access
"Userland" exploit relies on integer overflow found in "SmileBasic" interpreter.
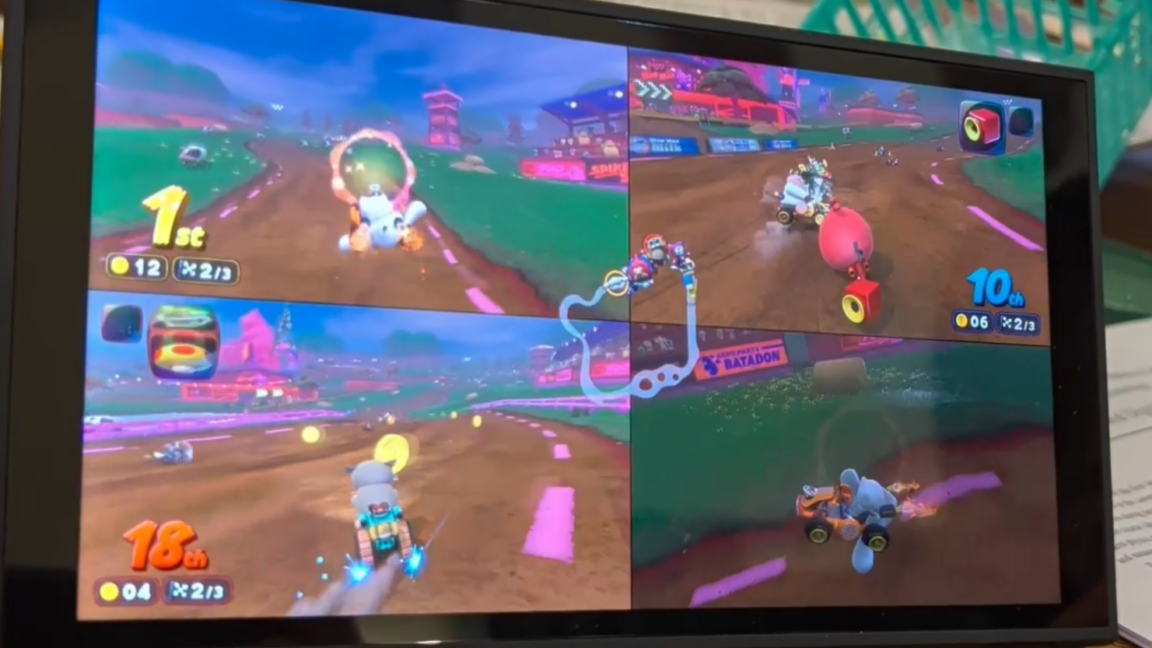
A security researcher has unveiled a software-based jailbreak for the Switch 2, granting userland access to the device. This capability allows for running homebrew applications, reverse engineering, and modifying Switch 2 games. The hack also enables backup of save files and access to various peripherals through MMIO. The technique relies on the original SmileBasic 4 version, a programming environment that operates on Nintendo hardware.
The hack is considered "tethered," meaning it requires access to a macOS or Linux PC on the same network to execute a node.js package that grants privileged system access. The researcher utilized OpenAI's Codex to manipulate SmileBasic's language interpreter, employing a custom harness that transmitted USB commands, viewed results via HDMI, powered cycles via a Bluetooth light switch, and ultimately identified a 32-bit integer overflow during the removal of items from an array in SmileBasic.
This vulnerability provides access to an array pointer, facilitating read and write access to portions of system memory.
Written by urgent.news from Ars Technica's reporting — not their text. Machine-written — may contain errors; check the original before relying on it.